
Cookie Manager Tarteaucitron — Complete guide
Installation, wizard, automatic blocking of third-party scripts, cookie list, service catalogue, appearance, Google Consent Mode v2, scan, statistics and proof of consent for the Cookie Manager (tarteaucitron.js) module for PrestaShop 1.7.8, 8 and 9.
Overview
Cookie Manager is a cookie consent management module for PrestaShop 1.7.8, 8 and 9, compatible with the Classic and Hummingbird themes. It is built on tarteaucitron.js 1.37.0, the open-source library by Amauri Champeaux (MIT licence). The module adds its own cookie banner, automatic blocking of third-party scripts, a cookie list generated for your visitors, Google Consent Mode v2 and a proof-of-consent log.
Until the visitor has made a choice, the module sets no cookies, writes nothing to browser storage and contacts no third party. The cookie that remembers the choice is only written on the first click.
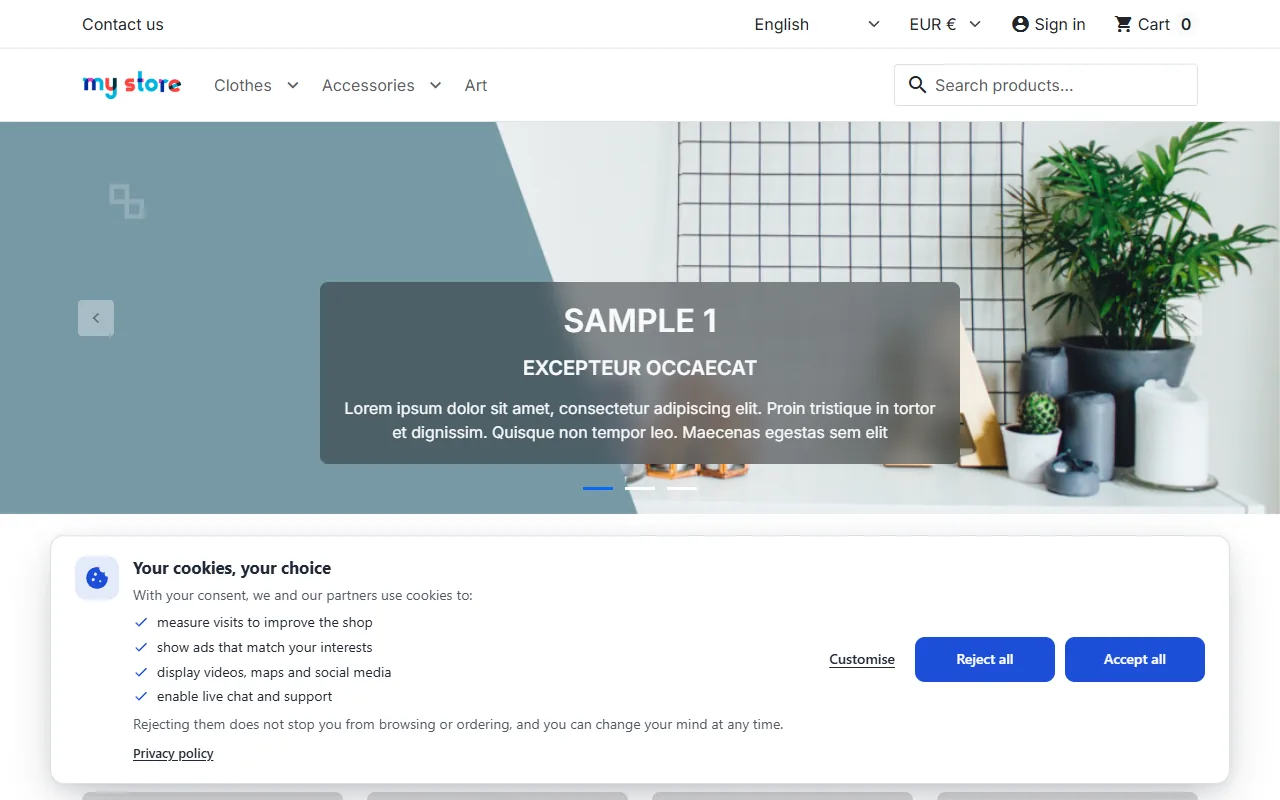
Installation and setup wizard
- In the back office, open Modules → Module Manager → Upload a module.
- Drop the file
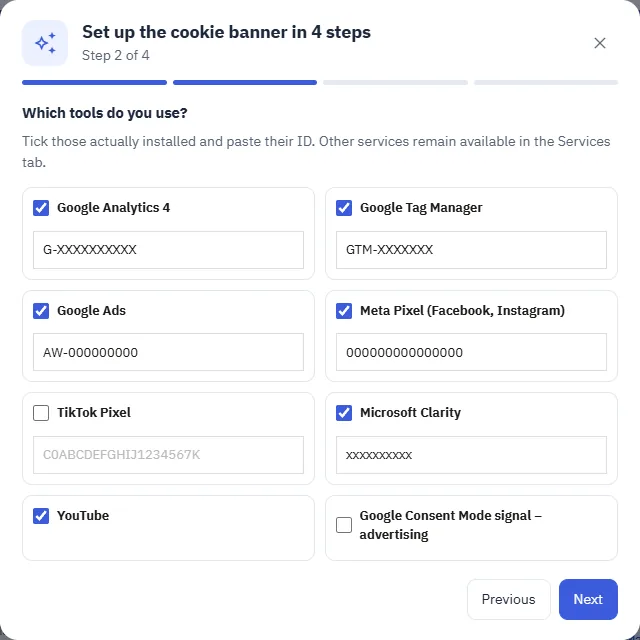
datafirefly_tarteaucitron-3.0.0.zip, then click Configure. - The wizard opens the first time the page is displayed: privacy policy, tools used and their IDs, appearance, enabling the cookie banner.
The configuration is also accessible from the Modules → Cookies (tarteaucitron) menu entry. The wizard can be relaunched at any time using the Wizard button at the top of the page.
Upgrading from version 2.0 or 1.x
Upload the new zip over the old module. The upgrade script carries over your settings: services and IDs, texts, colours, position, duration, Consent Mode, log, statistics and custom services.
- The choice your visitors have already made with 2.0 is kept: the cookie banner is not shown to them again, unless you add a service.
- Automatic blocking stays disabled after an upgrade. Enable it in the Blocking tab, then test your pages.
- From 1.x, the single value of each text is copied into every language of the shop, and the “Continue without accepting” label becomes “Reject all”.
On a fresh installation, automatic blocking is enabled by default.
Dashboard
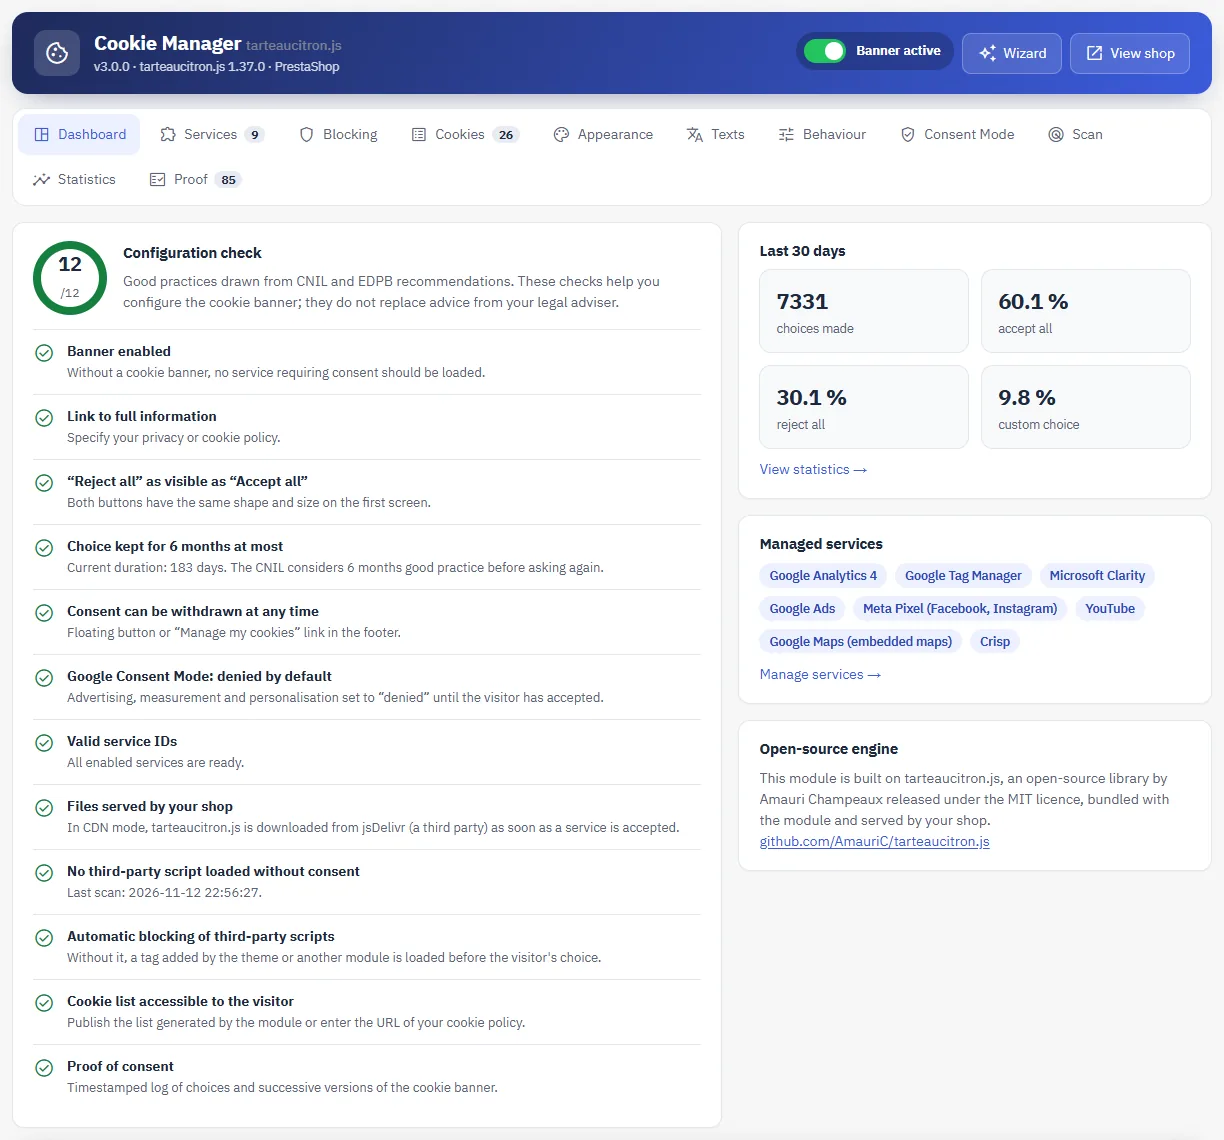
The dashboard brings together twelve configuration checks: cookie banner enabled, link to the privacy policy, “Reject all” and “Accept all” buttons with the same appearance, choice duration, means of withdrawal, Consent Mode default values, valid IDs, files served by the shop, third-party script scan, automatic blocking, cookie list accessible to the visitor and proof-of-consent log. Each unmet item offers a Fix link to the relevant tab.
These checks reflect good practice drawn from CNIL and EDPB recommendations. They help you configure the cookie banner but do not replace a legal analysis of your site.
Services
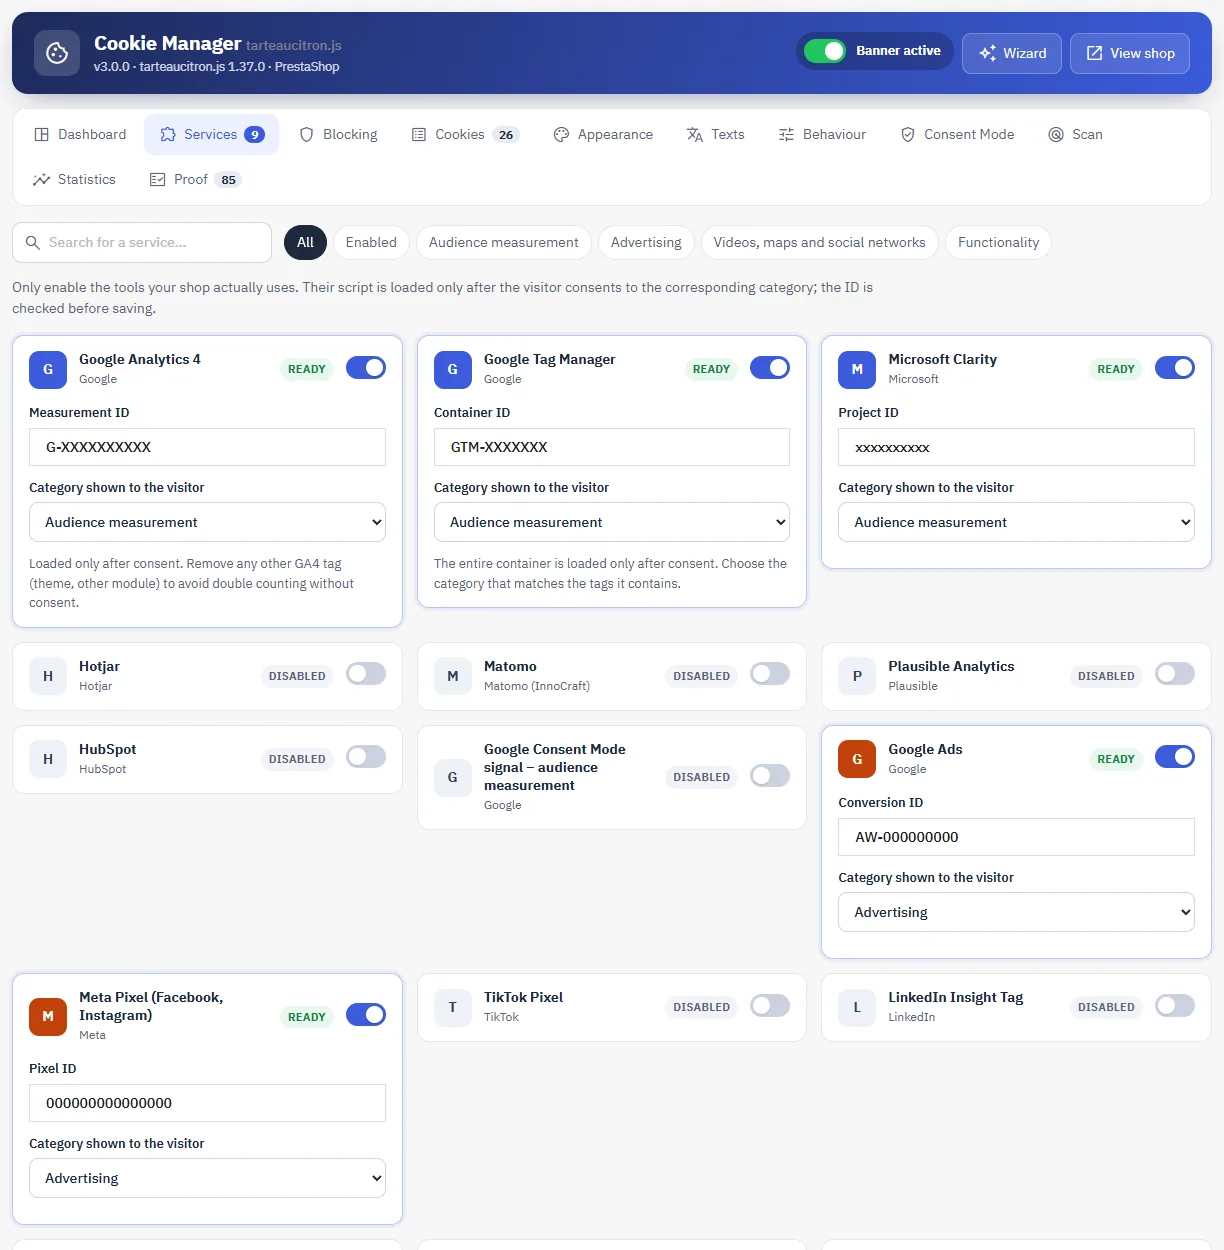
The Services tab presents the verified catalogue: Google Analytics 4, Google Tag Manager, Google Ads, Meta Pixel, TikTok, LinkedIn Insight, Pinterest, Snap Pixel, Microsoft Advertising, Microsoft Clarity, Hotjar, Matomo, Plausible, HubSpot, YouTube, Vimeo, Google Maps, Intercom, Crisp, Tawk.to, Smartsupp and Stripe, as well as two script-free Google Consent Mode signals, for a Google tag installed by another module.
- Only enable the tools actually present on your shop and paste their ID: its format is checked as you type, then again on saving. An invalid ID is rejected and the service stays disabled.
- Each service can be assigned to a category other than the one suggested, for example Google Tag Manager under “Advertising” if your container mainly holds advertising tags.
- Matomo and Plausible can be declared exempt from consent, but only if your configuration of the tool meets the CNIL’s conditions for audience measurement.
- Stripe is treated as strictly necessary for payment: it is loaded without asking and listed among the always-active cookies.
Custom services: for a tool missing from the catalogue, add a service with its name, category, privacy policy, cookies and the code provided by the tool (including <script> tags). This code only runs after the visitor has consented to the chosen category.
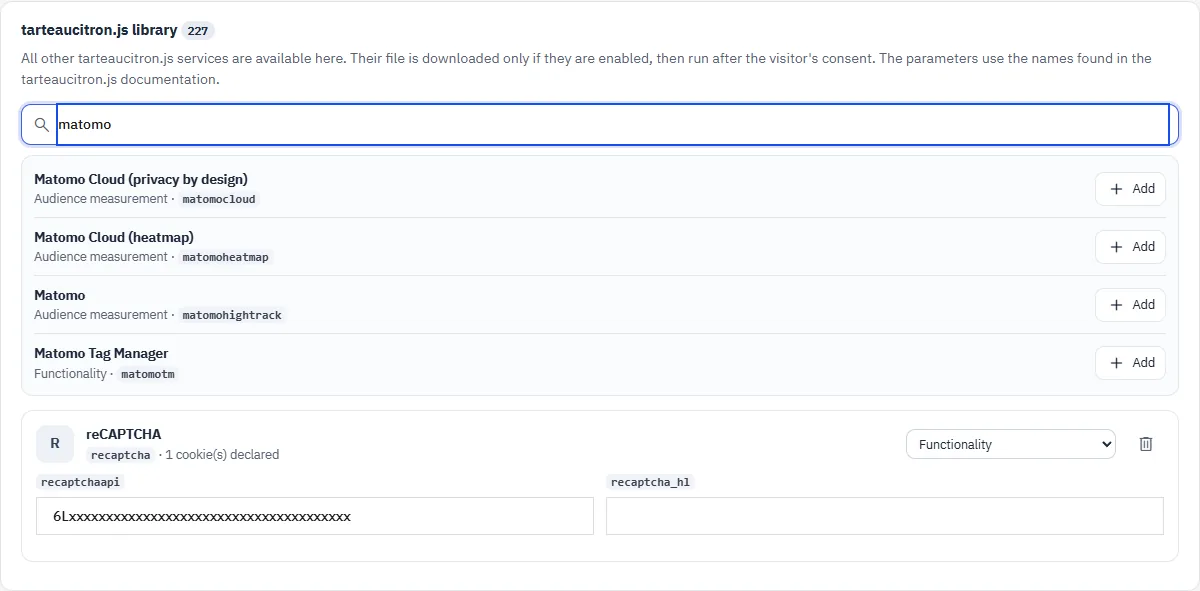
tarteaucitron.js library: the 245 services of tarteaucitron.js 1.37.0 are available in addition to the catalogue. Search for a service, add it, fill in its parameters and choose its category. A service’s file is only downloaded by the visitor if the service is enabled and accepted.
Automatic blocking
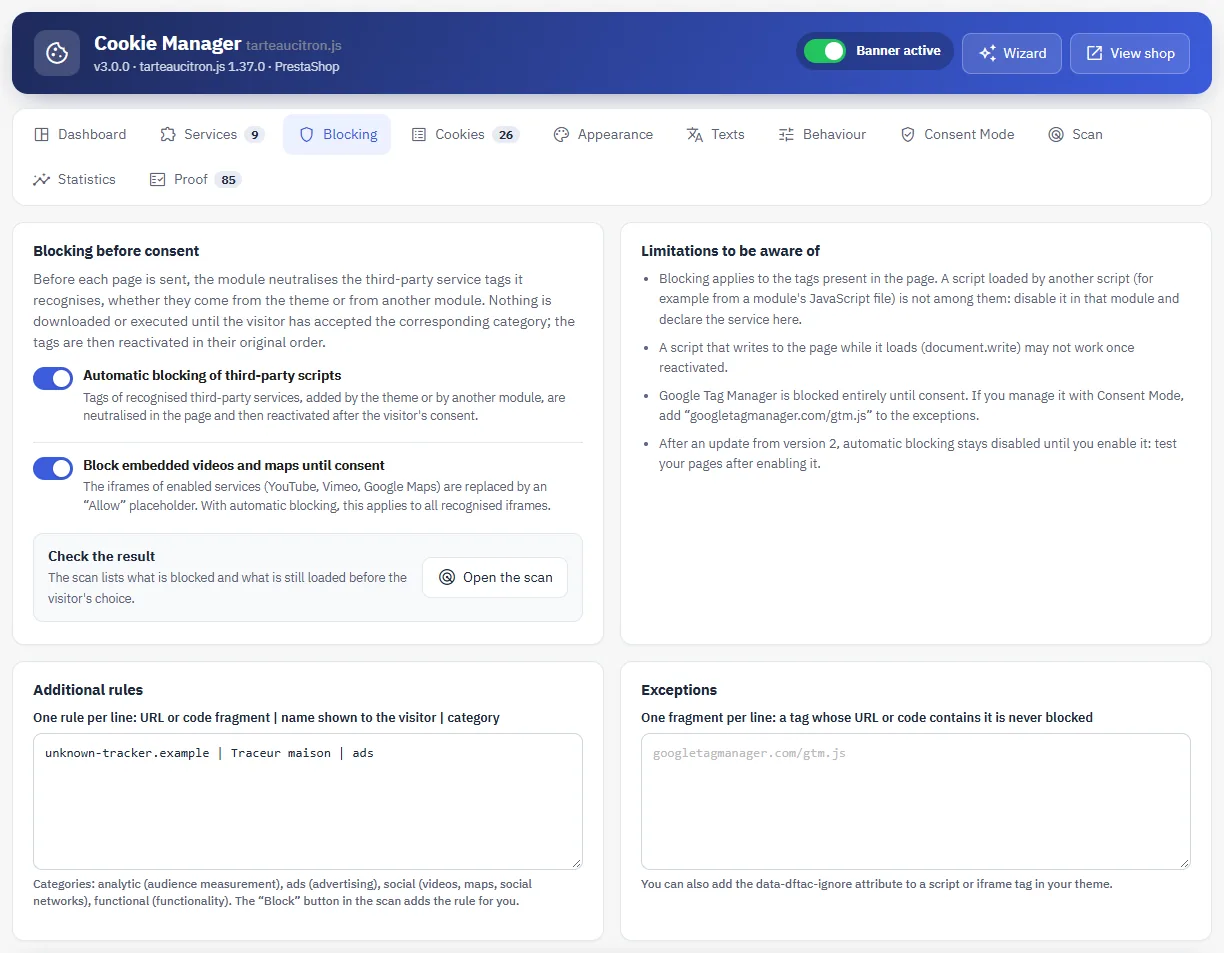
Before each page is sent, the module neutralises the <script> tags and iframes of the third-party services it recognises, whether they come from the theme or from another module: 46 services (those in the catalogue and 24 other common trackers), plus your own rules. Nothing is downloaded or executed until the visitor has accepted the corresponding category; the tags are then reactivated in document order.
- Additional rules: one rule per line, in the format
URL or code fragment | name shown to the visitor | category. The categories areanalytic,ads,socialandfunctional. The “Block” button in the scan adds the rule for you. - Exceptions: one fragment per line; a tag whose URL or code contains it is never blocked. You can also add the
data-dftac-ignoreattribute to a tag in your theme.
Blocking applies to the tags present in the page code. A script loaded by another script (for example from a module’s JavaScript file) does not appear there: disable it in that module and declare the service here. A script that uses document.write may not work once reactivated.
Google Tag Manager is blocked entirely until consent. If you manage it with Consent Mode, add googletagmanager.com/gtm.js to the exceptions.
Cookie list
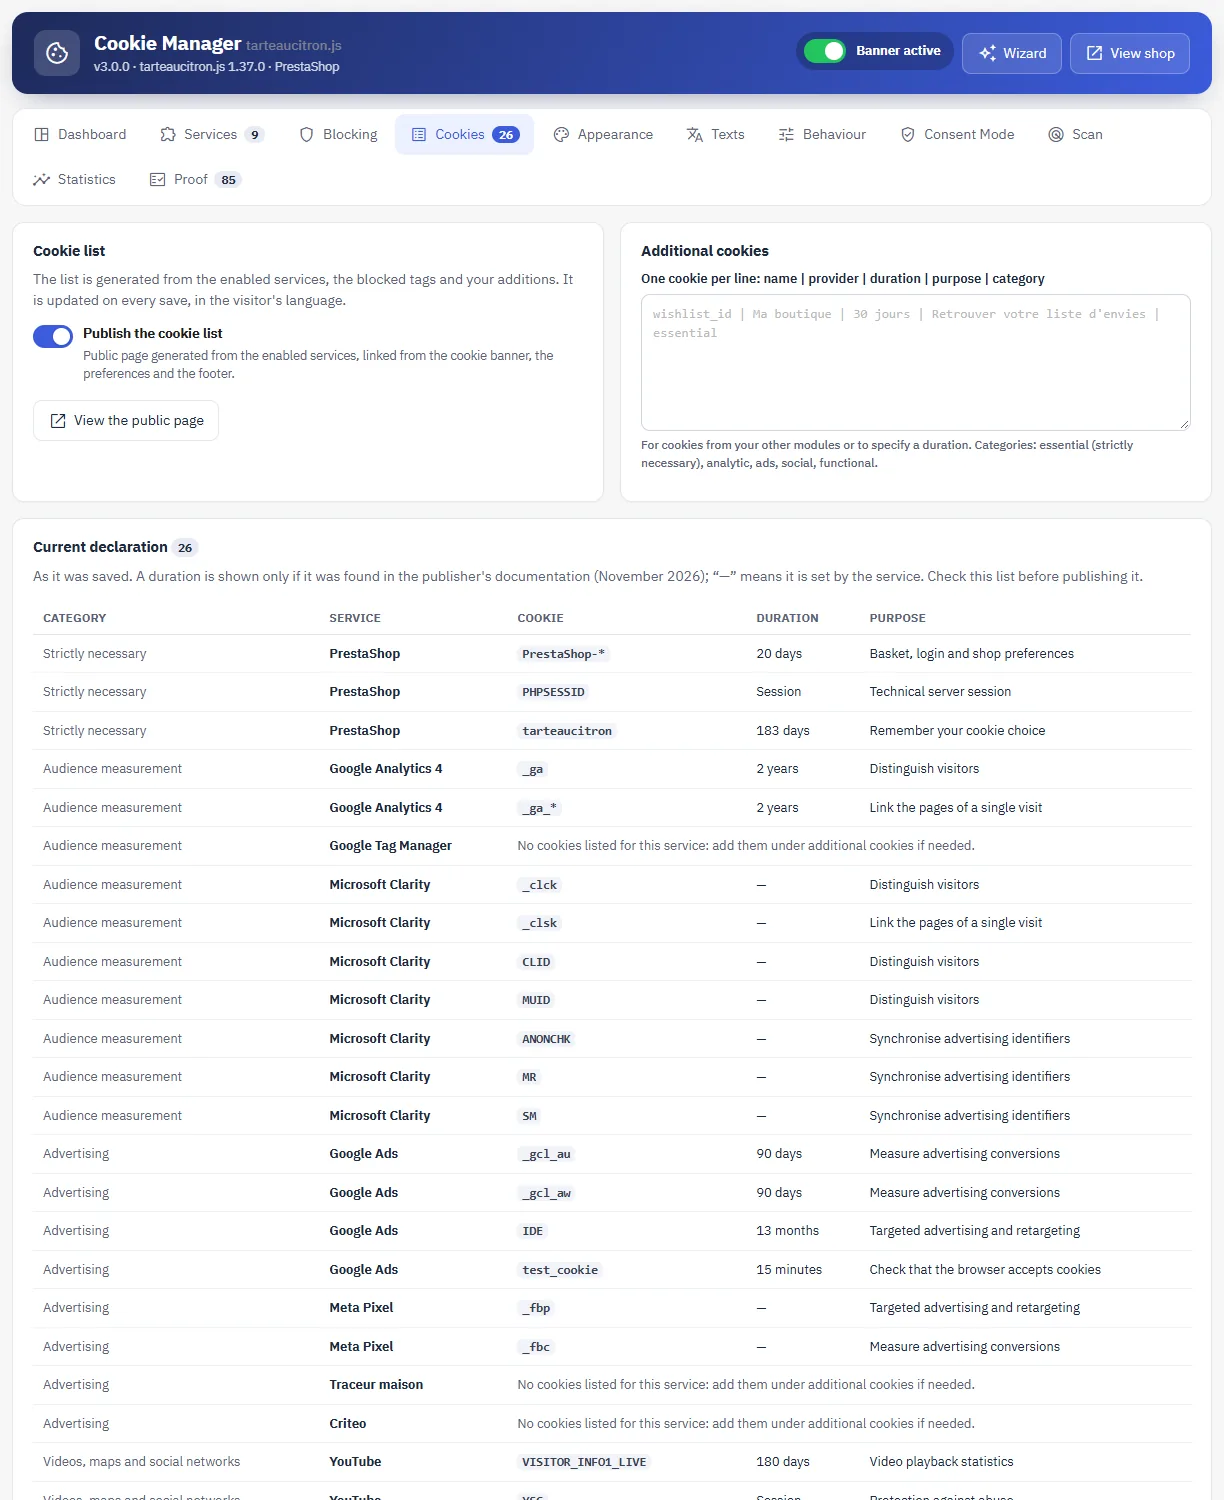
The Cookies tab generates the cookie list from the enabled services, the blocked tags and your additions: category, service, name, duration and purpose. It is updated on every save and displayed in the visitor’s language.
- Additional cookies: one cookie per line, in the format
name | provider | duration | purpose | category, for cookies from your other modules or to specify a duration. - A duration is only shown if it was found in the publisher’s documentation (November 2026); “—” means that it is set by the service.
Check this list before publishing it: it describes the services declared in the module, not those that another script might add without your knowledge.
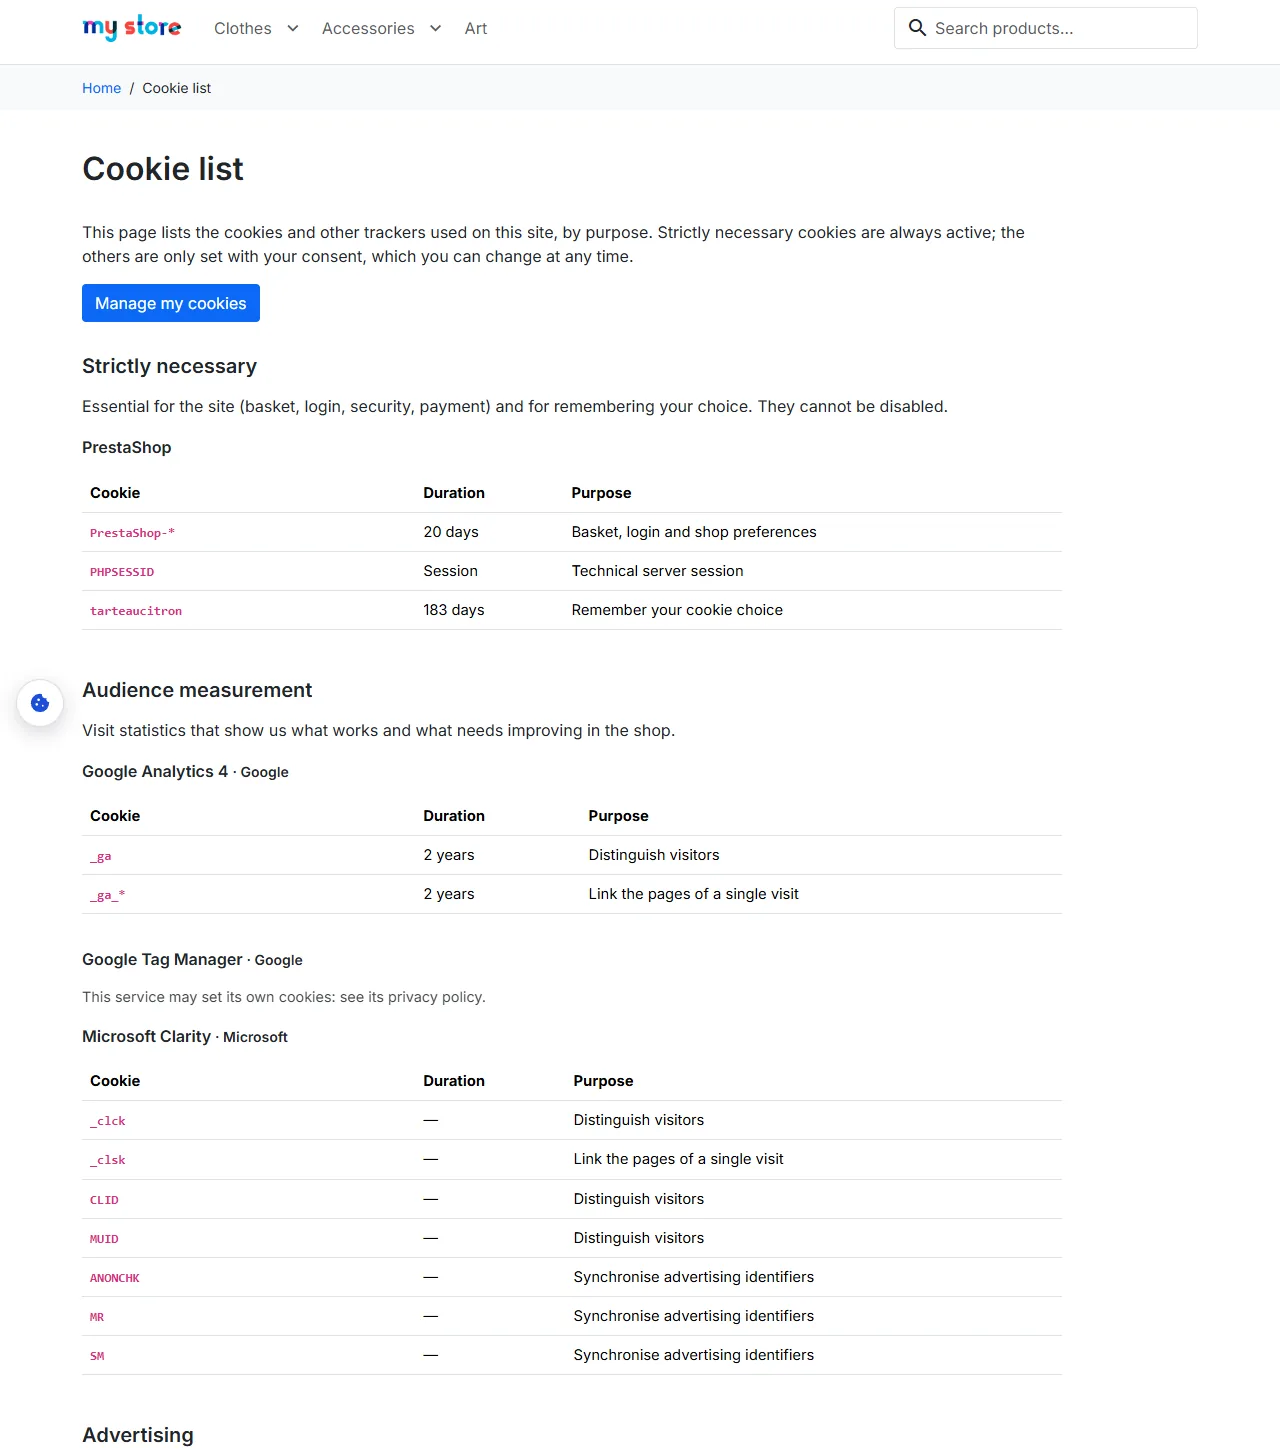
With the Publish the cookie list option (Behaviour tab), a public page is created and linked from the cookie banner, the preferences window and the footer.
Appearance
Six layouts are available: full-width bar at the bottom, card in one of the four corners or centred window. By default, “Reject all” and “Accept all” have the same shape, size and colour; an “outline” style is also available. The style that gives prominence to “Accept all” is offered with a warning, as the CNIL and the EDPB assess such differences on a case-by-case basis.
The colours (buttons, button text, background, text) come with ready-made palettes and a live contrast check, with a threshold of 4.5:1. The preview shows the real cookie banner, the preferences window or the floating button, at desktop or mobile width, in each language, including settings not yet saved.
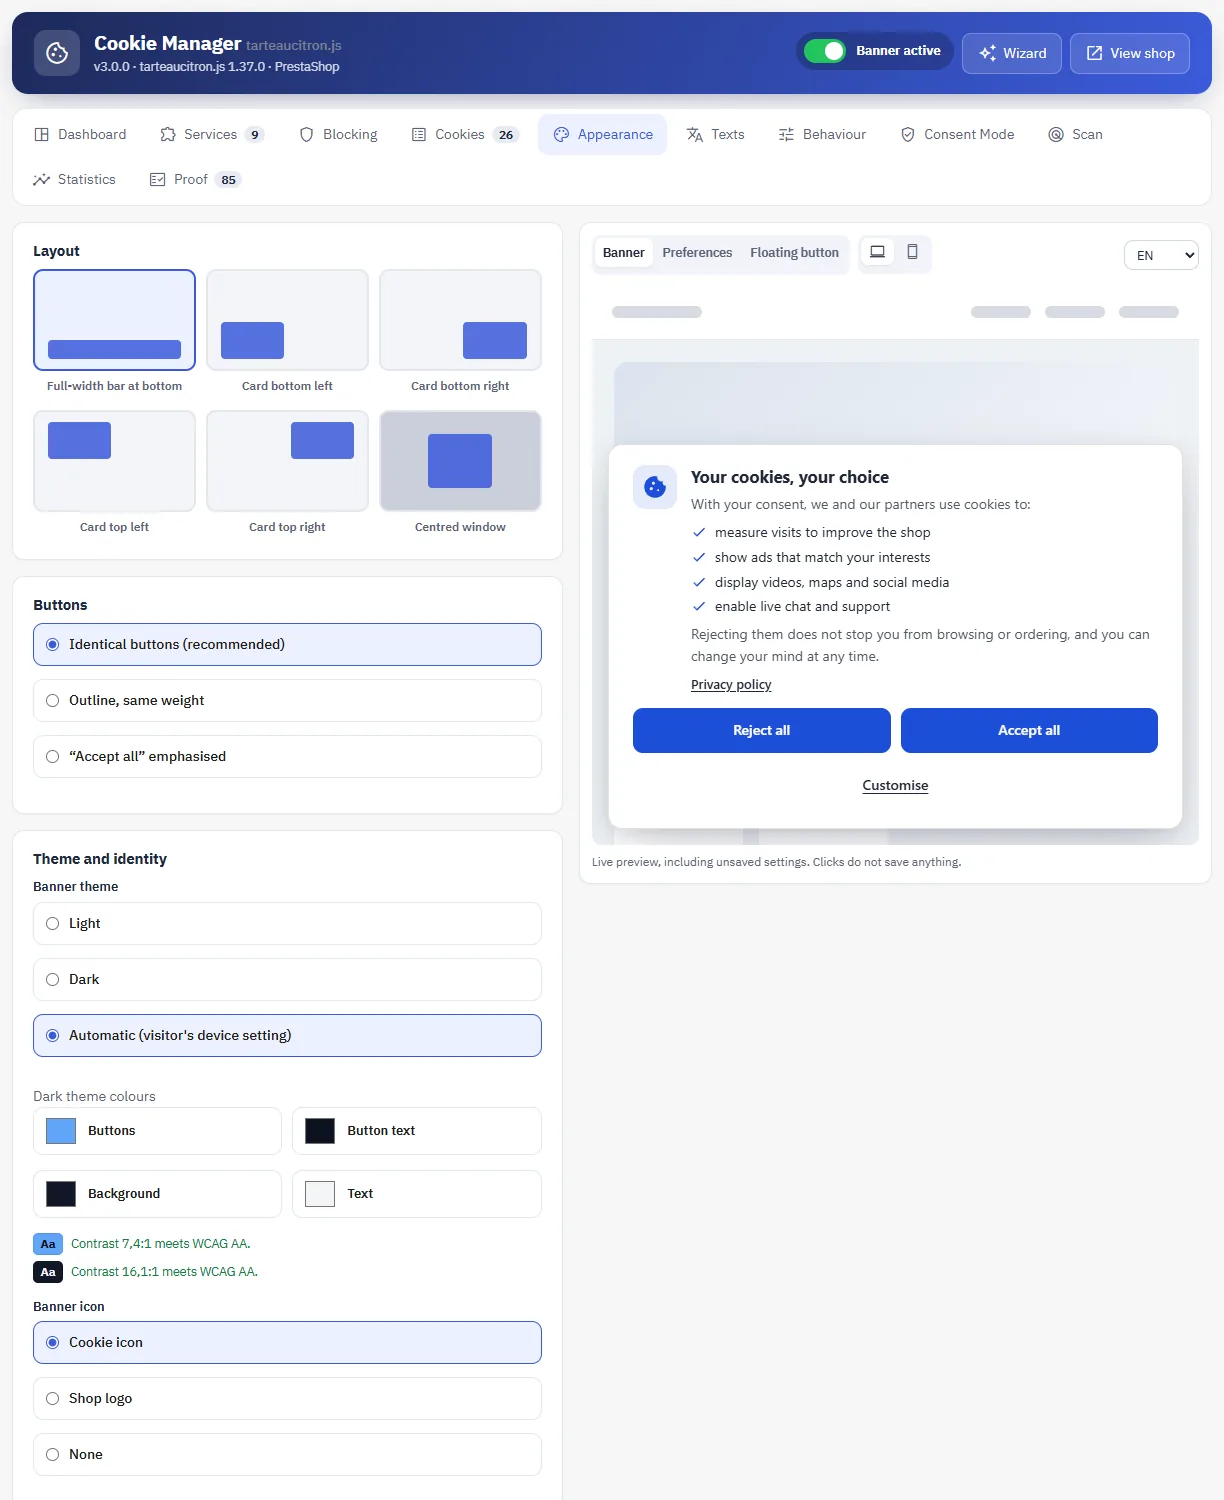
Theme and identity: light, dark or automatic theme (following the setting of the visitor’s device) with its own colours, cookie icon or shop logo, floating button position, system font or theme font, and a custom CSS field added after the cookie banner’s stylesheet.
Texts and languages
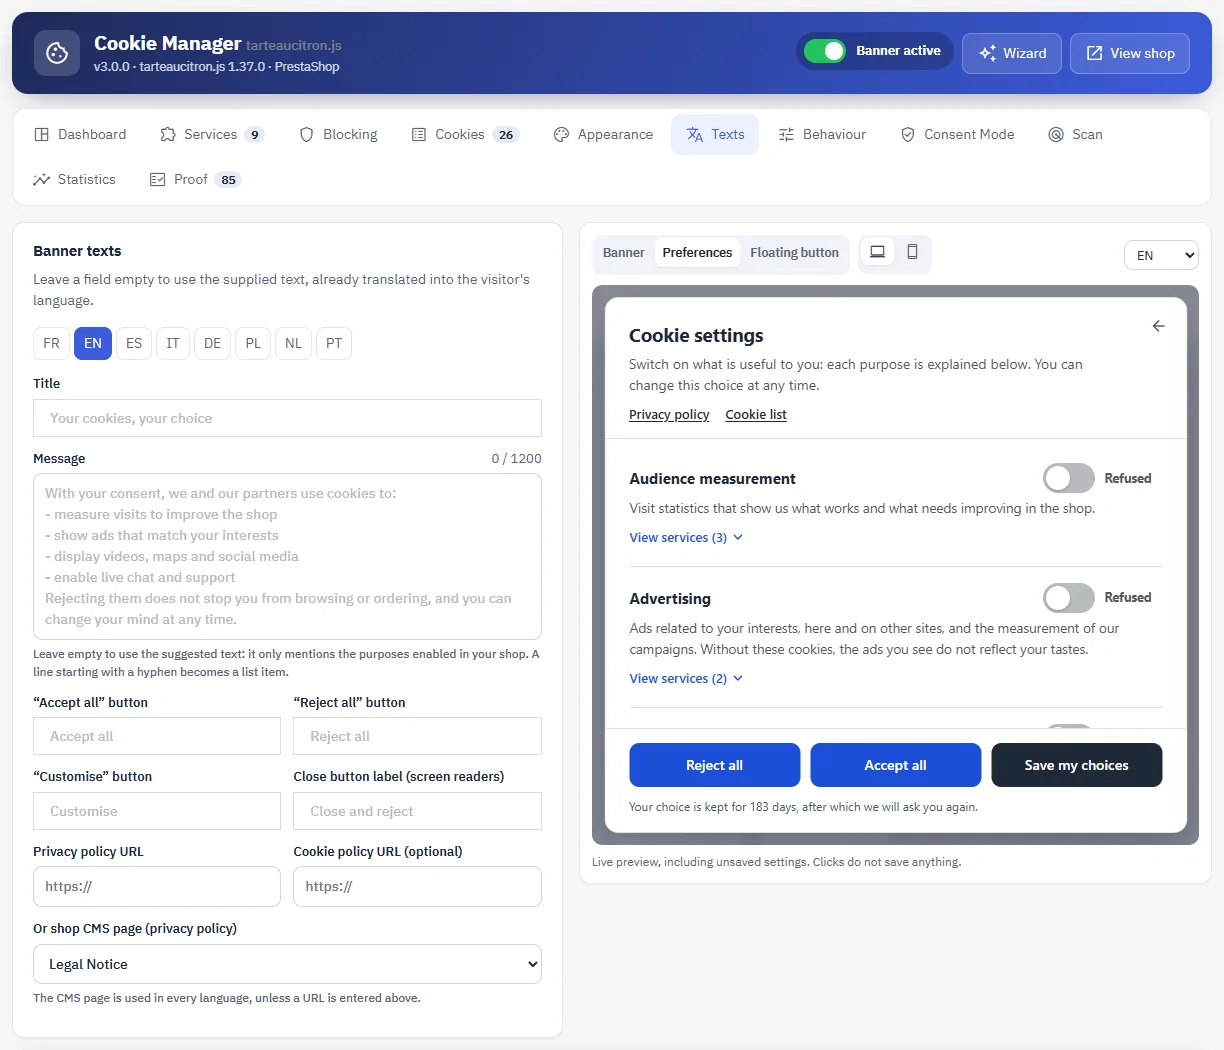
The cookie banner texts are supplied in French, English, Spanish, German, Italian, Polish, Dutch and Portuguese. The default message mentions only the purposes enabled in your shop, one line per purpose, then points out that refusing does not prevent visitors from browsing or ordering.
The Texts tab lets you replace each text language by language: title, message, button labels and the URLs of the privacy and cookie policies. A field left empty uses the supplied text. In the message, a line that starts with a hyphen becomes a list item. A CMS page of the shop can also serve as the privacy policy in all languages.
The sentence “refusing does not prevent you from ordering” is accurate with the module’s catalogue, in which Stripe is strictly necessary. If you place a payment method under consent, adapt the message.
Behaviour
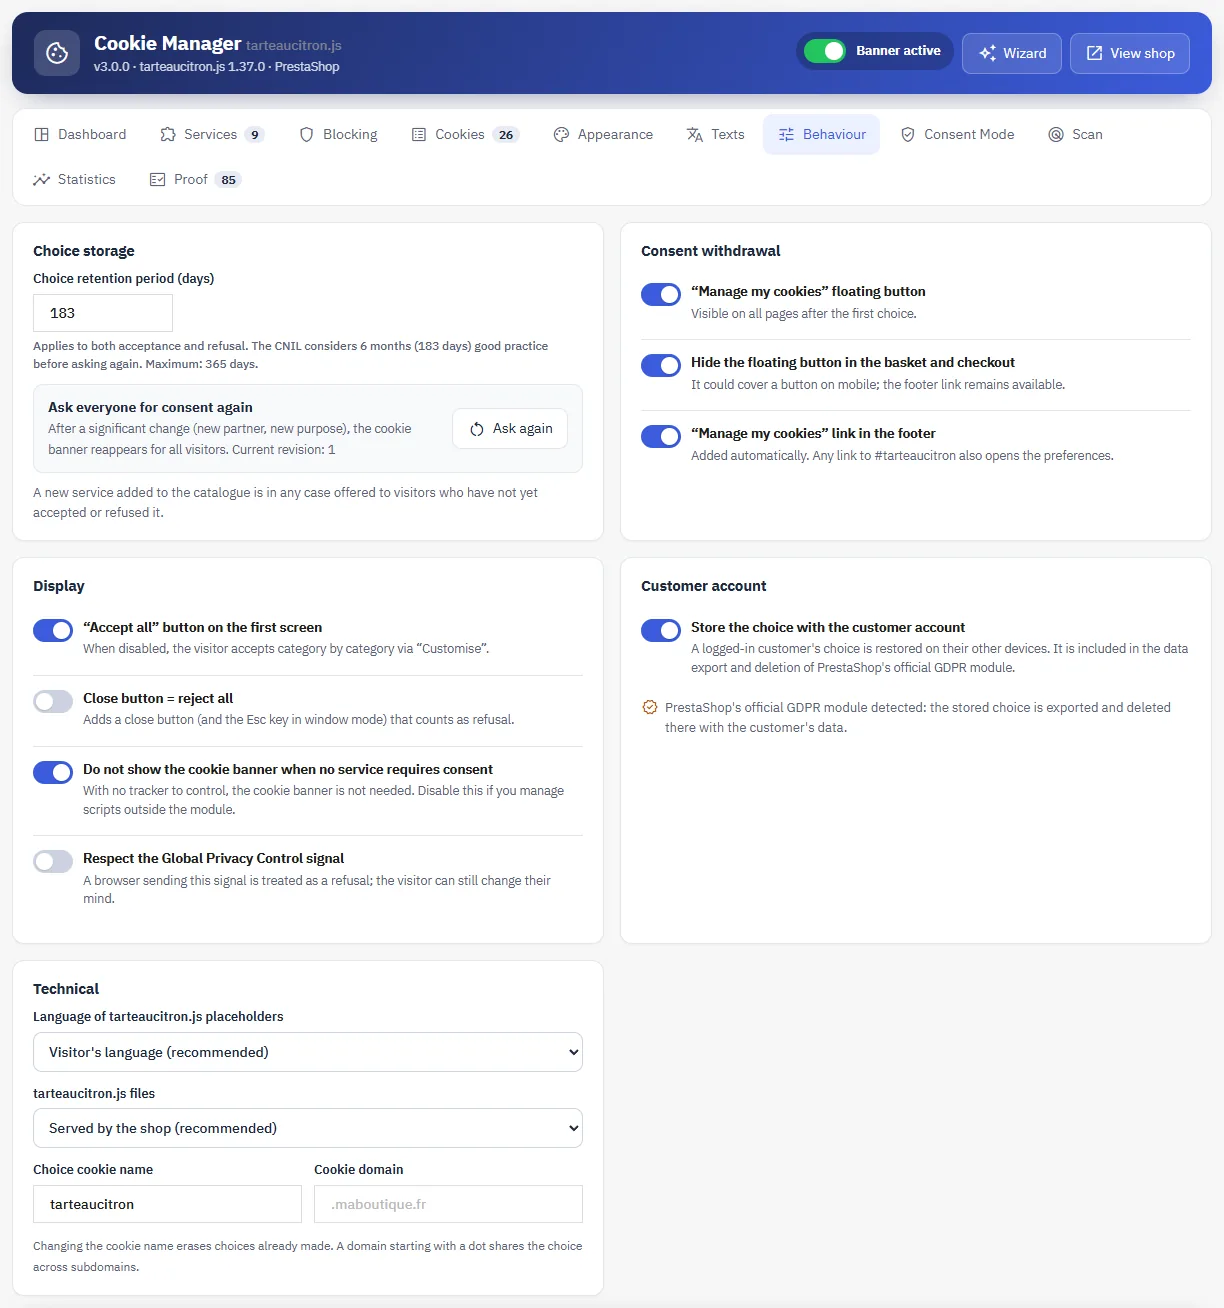
- Choice retention period: 183 days by default (6 months, a period the CNIL presents as good practice), 365 days at most. It applies to both acceptance and refusal.
- Ask everyone for consent again: after a significant change, a button makes the cookie banner reappear for all visitors. A service that has been added is in any case offered to visitors who have not yet seen it.
- Consent withdrawal: floating button, “Manage my cookies” link added automatically to the footer, any link to
#tarteaucitron, or the JavaScript calldftacOpenPreferences(). When consent is withdrawn, the service’s cookies are deleted and the page is reloaded. - Customer account: optionally, the choice of a logged-in customer is retrieved on their other devices. It is included in the data export and deletion of PrestaShop’s official GDPR module (psgdpr), if it is installed.
- Close button: optional, it counts as “Reject all”.
- Cookie banner hidden when no service requires consent: with no tracker to control, the cookie banner is not needed. Disable this option if you manage scripts outside the module.
- Global Privacy Control: optionally, a browser sending this signal is treated as a refusal.
Embedded videos and maps: recognised iframes (YouTube, Vimeo, Google Maps, Dailymotion, Spotify…) are replaced by a keyboard-accessible “Allow” placeholder. The platform is only contacted after the visitor’s consent. Allowing a single piece of content from its placeholder does not count as consent for the rest of the category.
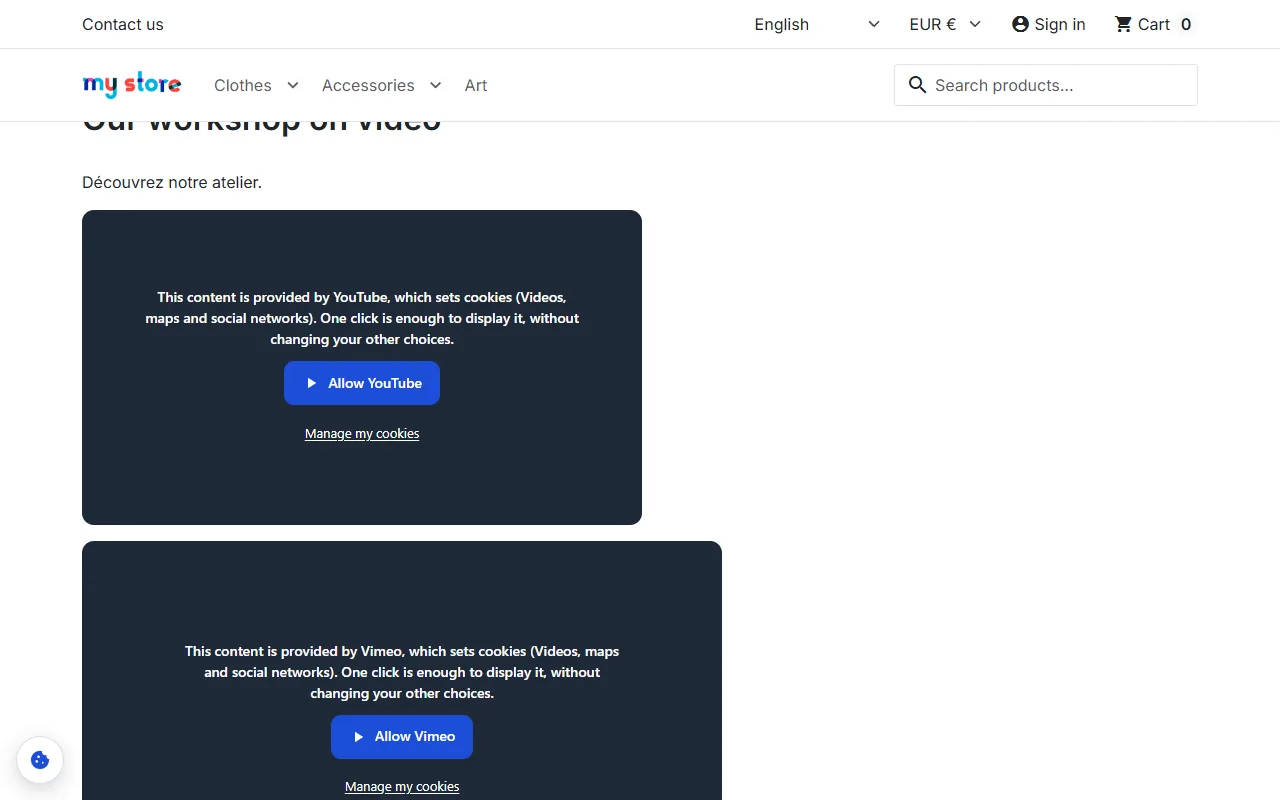
What the visitor sees
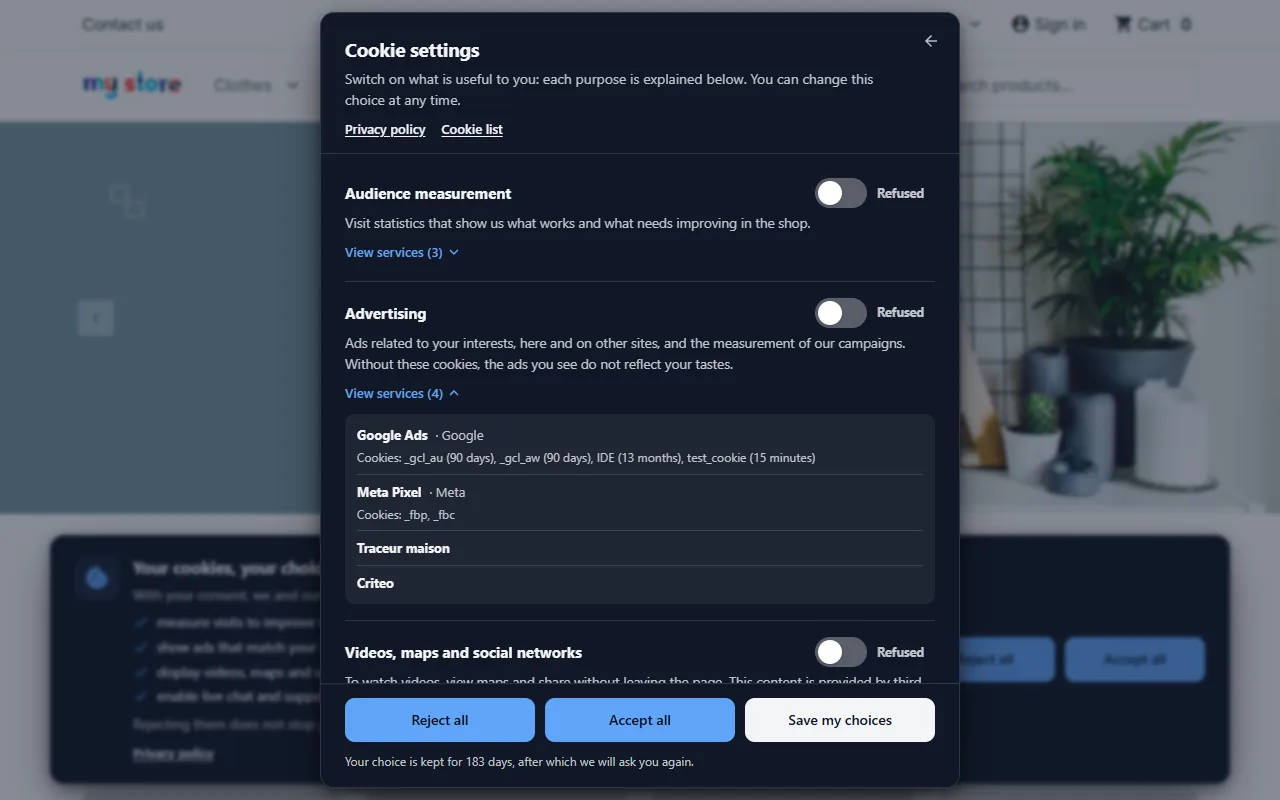
The first screen shows the title, the message, the link to the privacy policy and the “Reject all”, “Accept all” and “Customise” buttons. The preferences window lists the purposes, each with a toggle (unticked by default), the services in each category with their cookies and their duration, and the strictly necessary cookies, which are always active. It also displays the consent ID, which the visitor can give you.
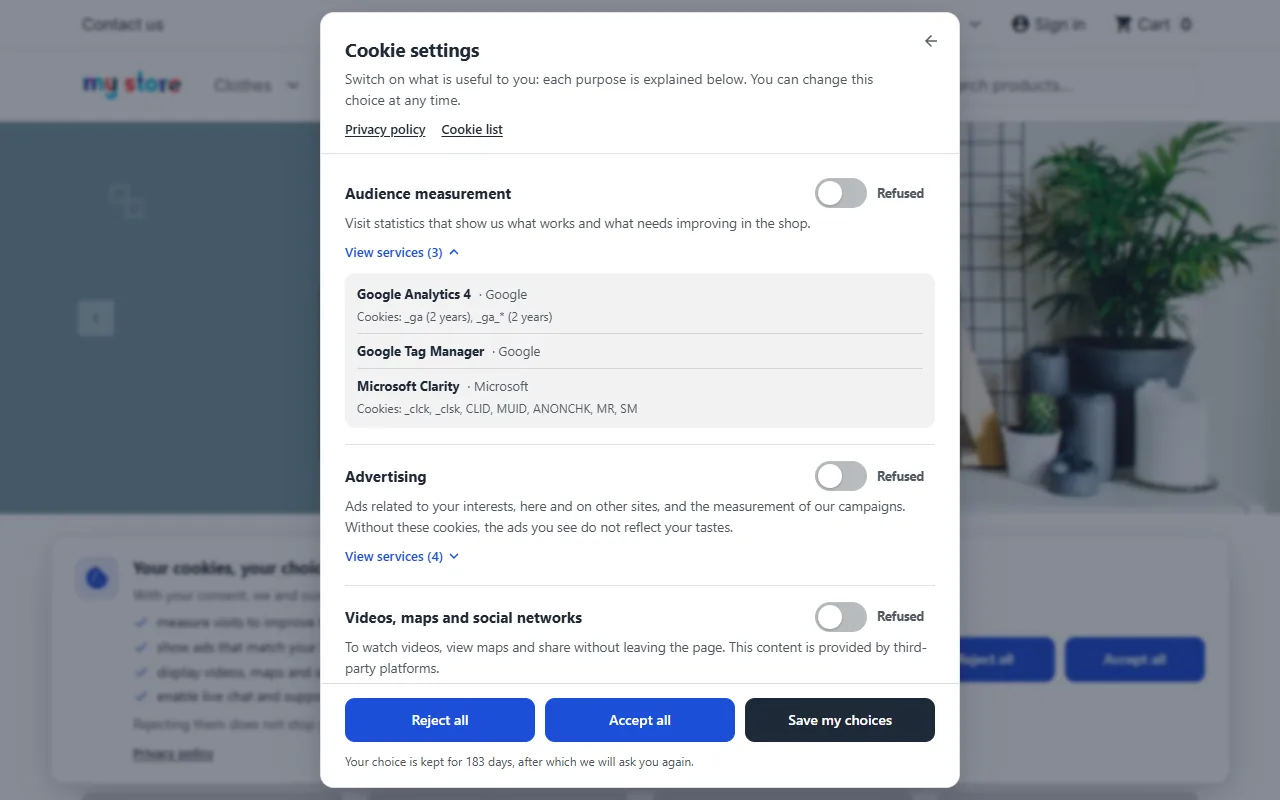
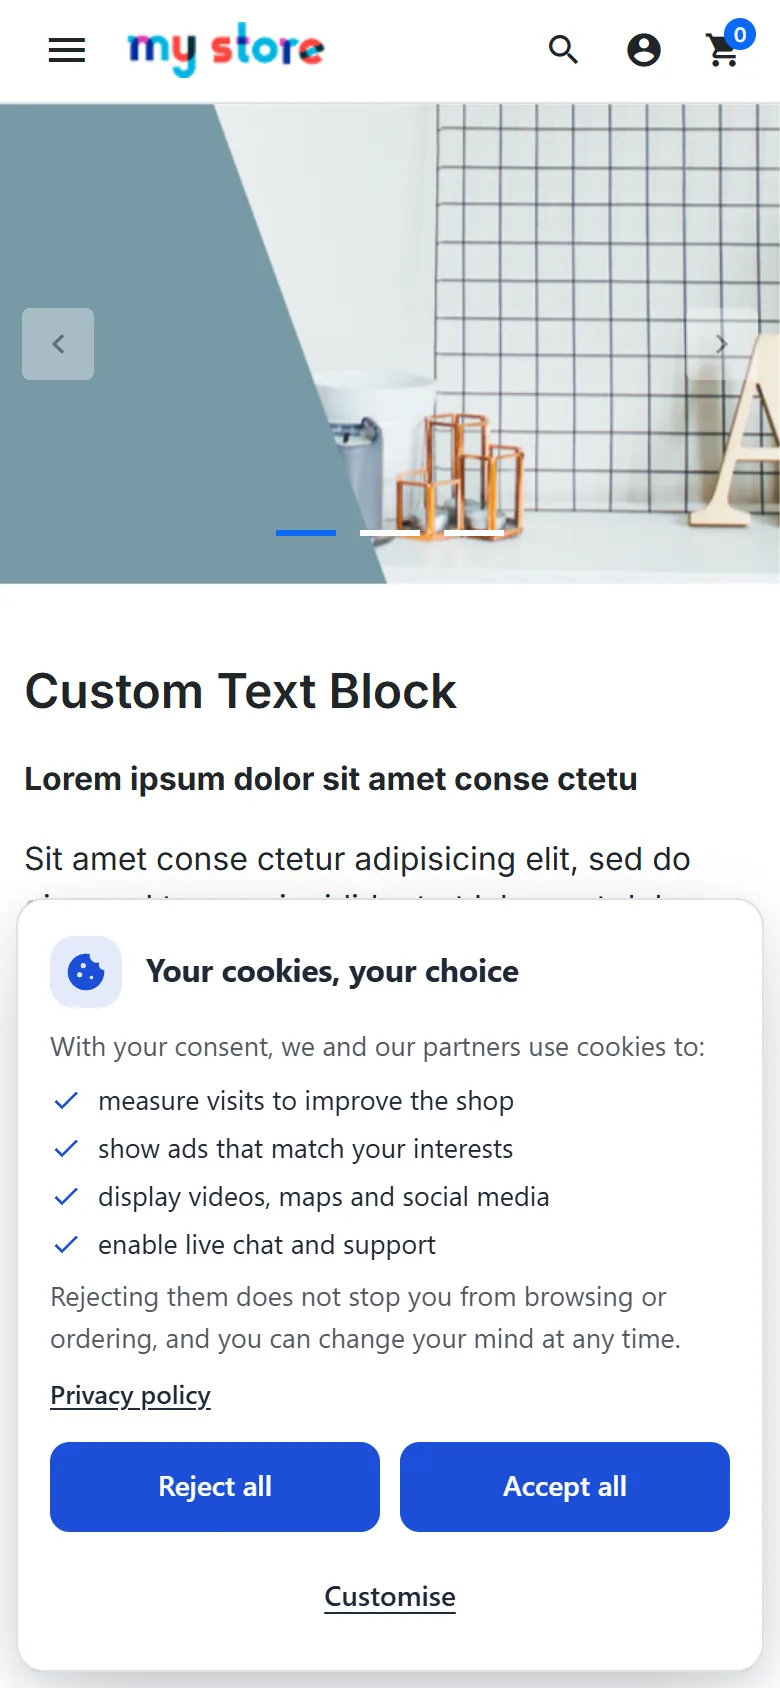
On mobile, the buttons keep the same size, each purpose fits on one line and the cookie banner does not shift the page.
Accessibility: real checkboxes announced as switches, a preferences window that keeps the focus, closing with the Esc key with focus returned, reduced motion if the visitor has requested it. No violations were found by axe-core (WCAG 2.1 A and AA) on the cookie banner, the preferences, blocked content and the cookie list, in the light and dark themes.
Google Consent Mode v2
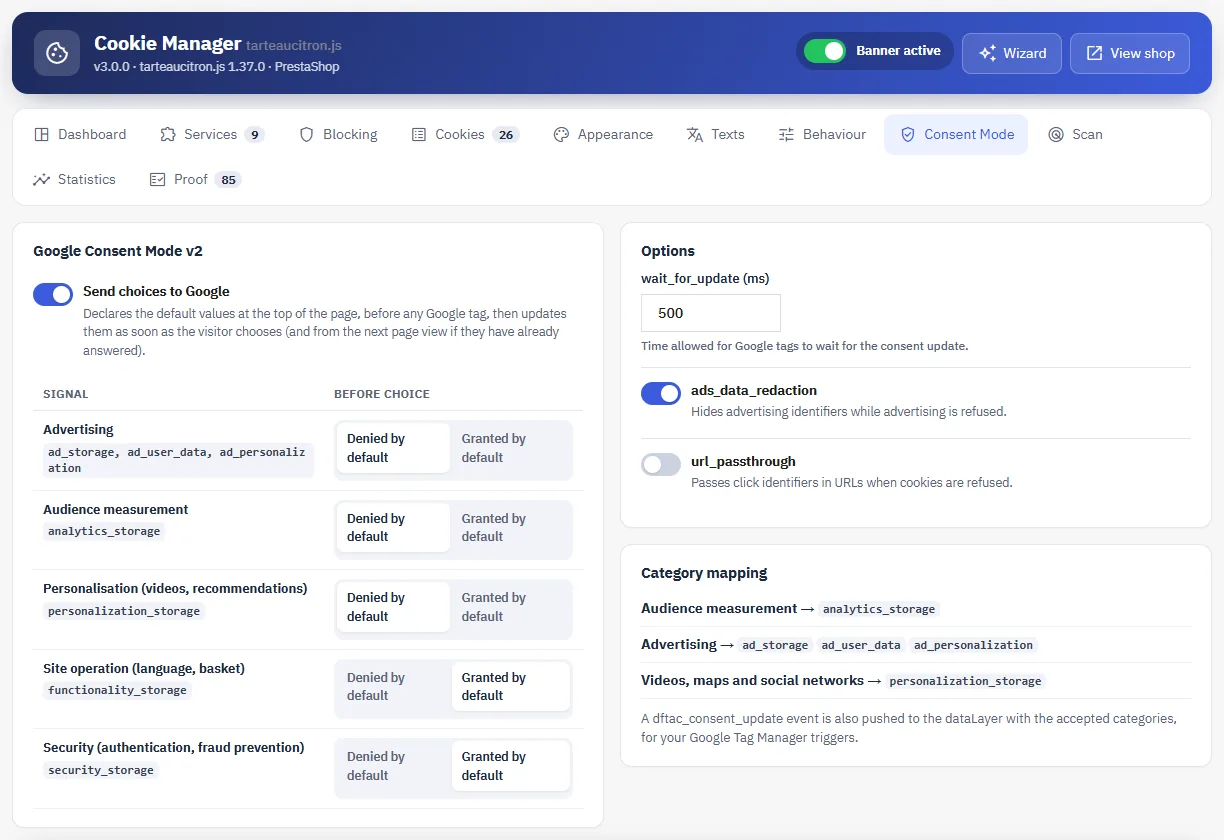
The module declares the default values at the top of the page, before any Google tag: advertising, measurement and personalisation set to denied, functionality and security set to granted (editable). As soon as the visitor chooses, the signals are updated according to the accepted categories:
- Audience measurement →
analytics_storage; - Advertising →
ad_storage,ad_user_data,ad_personalization; - Videos, maps and social networks →
personalization_storage.
For a visitor who has already answered, the update is sent at the top of the page from the next page view, without waiting for the page to finish loading. The wait_for_update, ads_data_redaction and url_passthrough options are adjustable, and a dftac_consent_update event is pushed to the dataLayer for your Google Tag Manager triggers.
Third-party script scan
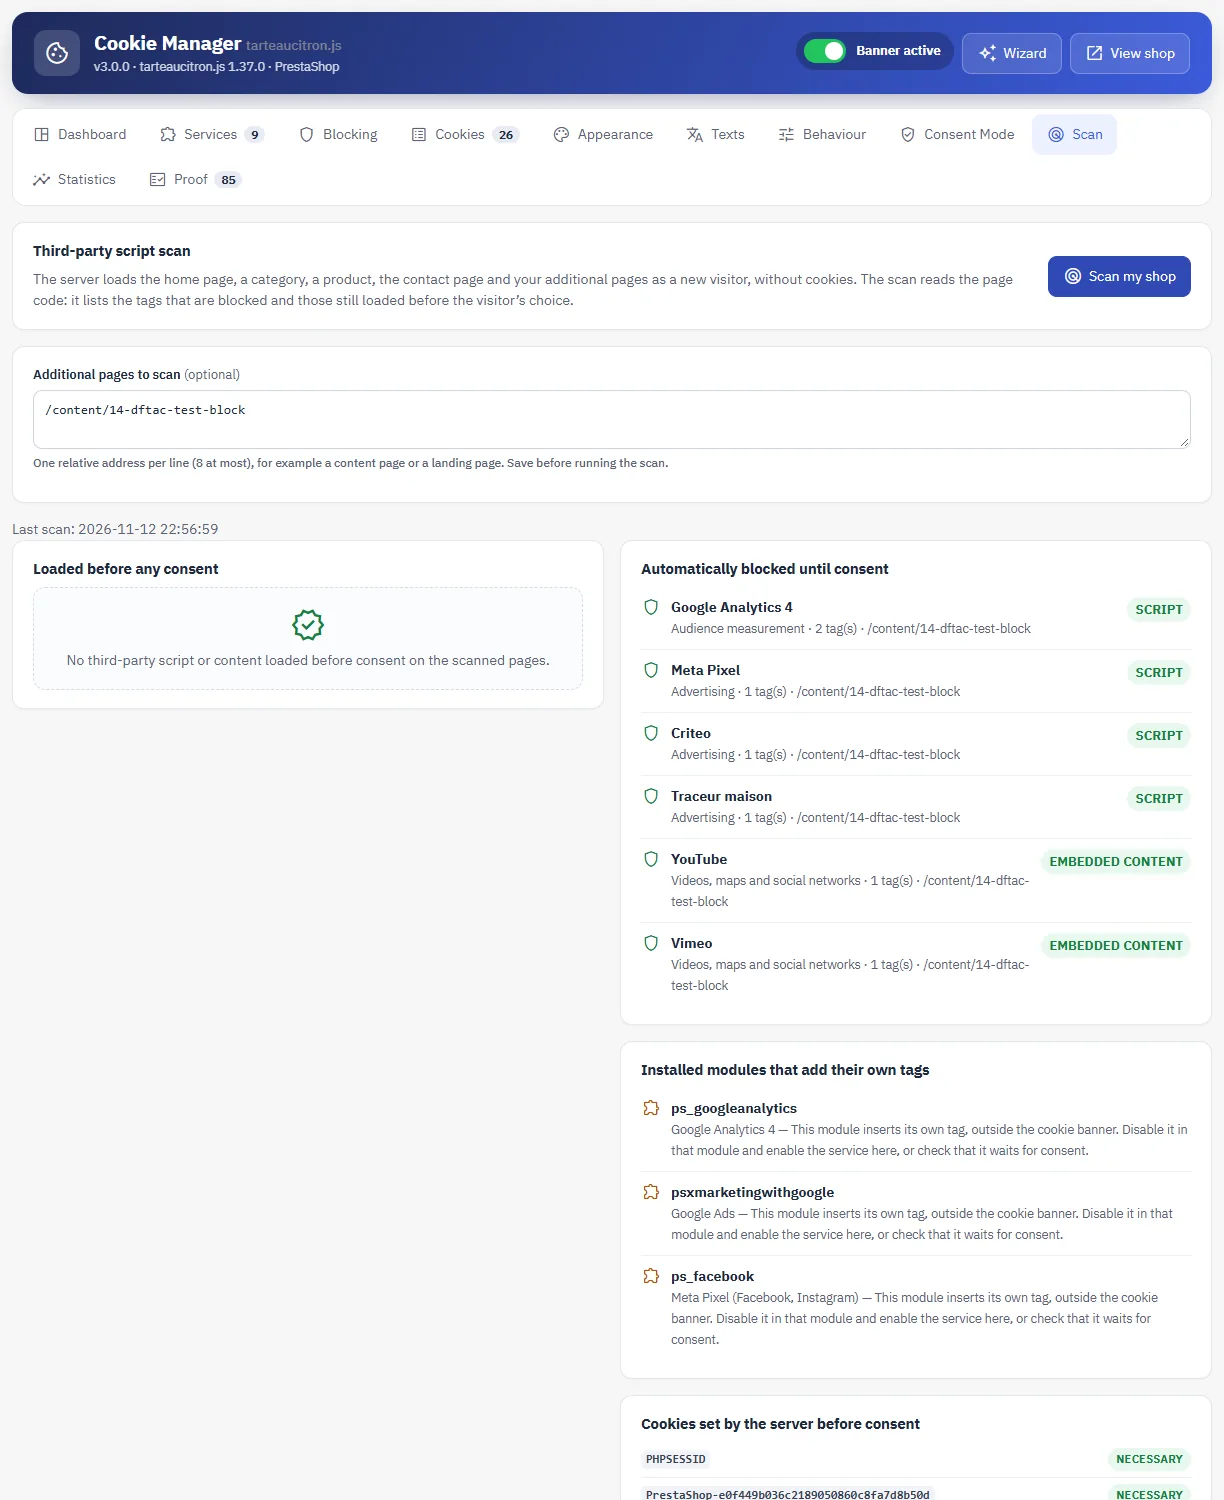
The Scan my shop button loads the home page, a category, a product, the contact page and up to 8 pages of your choice from the server, as a new visitor without cookies. The result lists the tags blocked automatically, the third-party scripts and content still loaded before the choice (with a Block button that creates the rule), the cookies set by the server and the installed modules known to add their own tags.
The scan reruns by itself when the back office is opened once it is more than 30 days old. It reads the HTML sent by the shop: a script added later by JavaScript is not detected.
Statistics and A/B testing
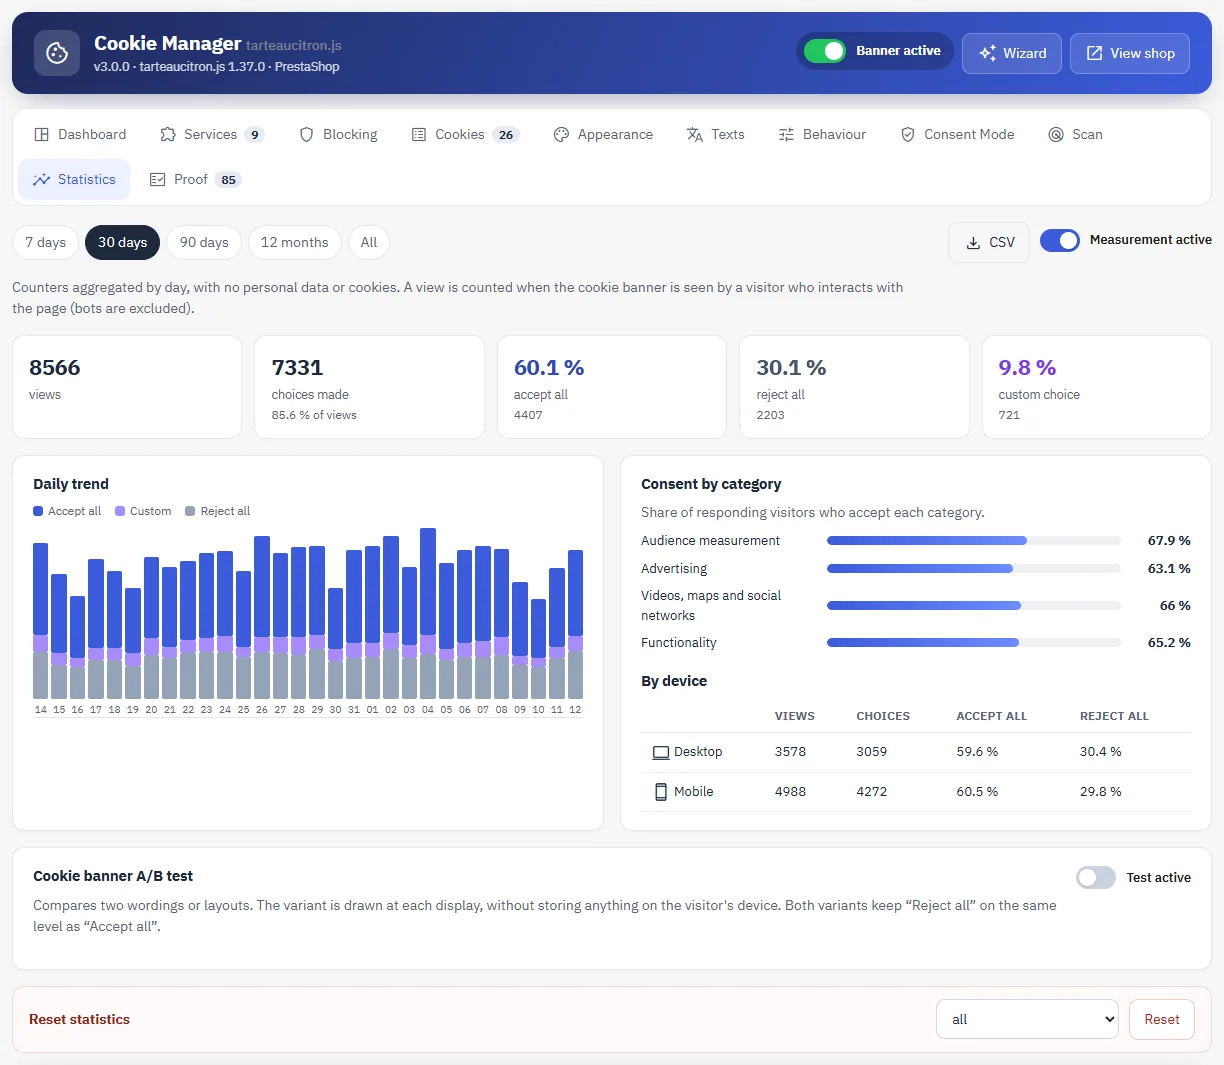
The Statistics tab shows views, choices made, the shares of “Accept all”, “Reject all” and custom choices, consent by category, the desktop/mobile split and the daily trend, over 7, 30 or 90 days, 12 months or the entire history, with CSV export. Counters are aggregated by day, with no personal data or cookies. A view is counted when the cookie banner is seen by a visitor who interacts with the page; bots are excluded.
The A/B test compares two wordings or layouts. The variant is drawn at each display, without storing anything on the visitor’s device, and both variants keep “Reject all” on the same level as “Accept all”. A winner is only announced beyond 100 choices per variant and a significant difference at 95%.
Proof of consent
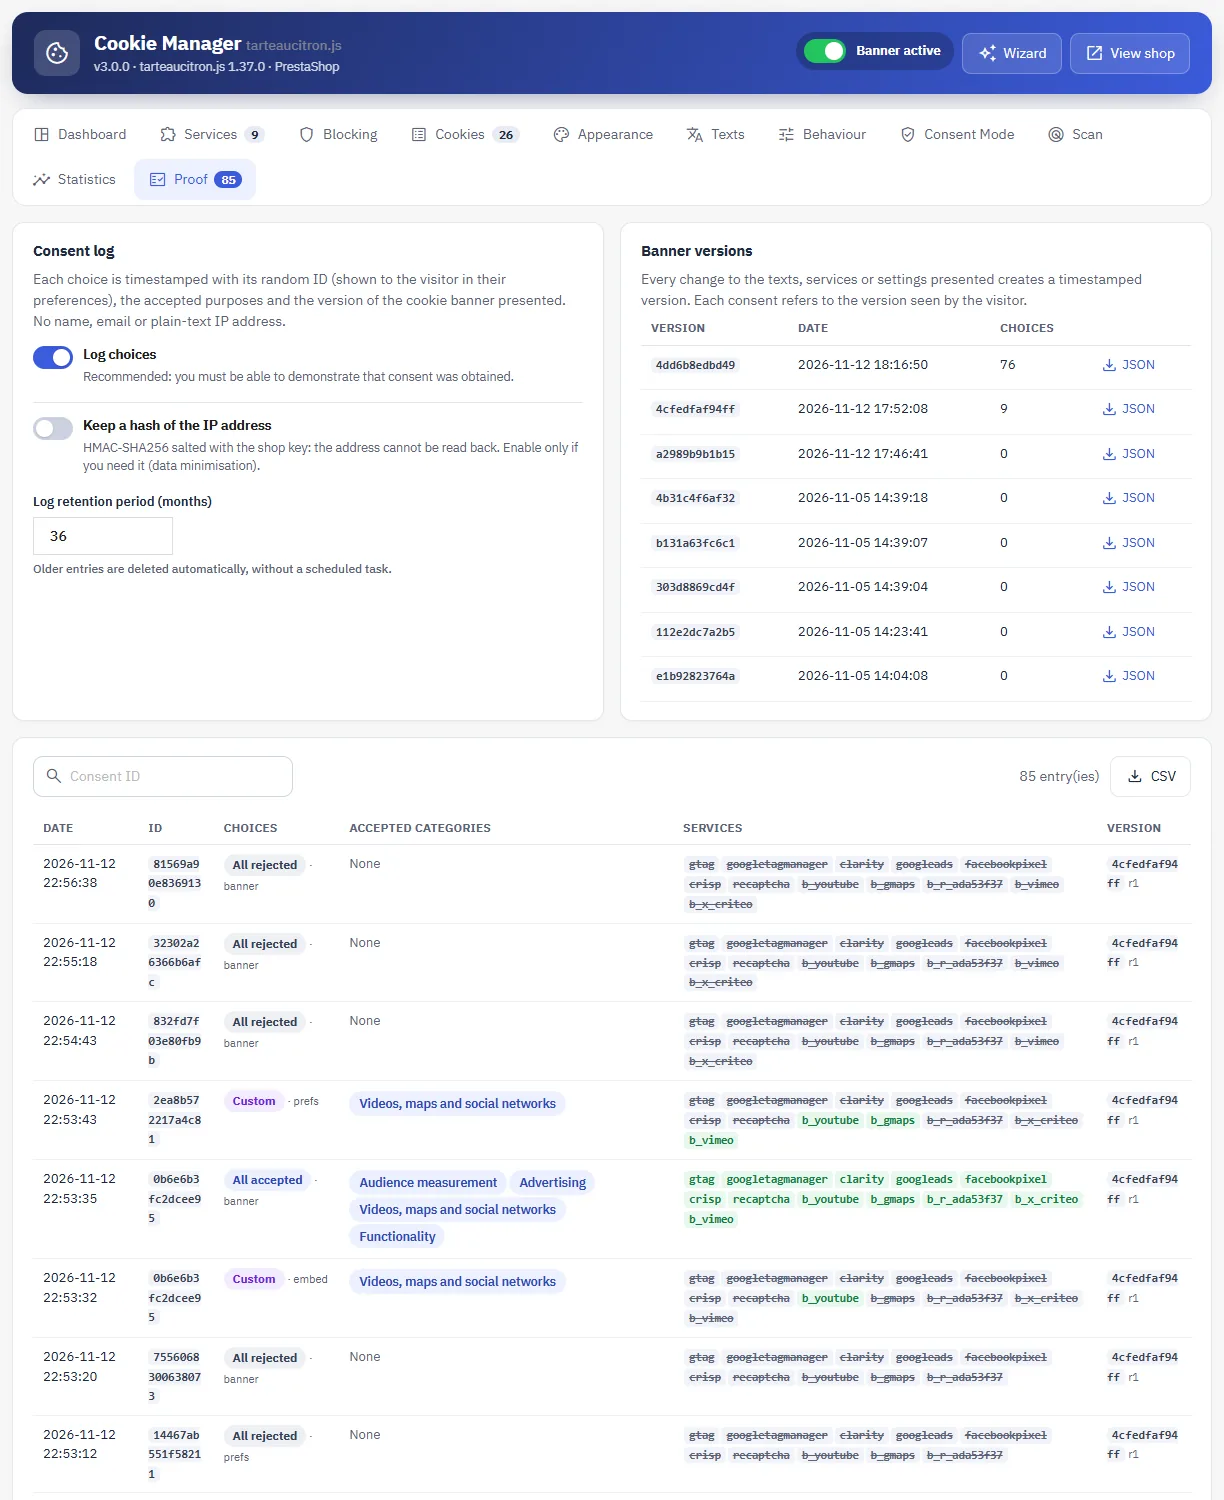
Each choice is recorded with its date, its random ID (also stored in the visitor’s cookie), the action, the accepted categories and services, the version of the cookie banner presented and the source of the choice (cookie banner, preferences, floating button, blocked content placeholder). No name, email or plain-text IP address is stored; a salted hash of the IP address is available as an option.
- Search by consent ID, CSV export.
- Every change to the texts, services or settings presented creates a timestamped version of the cookie banner, downloadable in JSON format.
- Automatic purge beyond the chosen retention period, without a scheduled task; manual purge also possible.
- The log is kept if the module is uninstalled.
Hosting and weight
Before any choice, the page loads only two files from the module, served by your shop: the cookie banner’s script and stylesheet. tarteaucitron.js, its language file and the service files are only downloaded after a consent that needs them; a visitor who refuses never downloads them. The “jsDelivr CDN” option then loads the official files from jsDelivr, a third party contacted as soon as a service is accepted.
Measured on a PrestaShop 9.1.5 home page (Hummingbird theme): 2 files and 12 KB transferred before any choice. Version 2.0.0 loaded 5 files and 38 KB (measured on PrestaShop 8.2.1, Classic theme).
Multistore
Settings follow the shop context selected in the back office: select a shop to configure it individually. The log and statistics are recorded per shop.
Limitations to be aware of
- The module is not a consent management platform registered with IAB Europe (TCF), nor a Google-certified CMP. If you display AdSense, Ad Manager or AdMob advertising in Europe, Google requires a certified CMP.
- Automatic blocking and the scan read the HTML of the pages: they do not see a script injected later by another script.
- The cookie banner is the same whatever the visitor’s country.
- These features help you apply the good practice of the CNIL and the EDPB; they do not replace a legal analysis of your site (inventory of trackers, privacy policy, contracts with your partners).
Troubleshooting
- The cookie banner does not appear: check that the cookie banner is enabled (switch at the top of the page), that at least one service requiring consent is ready, or disable the “Do not show the cookie banner when no service requires consent” option. Then clear the PrestaShop cache.
- A service does not load after acceptance: check its badge in the Services tab. “To be completed” indicates a missing or invalid ID.
- A script loads before the choice: run the scan, then use the “Block” button. If the script does not appear, it is most likely injected by another script: disable it in the module that adds it.
- A tool no longer works after blocking is enabled: add its URL to the exceptions in the Blocking tab, or declare it as a service so that it is loaded after consent.
- The cookie banner reappears on every page: check the cookie domain and that the cookie name has not been changed in the meantime.
- No entries in the log: check that logging is enabled in the Proof tab, then make a choice in a private browsing window.
Need help? Contact DataFireFly support from your customer account; we reply within 24 working hours.