
2FA Google Authenticator for PrestaShop — Documentation
Install and configure 2FA for the PrestaShop 8 and 9 back office and customer accounts: authenticator app, security keys, recovery codes, policy per profile.
This guide covers the installation, configuration and use of the DataFirefly 2FA module for PrestaShop 8 and 9. After the password, the module asks for a second proof of identity: a 6-digit code from an authenticator app (TOTP, RFC 6238), a security key or a passkey (WebAuthn), or a recovery code. It protects the back office and, optionally, customer accounts.
What is new in version 2.0.0: fully rebuilt access control (every back-office page, including PrestaShop 8 legacy pages, AJAX calls and the file manager), security keys and passkeys, protection against code replay, trusted devices, policy per profile, dashboard, security log, e-mail alerts, customer 2FA by app or by e-mail, and a command-line recovery command. Apps already enrolled keep working after the update.
Requirements
- PrestaShop 8.0 to 8.2 or PrestaShop 9.x (Classic and Hummingbird themes for the customer side)
- PHP 7.2.5 minimum on PrestaShop 8 (PHP 8.1 minimum on PrestaShop 9); tested up to PHP 8.5
- OpenSSL PHP extension (security keys and passkeys)
- An authenticator app on the phone: Google Authenticator, Microsoft Authenticator, 2FAS, Aegis, 1Password, Bitwarden or any TOTP-compatible app
- HTTPS for security keys and passkeys (a browser requirement)
- A synchronised server clock (NTP)
Installation and update
- In the back office, open Modules → Module Manager, click Upload a module and select
df2fa-2.0.0.zip. - The module creates its tables, registers its pages and installs two small overrides (
Employee::isLoggedBackandProfile::getProfileAccess) that extend the protection to the file manager. - Open Configure to set the policy (see below).
Installing the module does not force 2FA on anyone: you cannot lock yourself out of the back office by installing it. The requirement is then set profile by profile.
Updating from 1.x
- Secrets already enrolled are kept: your employees keep their app. They simply enter their code once after the update.
- Secrets still stored in plain text (versions 1.0.x) are encrypted automatically.
- Old recovery codes remain valid; the My 2FA page offers to create new, better protected ones.
- The old “2FA required” setting is converted into a requirement for all profiles.
If another extension already overrides Employee::isLoggedBack or Profile::getProfileAccess, the module still installs, without its overrides; the Overview then shows that the file manager is not covered.
Signing in to the back office with 2FA
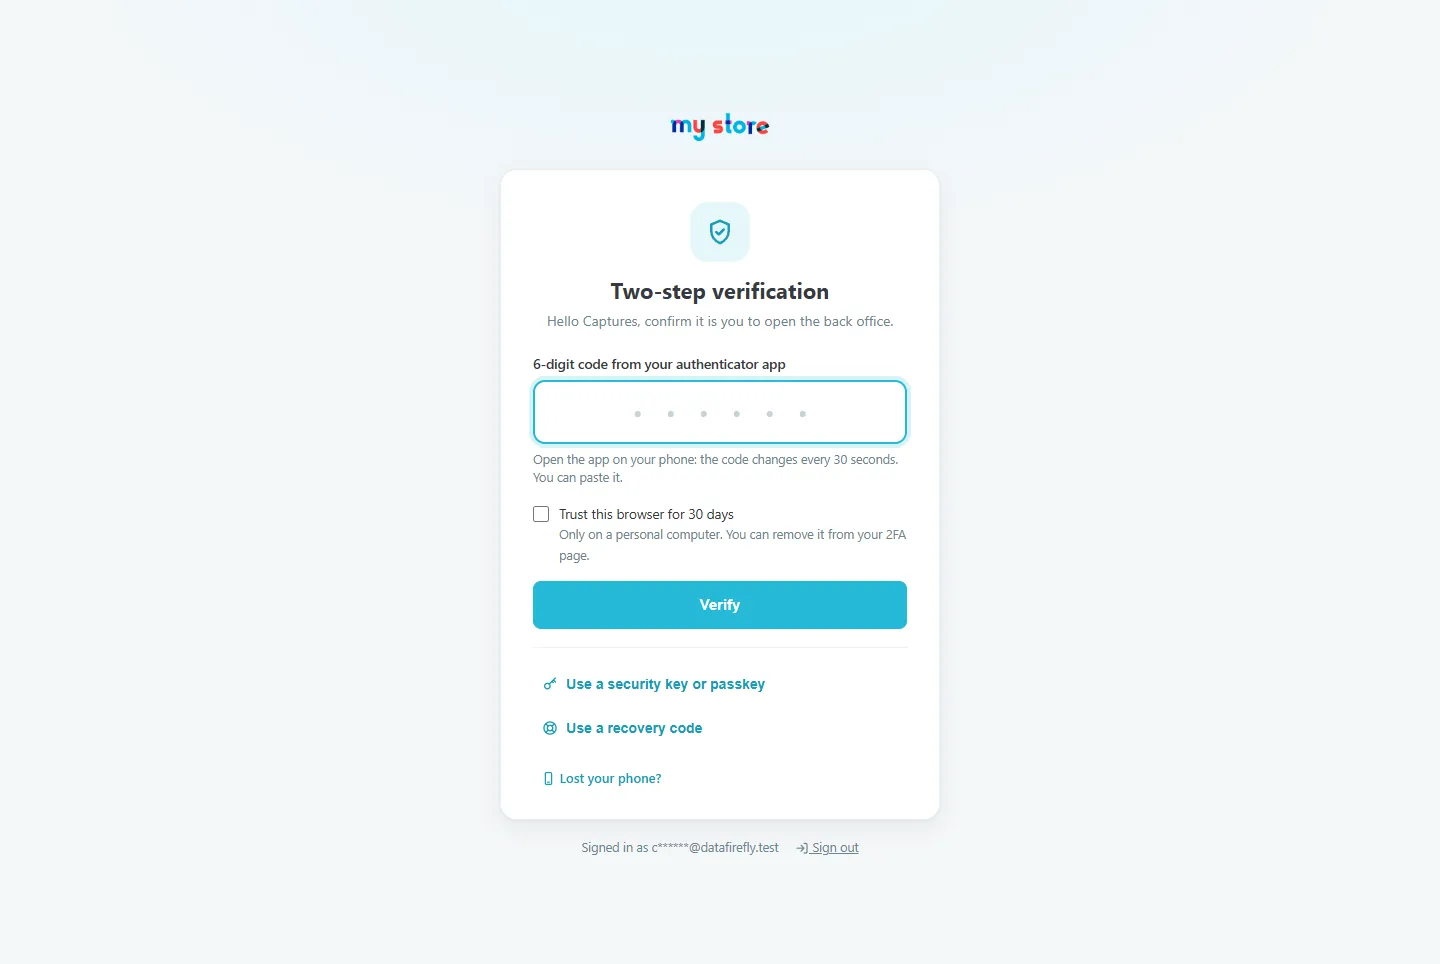
After the password, the employee lands on a full-screen page, without the back-office menu. They enter the 6-digit code from their app: pasting is accepted and verification starts automatically at the sixth digit. Once the code is accepted, they return to exactly the page they had requested.
- Trust this browser for 30 days: on a personal computer, this box avoids asking for a code again for the chosen duration (30 days by default). The device can be revoked at any time from the My 2FA page.
- Other ways to verify: security key or passkey, or recovery code.
- Phone clock out of sync: if the code matches a shifted time, the page says so and explains how to correct the phone’s time (access is still denied).
- Replay refused: a code that has already been used cannot be used a second time.
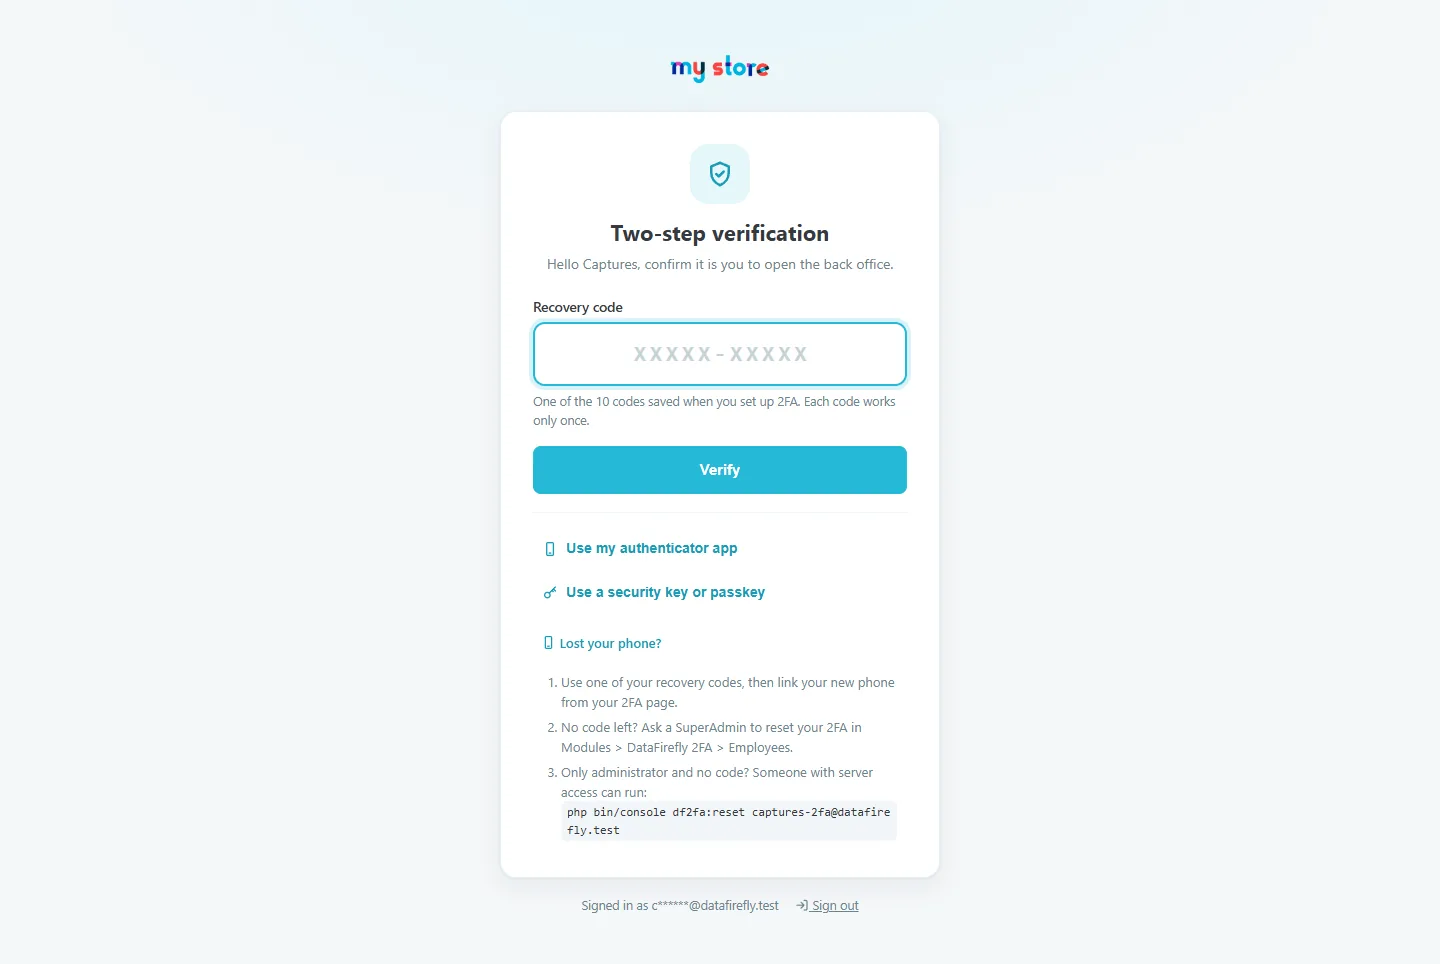
Lost phone: recovery codes and help
The Use a recovery code link accepts one of the 10 codes in the XXXXX-XXXXX format provided at activation (lowercase and spaces accepted). Each code works only once; when 3 codes or fewer are left, the back office prompts you to create new ones. The Lost your phone? help lists the options:
- Use a recovery code, then link the new phone from the My 2FA page.
- Ask a SuperAdmin to reset the 2FA in Modules > DataFirefly 2FA > Employees.
- Only administrator and no code: on the server command line,
php bin/console df2fa:reset email@exemple.com(or--unlockto lift a lockout only,--listto list the accounts).
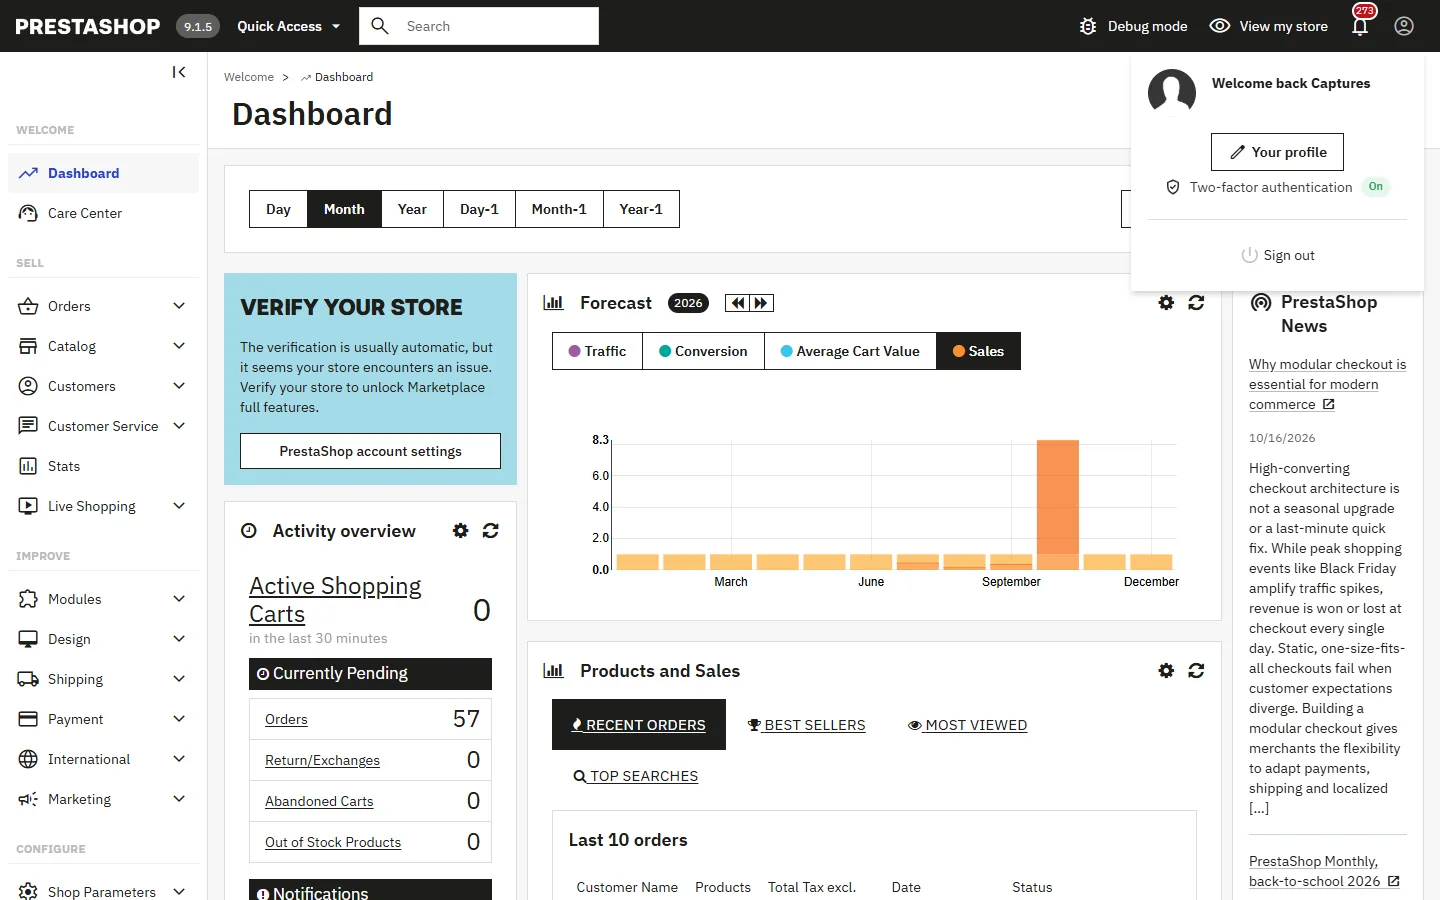
Turning on 2FA (employee)
Each employee finds the Two-factor authentication entry in their menu (top right), with an On or Off badge. If their profile requires 2FA, the wizard opens automatically at the next sign-in, in full screen, and no other page can be reached until it is completed.
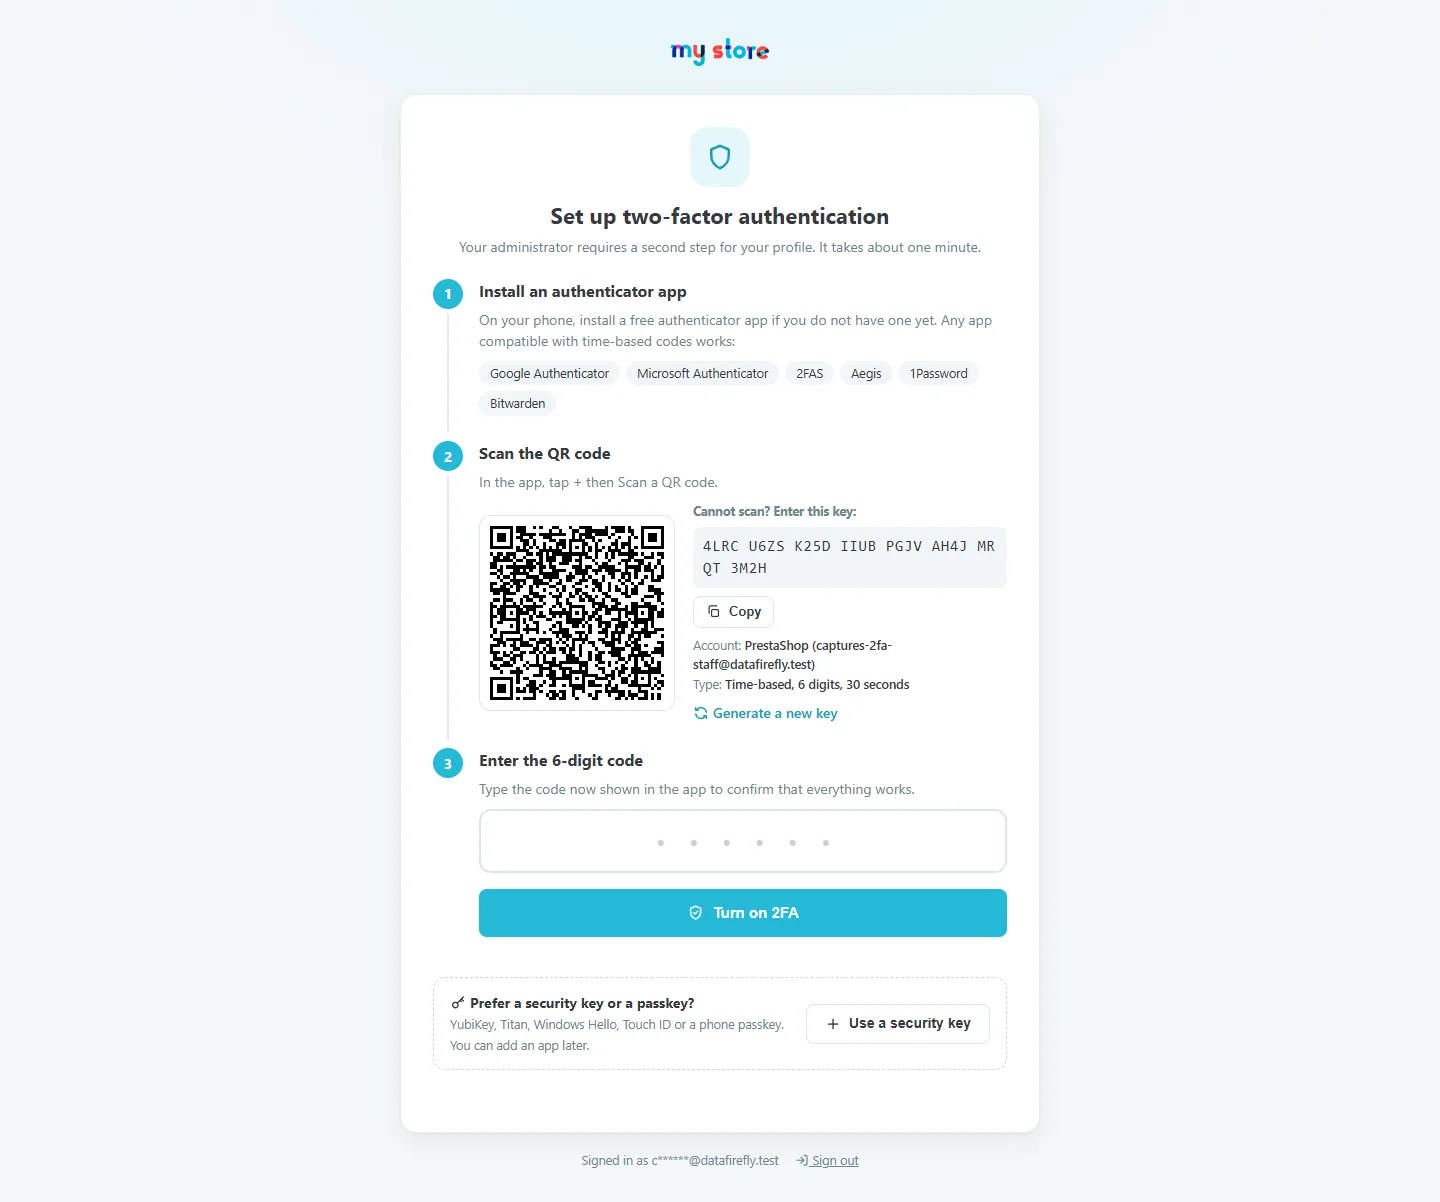
The wizard has three steps:
- Install an authenticator app on the phone.
- Scan the QR code, generated locally in the browser. Otherwise, the key is shown in groups of 4 characters with a Copy button.
- Enter the 6-digit code to confirm.
The employee can also choose a security key or a passkey instead of the app.
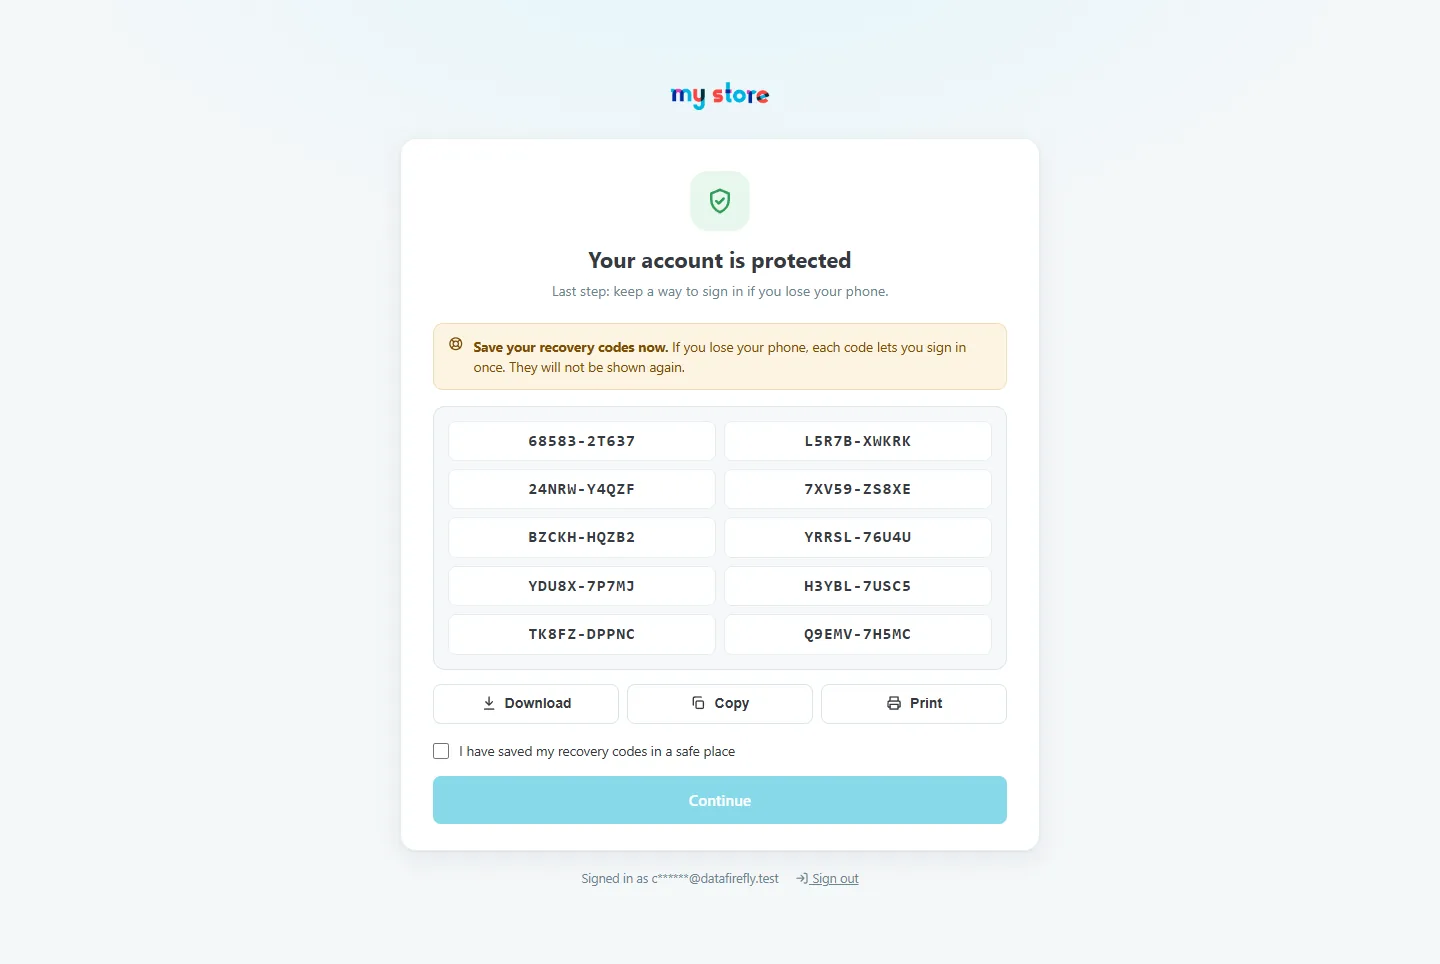
The 10 recovery codes are then shown only once, with Download, Copy and Print buttons. The employee must tick “I have saved my recovery codes in a safe place” to continue.
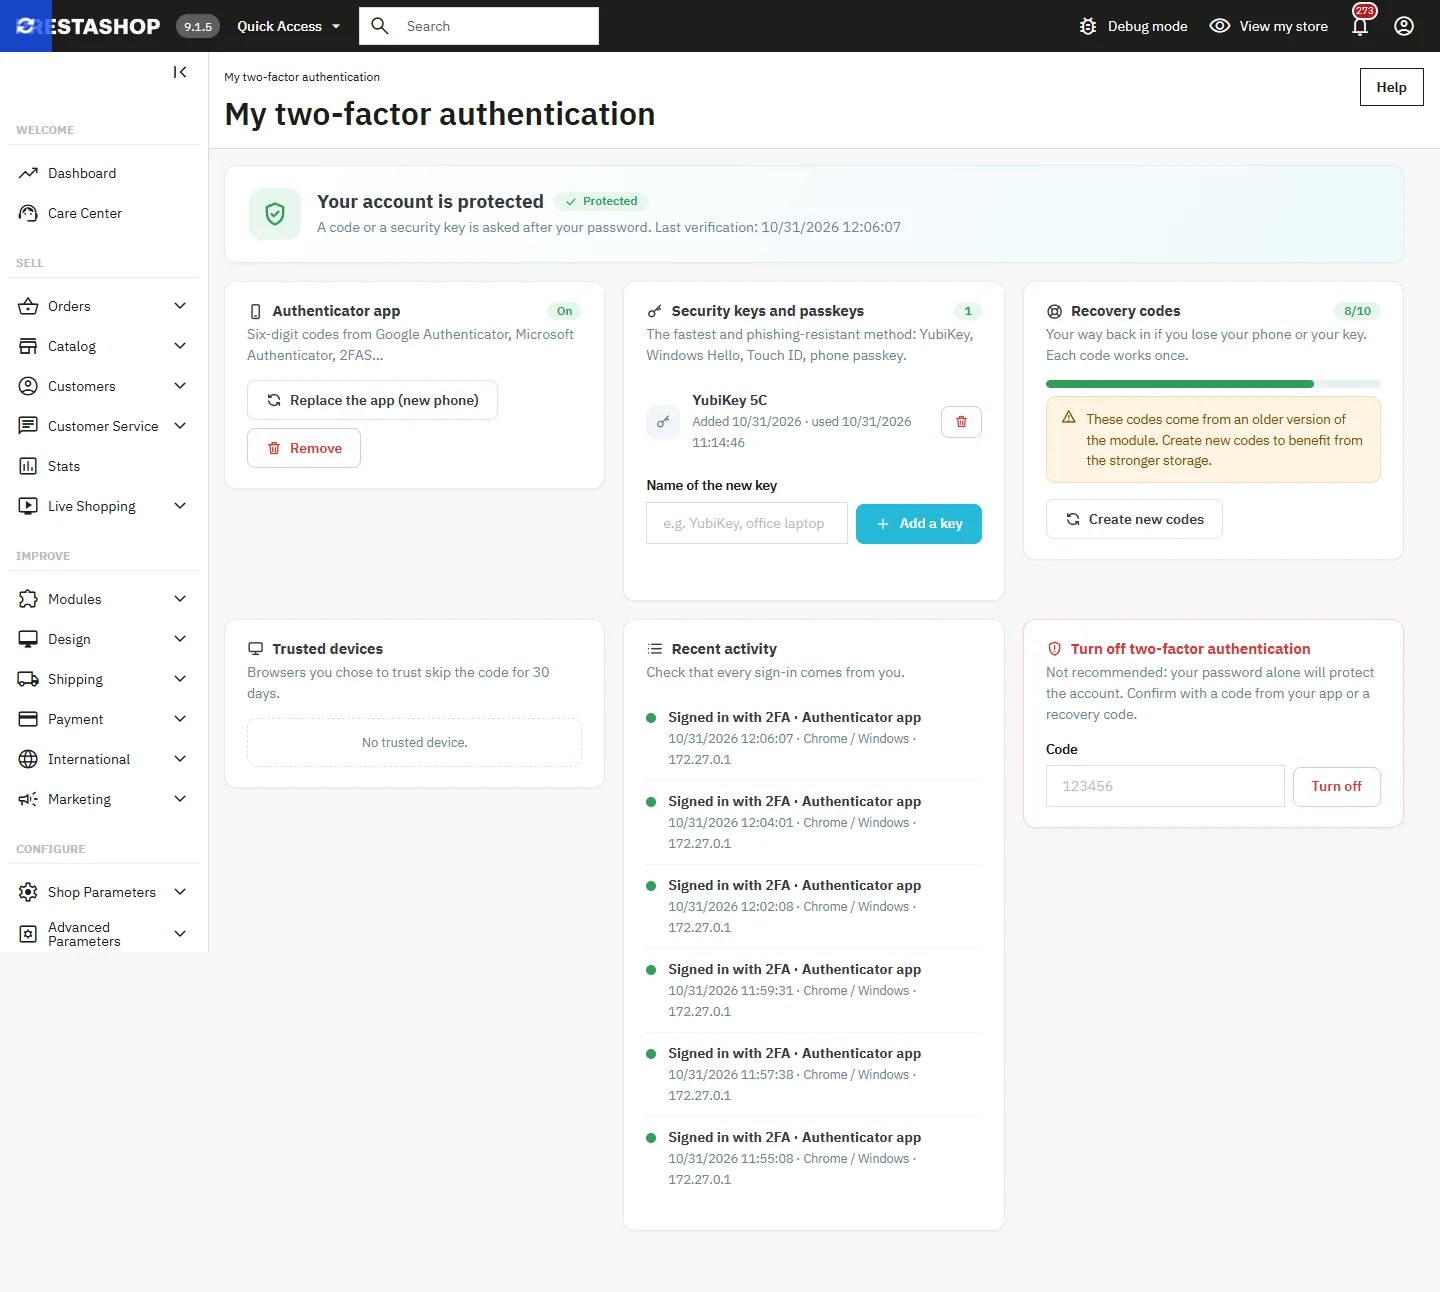
The My 2FA page
It brings together everything about the employee’s account:
- Authenticator app: replace the app (new phone); the current one keeps working until the new one is confirmed.
- Security keys and passkeys: add (with a name), list, remove.
- Recovery codes: number left, creation of a new set.
- Trusted devices: browser, last use, expiry, removal one by one or all at once.
- Recent activity: sign-ins, wrong codes, changes.
- Turn off 2FA: with a code from the app or a recovery code; not possible if the profile requires it.
Security keys and passkeys
The module accepts FIDO2/WebAuthn keys (YubiKey, Titan…) and built-in authenticators (Windows Hello, Touch ID, phone passkey) as a second factor. It is the fastest method and it resists phishing: the key only answers the genuine site. The module checks the challenge, the origin, the domain and the signature counter; a cloned key is refused. Security keys require HTTPS (or localhost).
Module dashboard
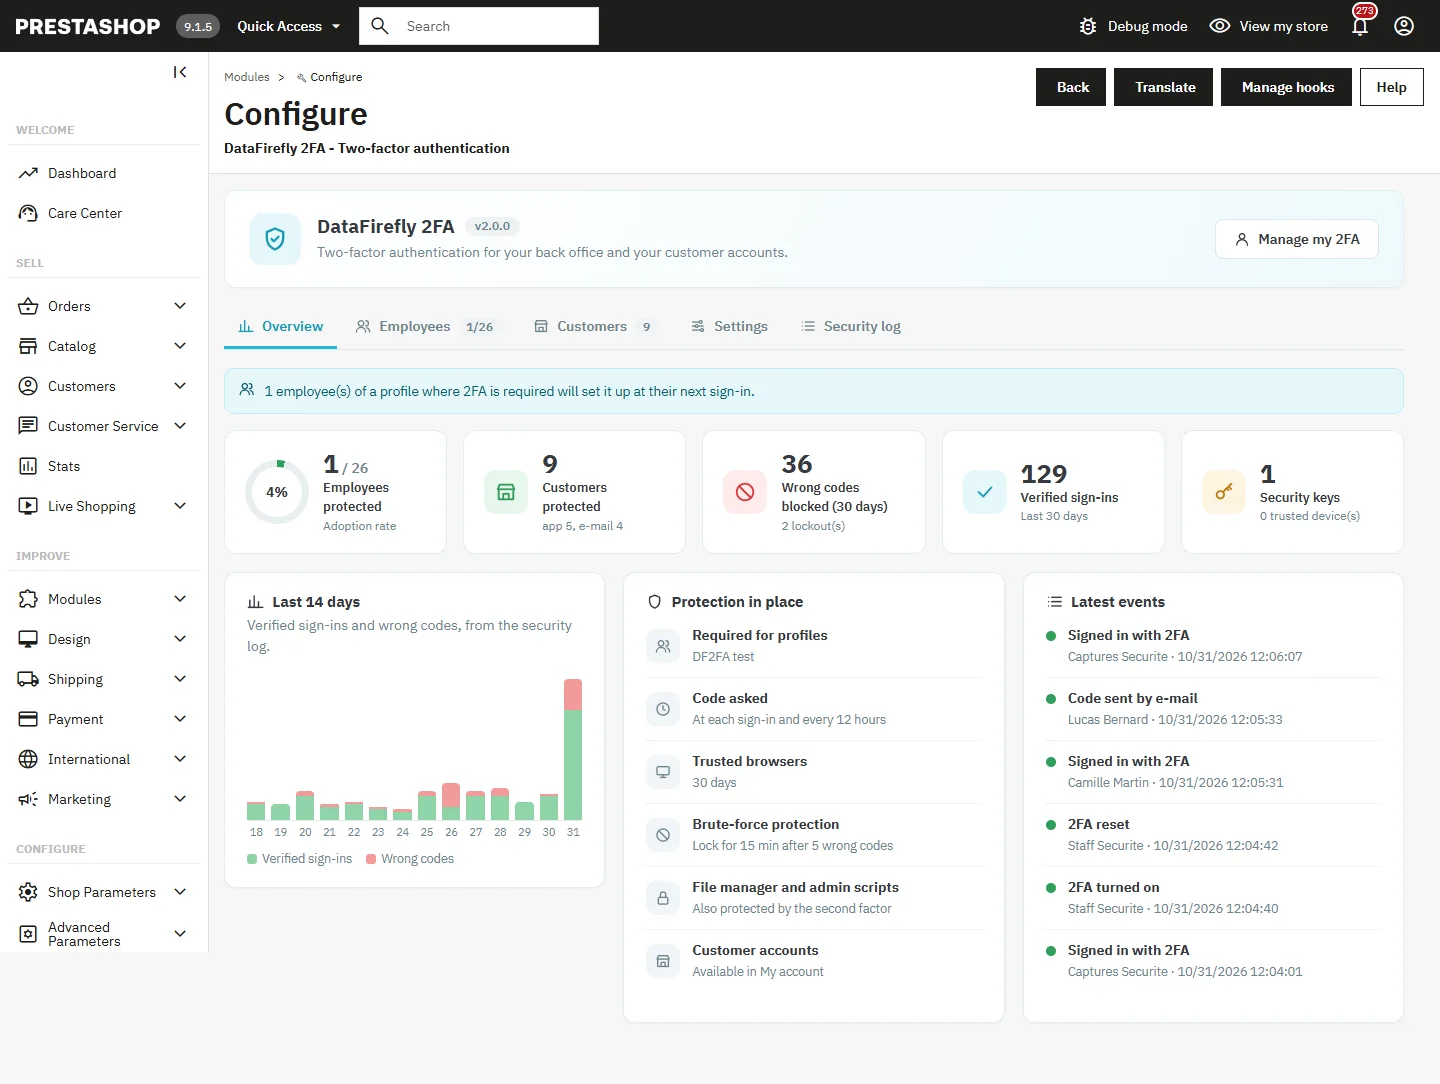
Open Modules > DataFirefly 2FA > Configure. The page has five tabs: Overview, Employees, Customers, Settings and Security log. The Overview shows the adoption rate, employees and customers protected, wrong codes blocked and lockouts over 30 days, verified sign-ins, a 14-day chart, the protection in place and the latest events. All figures are calculated from your database.
Employees and reset
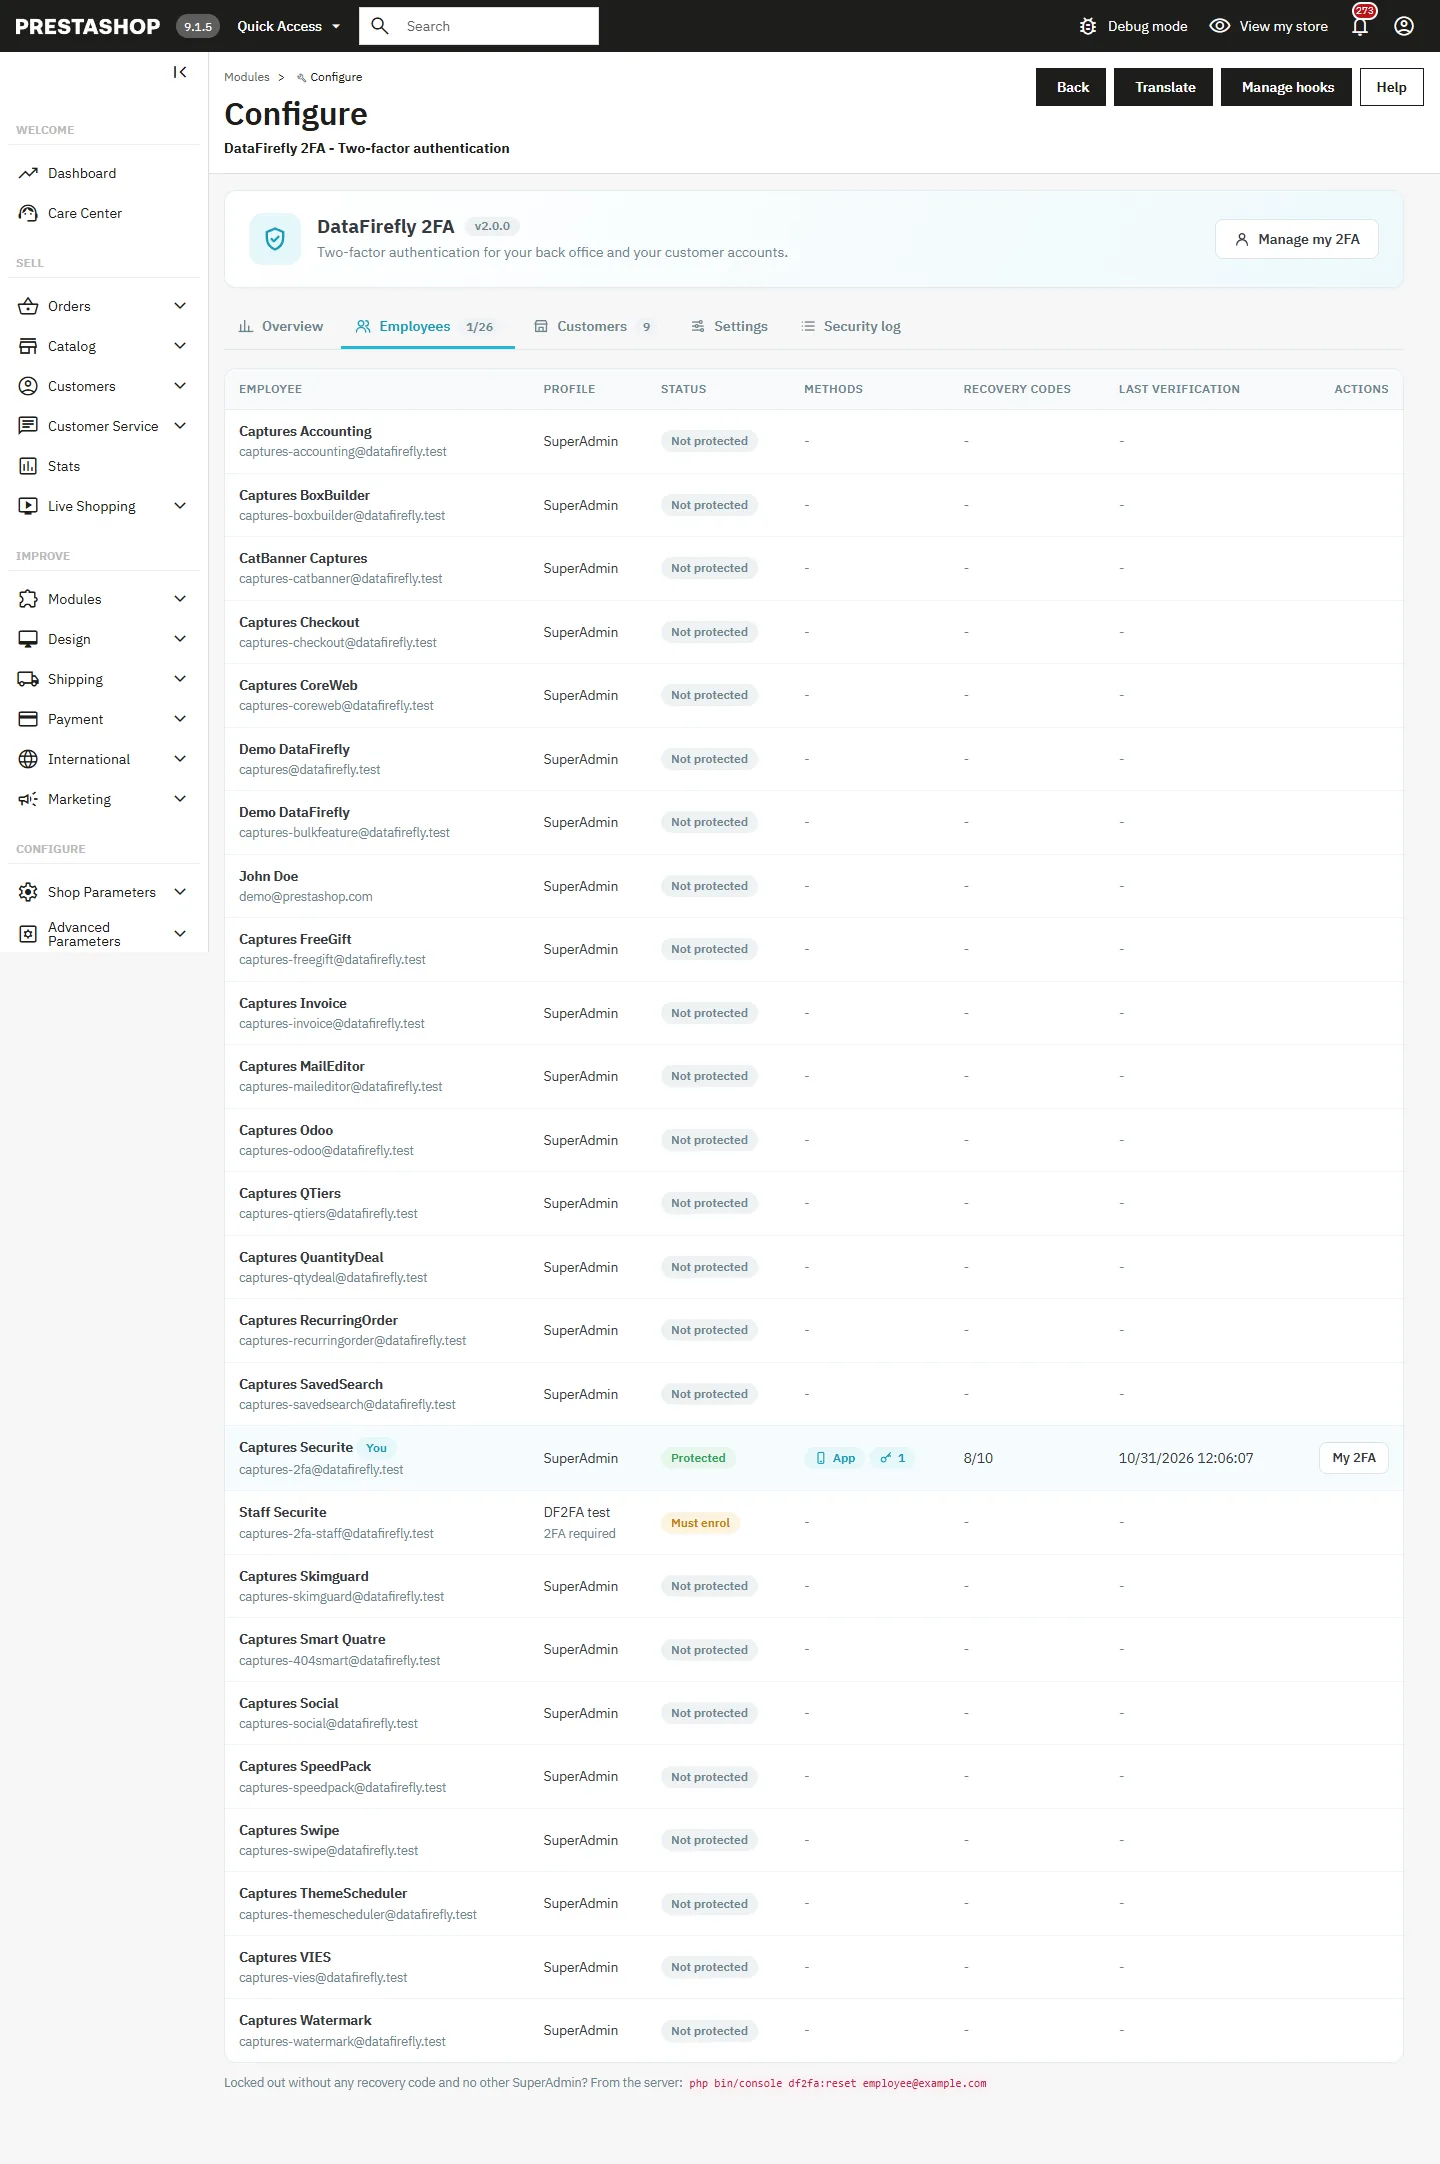
The Employees tab lists every active employee with their profile, status (Protected, Must enrol, Not protected, Locked), methods, recovery codes left and last verification. A SuperAdmin can unlock an account, revoke its trusted devices or reset its 2FA (lost phone). Every action is logged.
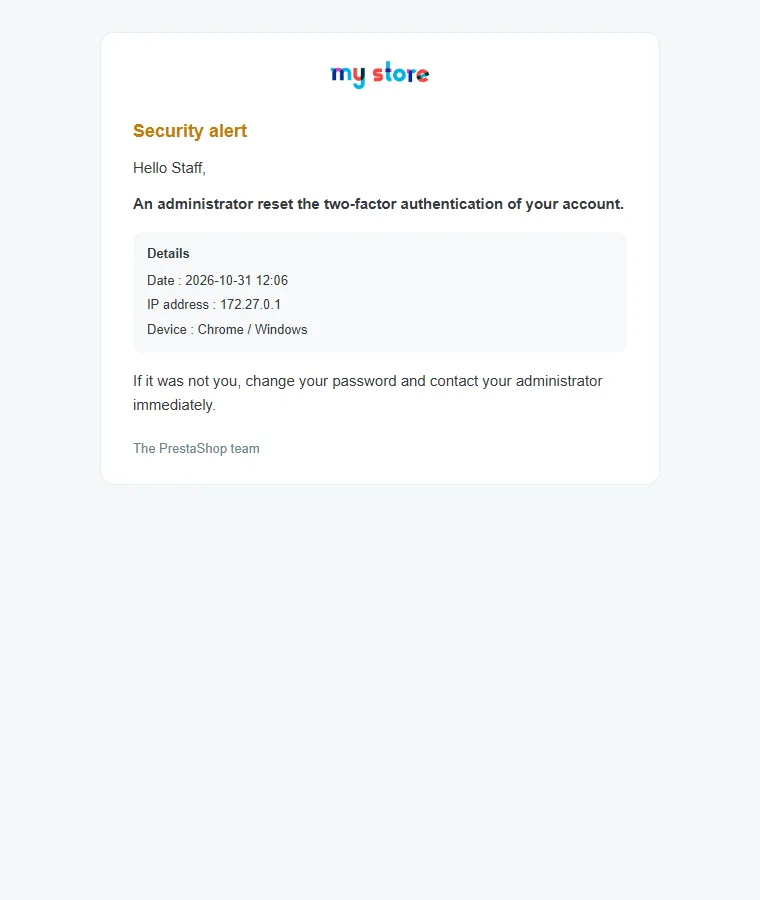
When their 2FA is reset or turned off, a recovery code is used, their account is locked or a key is added, the employee receives a security alert by e-mail, in their language.
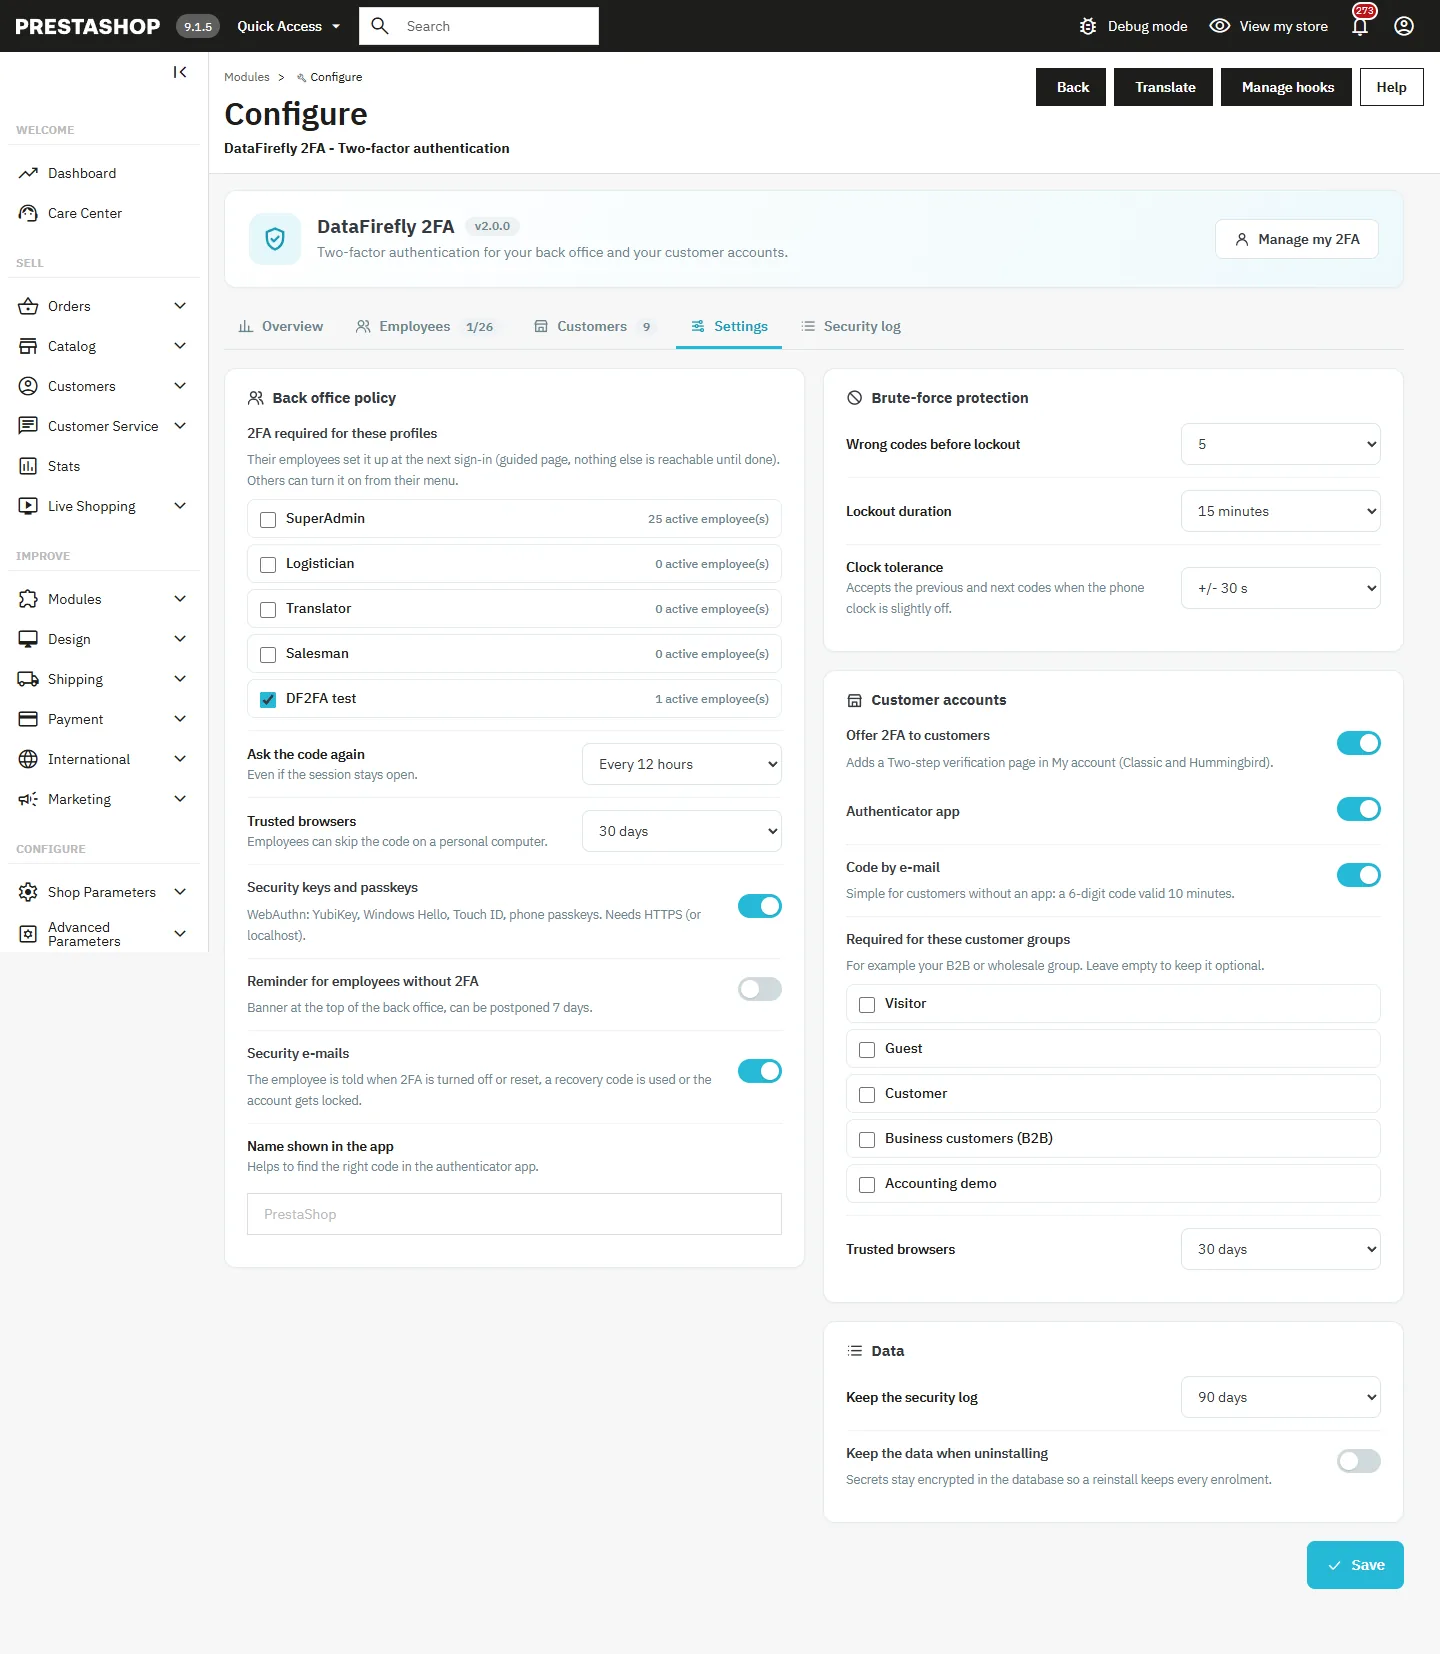
Settings
- 2FA required for these profiles: employees of the ticked profiles set up 2FA at their next sign-in. Others can turn it on from their menu.
- Ask the code again: only at sign-in, or also every 4 to 168 hours (12 hours by default).
- Trusted browsers: from 7 to 90 days, or off.
- Security keys and passkeys: on by default.
- Reminder for employees without 2FA: banner at the top of the back office, which the employee can postpone for 7 days.
- Security e-mails, Name shown in the app.
- Brute-force protection: number of wrong codes before lockout (5 by default), lockout duration (15 minutes by default), clock tolerance (±30 s by default).
- Customer accounts: see the next section.
- Data: security log retention period (90 days by default), keeping the data when uninstalling.
Recommended rollout: first turn on your own 2FA, then tick the SuperAdmin profile, then the other profiles. The Overview tab shows how many employees will set up 2FA at their next sign-in.
Customer 2FA
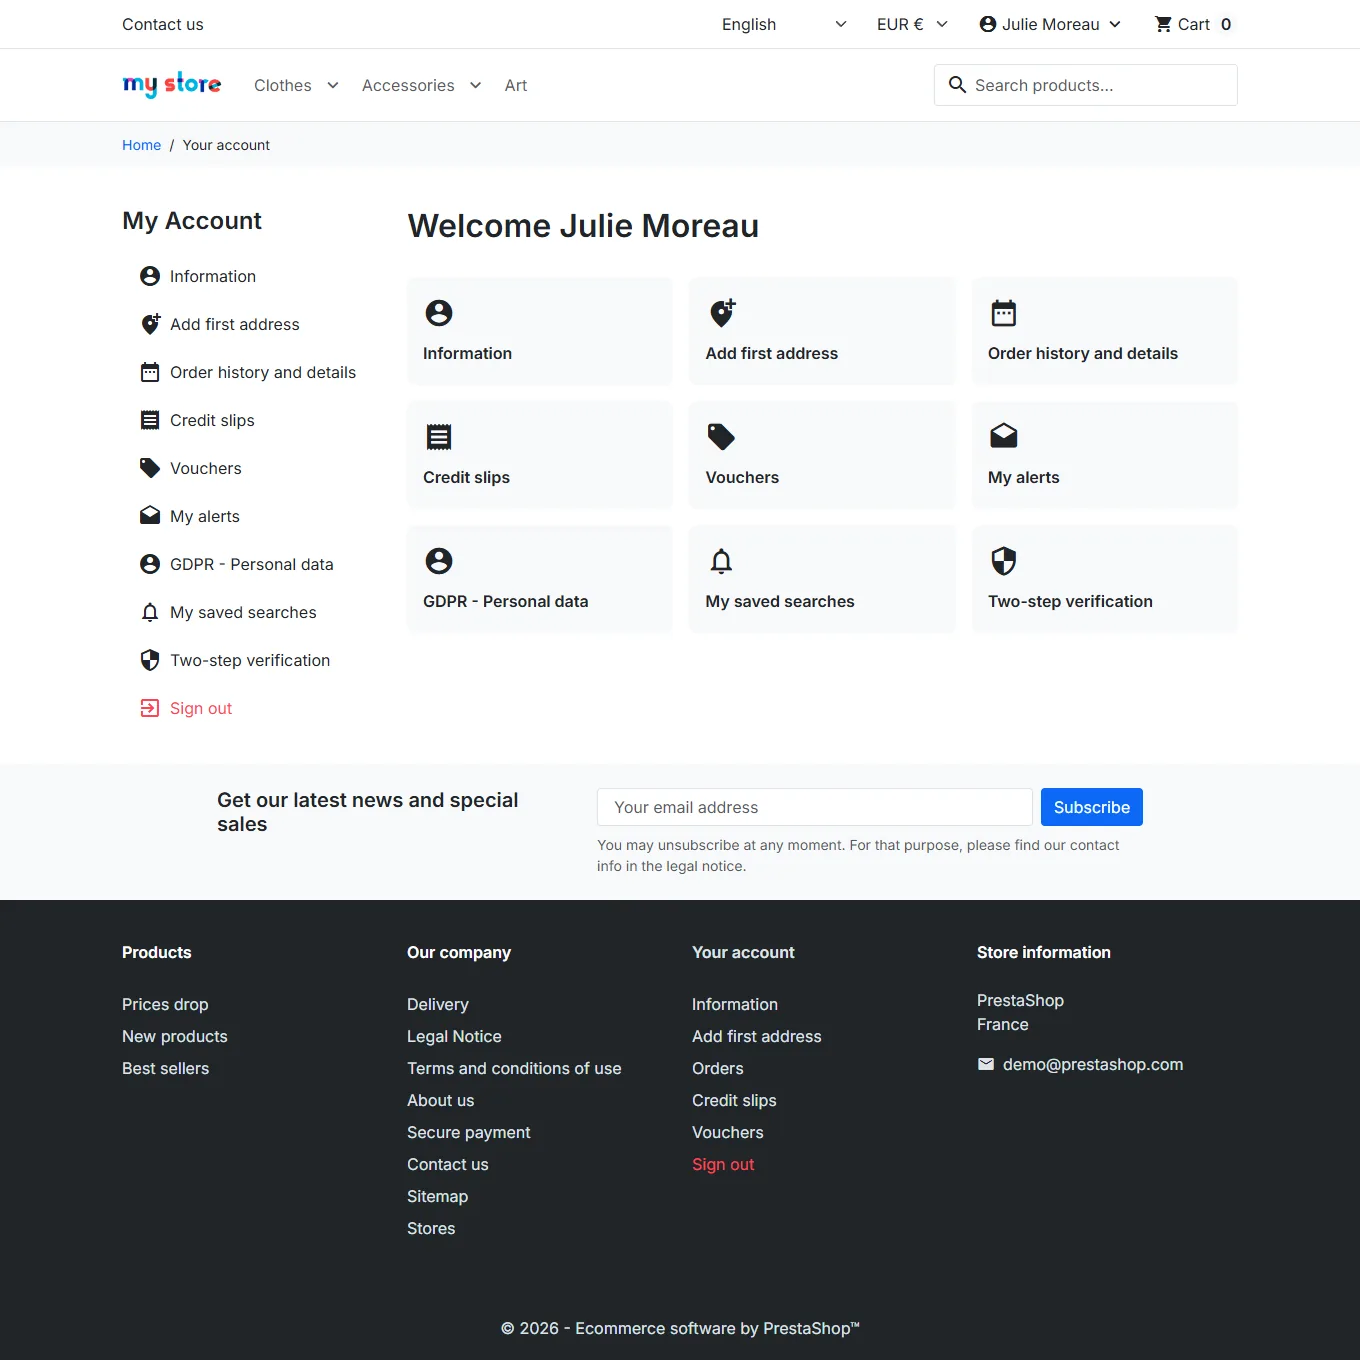
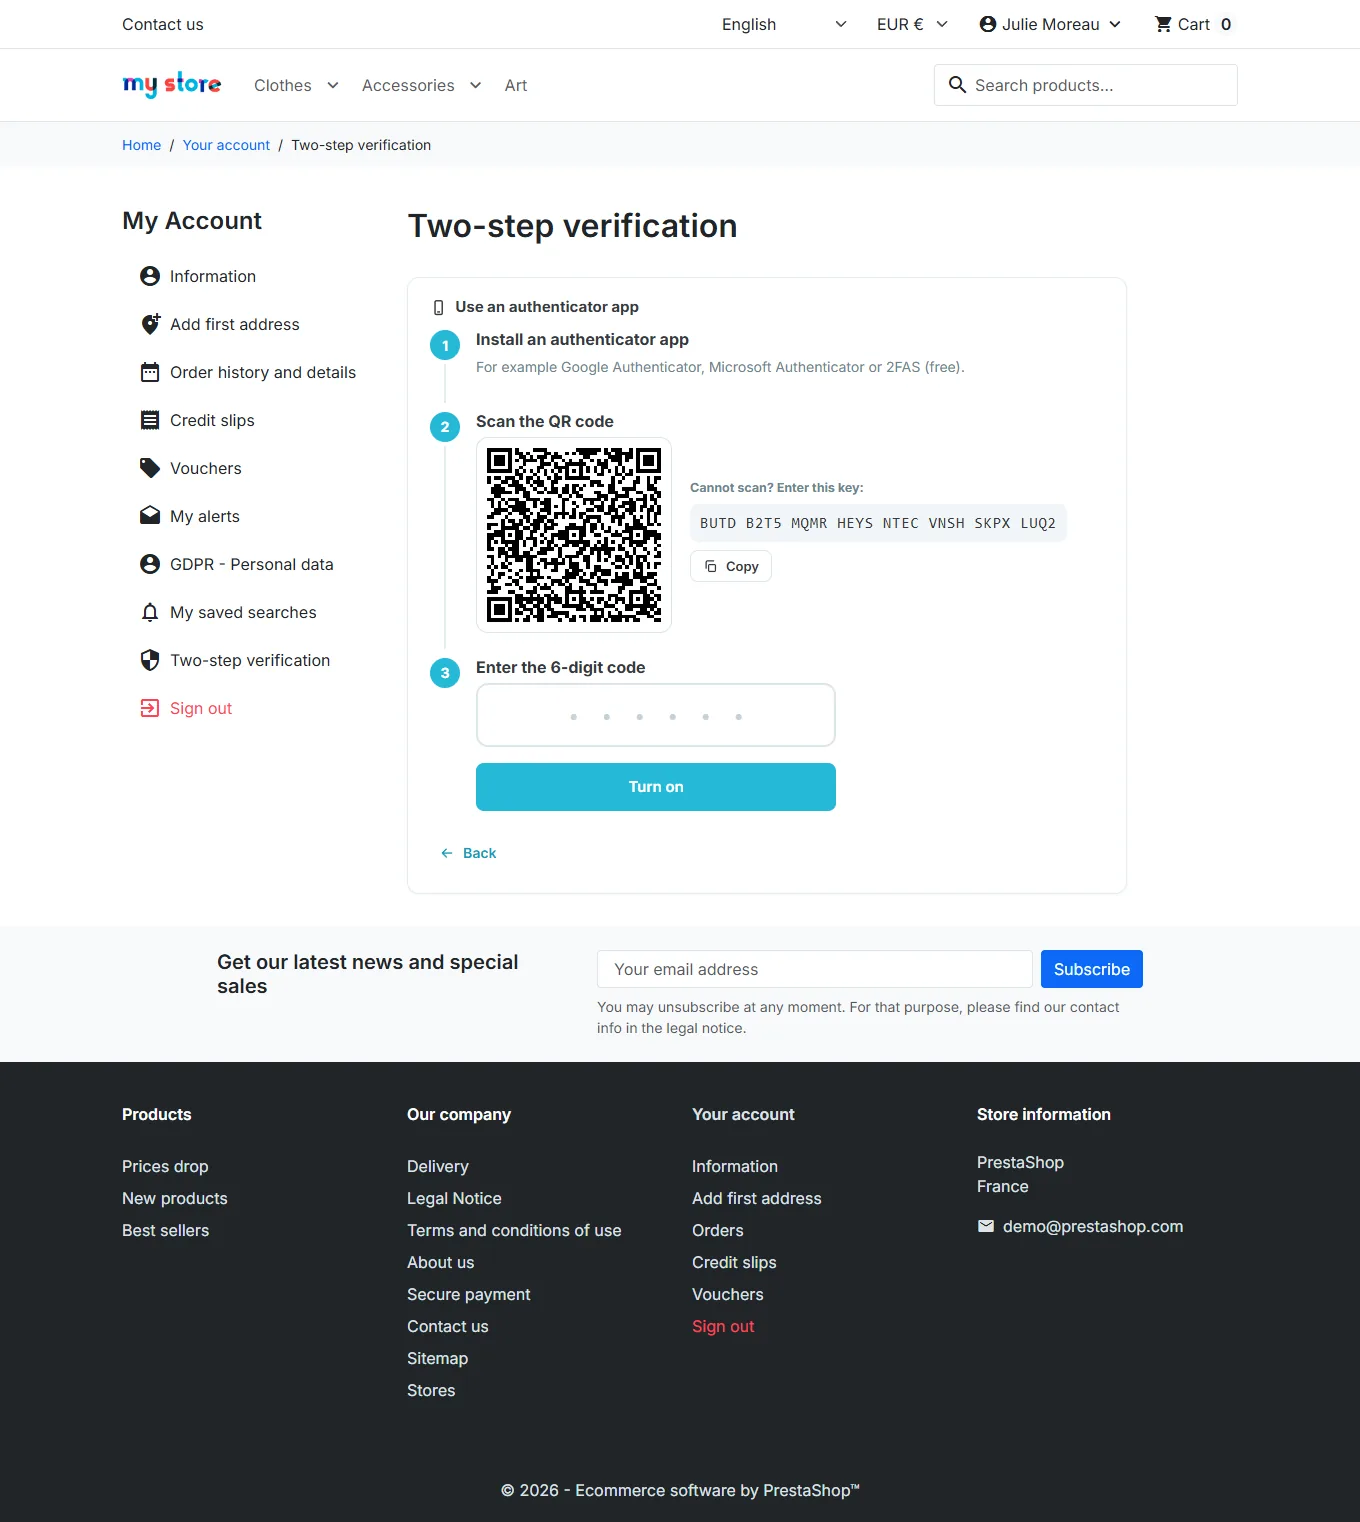
Turn on Offer 2FA to customers in Settings. A Two-step verification page appears in My account (Classic and Hummingbird themes). You choose the methods offered: authenticator app, code by e-mail, or both. You can also make verification mandatory for some customer groups, for example your B2B group.
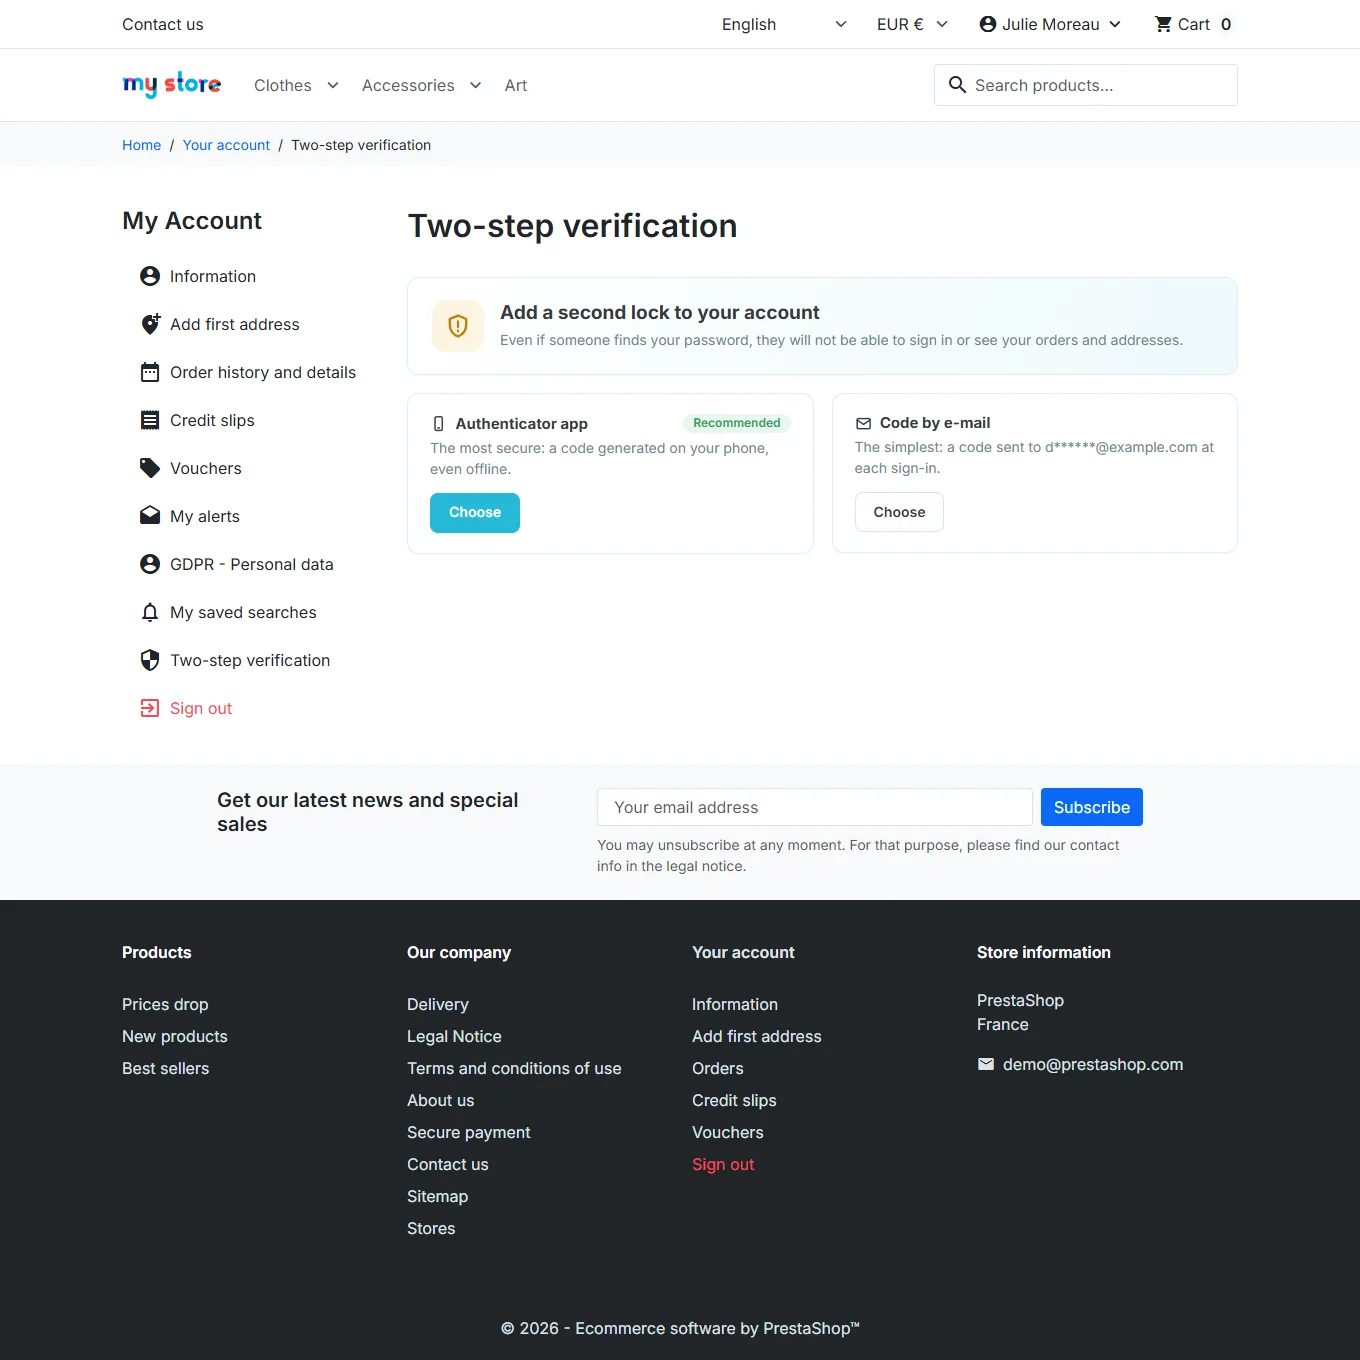
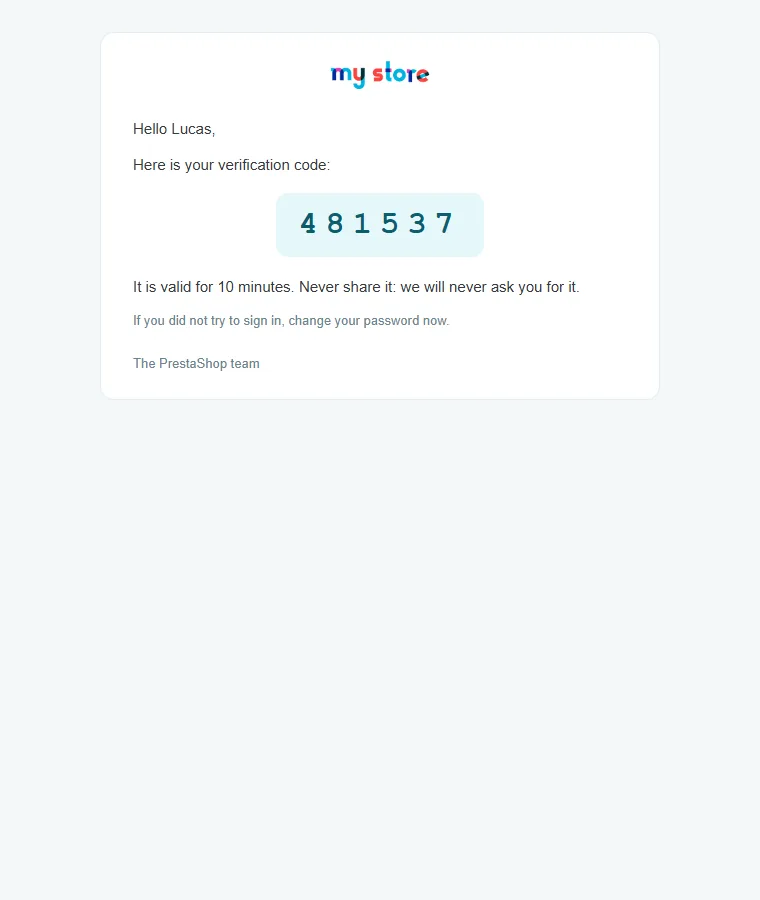
The customer chooses their method: the authenticator app, recommended because it works even offline, or the code by e-mail, simpler (6 digits, valid for 10 minutes, resending limited to once per minute).
Activation with an app follows the same three steps as for employees, then the customer receives their 10 recovery codes.
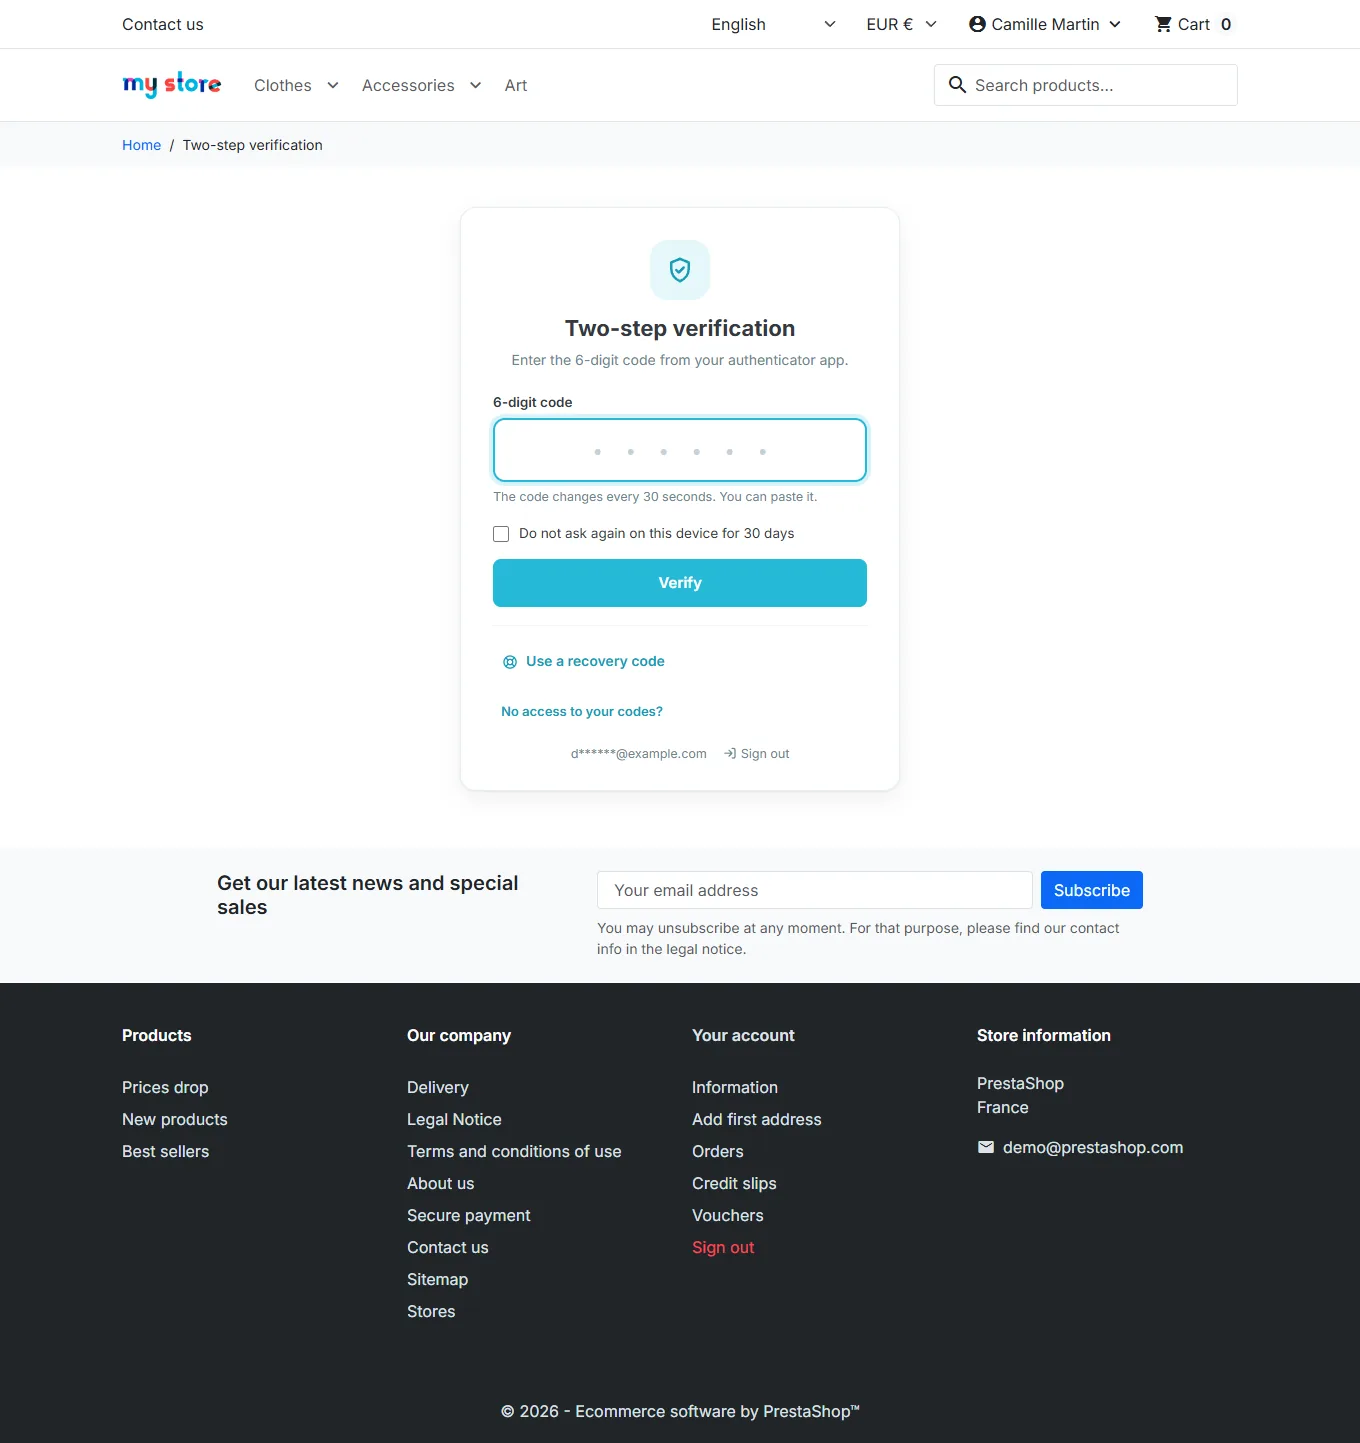
At each sign-in, including from the checkout, a social login or after a password reset, the customer must enter their code before accessing their account, orders or addresses. If they wish, they can choose not to be asked again on this device for 30 days.
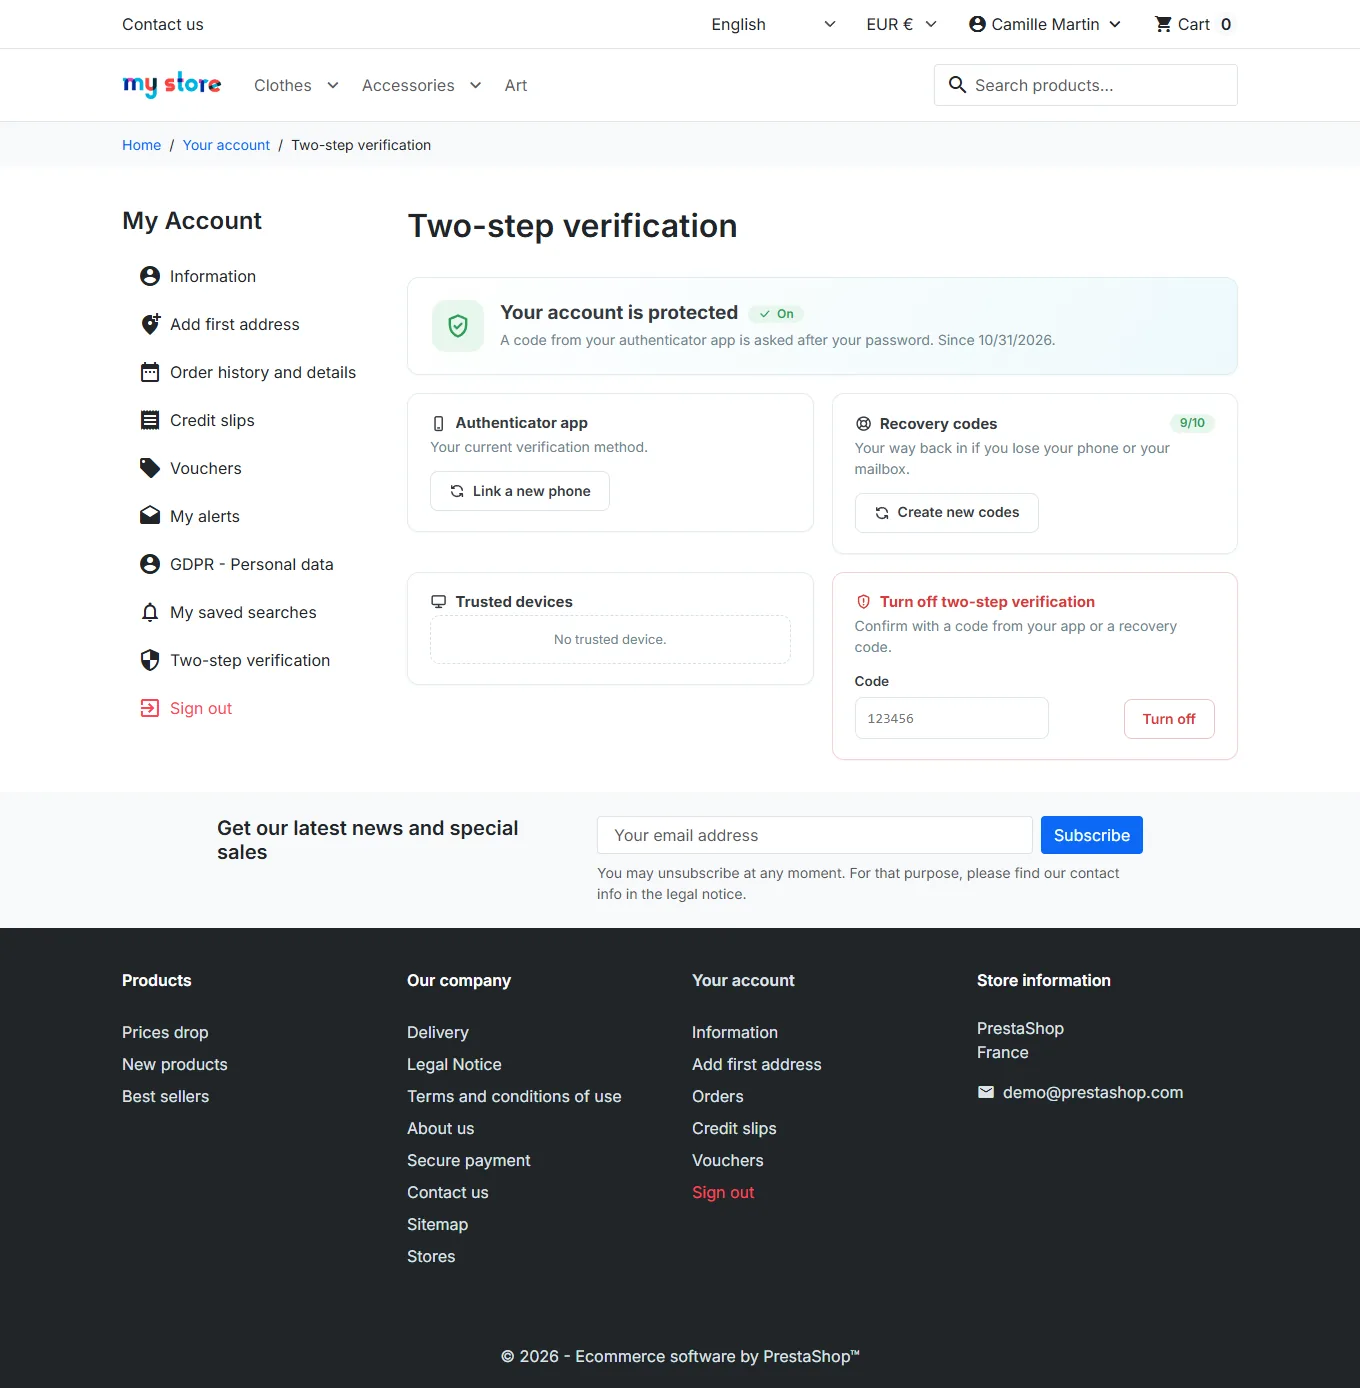
From the same page, the customer manages their method, recovery codes and trusted devices, and can turn off verification unless their group requires it.
With the e-mail method, the code is sent automatically when the verification page opens, using a template translated into all 8 languages.
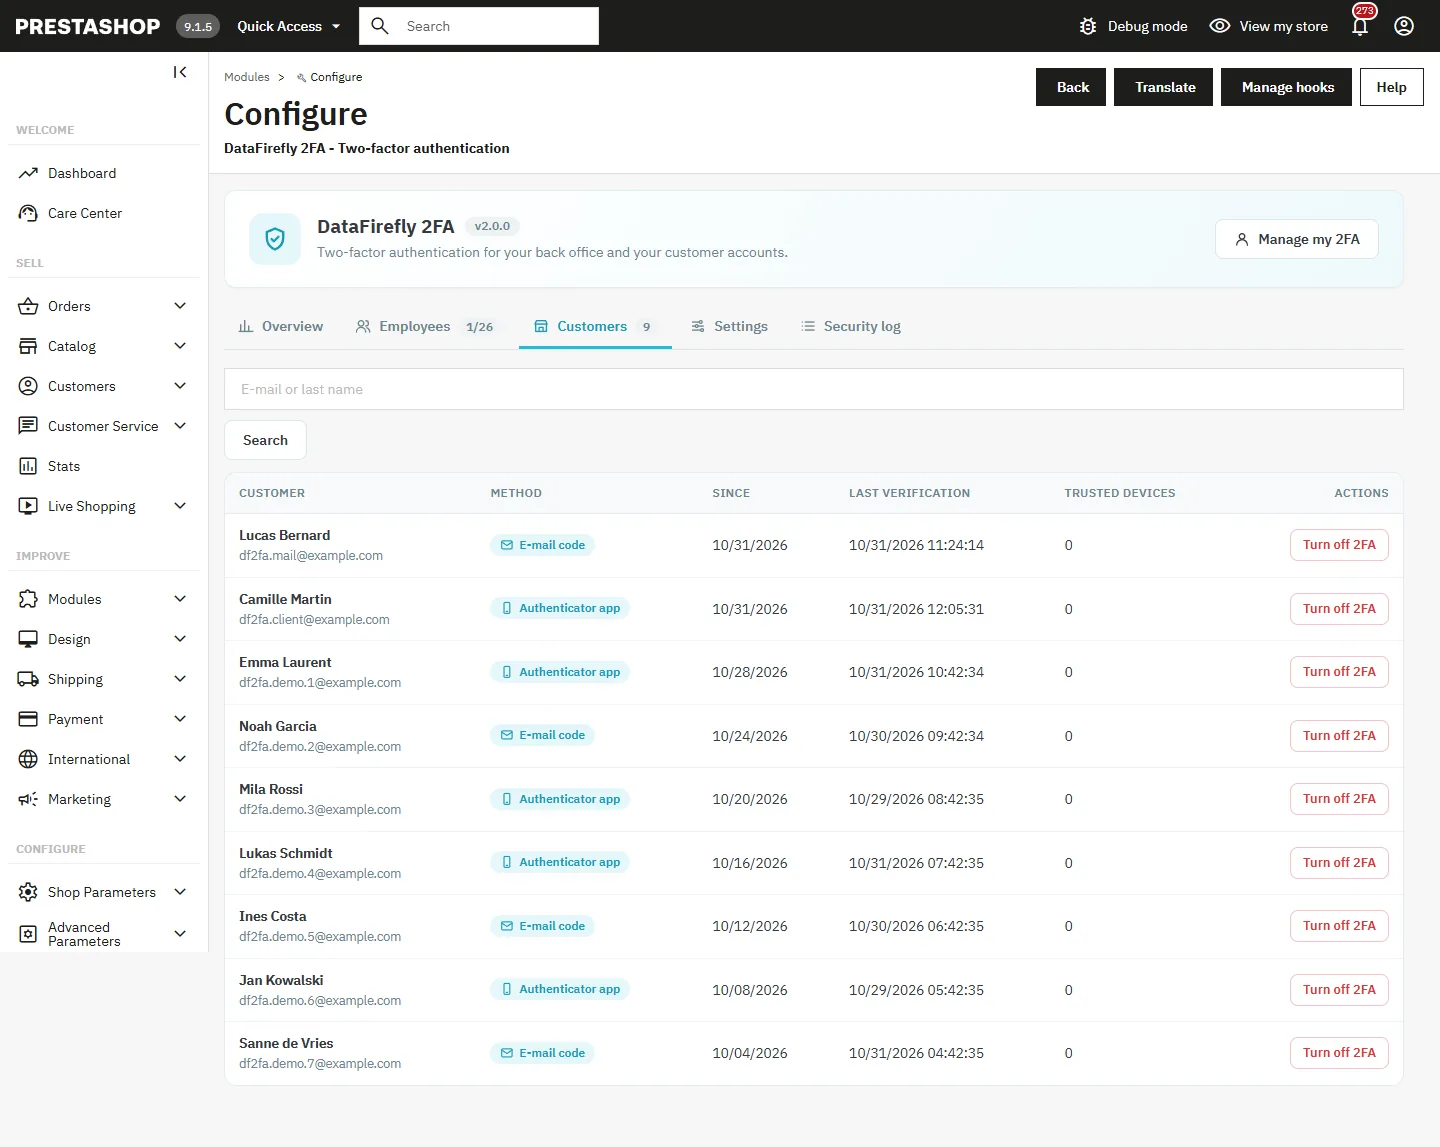
In the back office, the Customers tab lists protected customers (method, date, last verification, devices) and lets you unlock an account or turn off its 2FA after checking the customer’s identity.
Security log
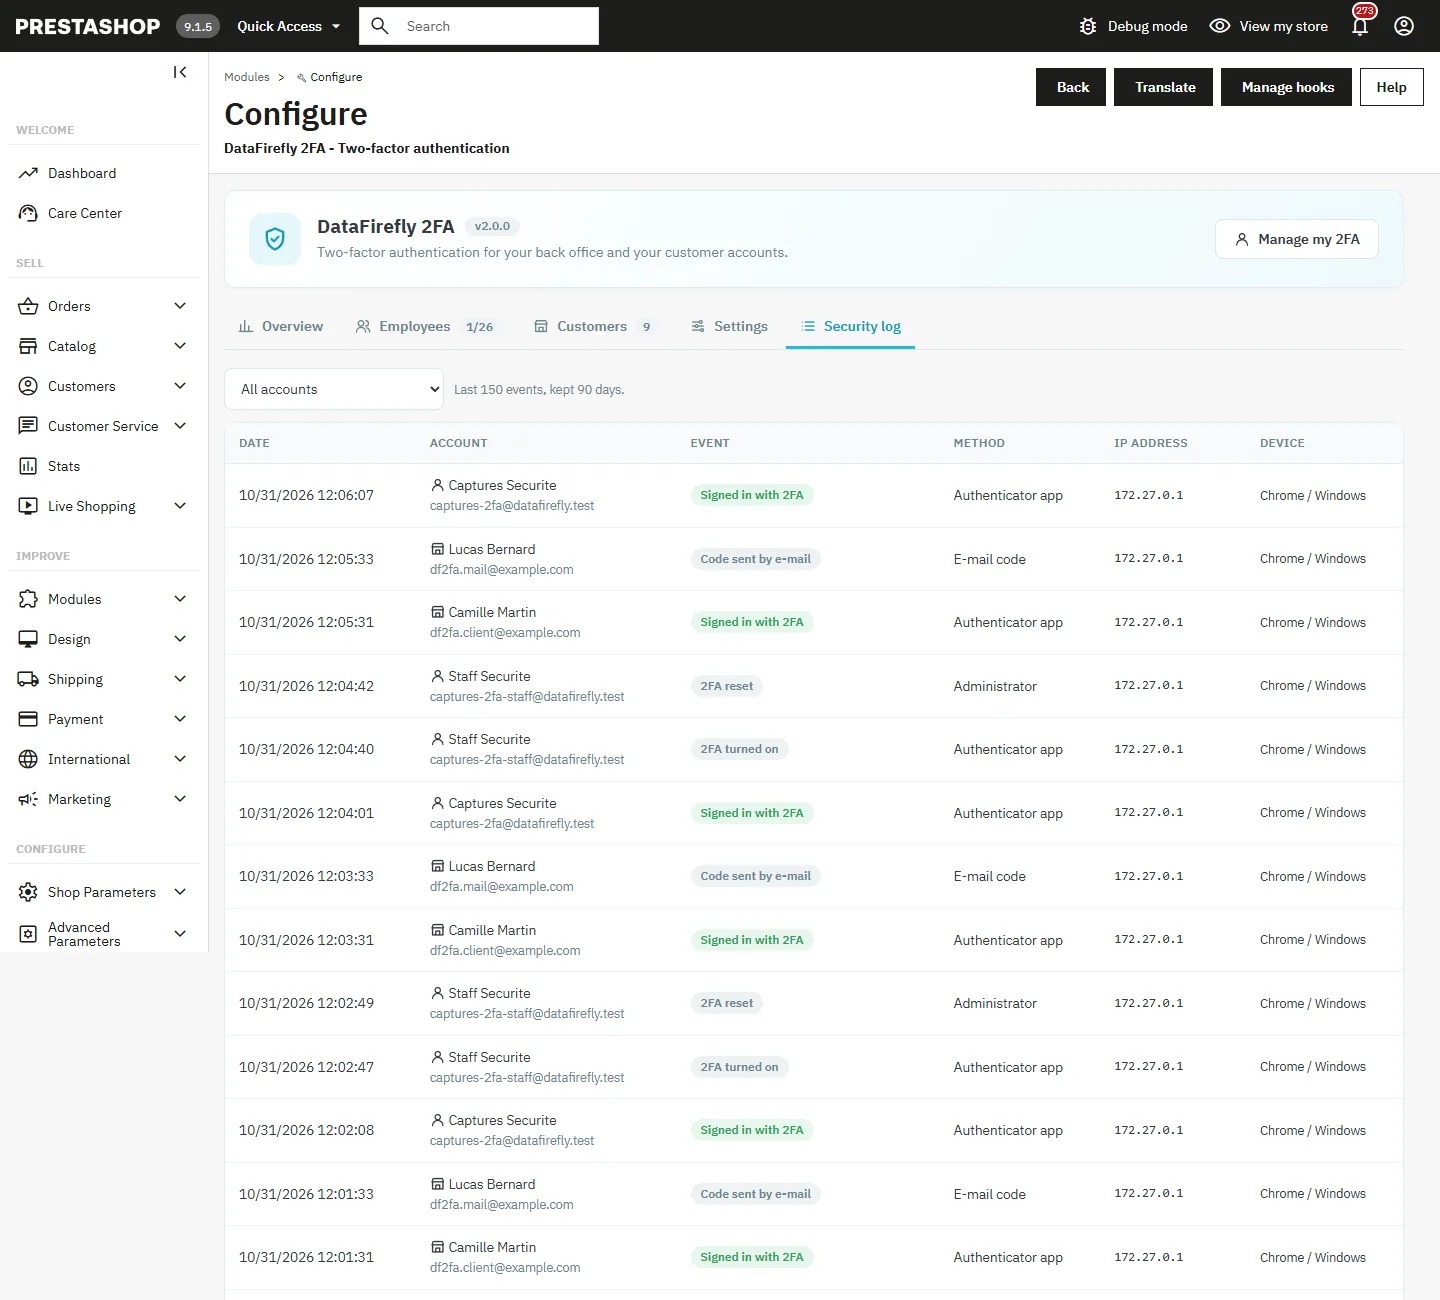
The log records verified sign-ins, wrong codes, lockouts, activations and deactivations, resets, recovery code use, trusted devices and keys, with the date, account, method, IP address and device. It can be filtered by employees or customers and is purged automatically according to the chosen retention period.
What the module protects
- Every back-office page: legacy pages (including on PrestaShop 8), Symfony pages, AJAX calls (401 response), forms submitted by POST, file manager.
- The verified state is kept on the server and tied to the employee’s PrestaShop session: a new sign-in always starts unverified.
- Secrets encrypted in the database, recovery codes stored as hashes with a server secret key, constant-time comparisons, protection against replay and brute force, CSRF tokens on every action.
The webservice (API keys) and the PrestaShop 9 Admin API (OAuth credentials) do not go through an employee sign-in: they are outside the scope of 2FA. Protect these keys and limit their permissions.
Troubleshooting
“This code would be valid X minute(s) away”
The phone’s clock is out of sync. Turn on automatic date and time on the phone, then try again. Also check the server clock (timedatectl).
“This code was already used”
The module refuses replay: wait for the next code in the app (30 seconds).
Account locked after too many wrong codes
Wait for the lockout to end, ask a SuperAdmin to lift it from the Employees tab, or run php bin/console df2fa:reset email@exemple.com --unlock.
No SuperAdmin can sign in any more
From the server, php bin/console df2fa:reset email@exemple.com removes 2FA from the given account; the employee signs in again with their password and sets up 2FA again.
The security key is not offered
The site must be served over HTTPS, the option must be turned on in Settings and the OpenSSL extension must be present on the server.
Uninstalling
By default, uninstalling removes the module’s tables, settings, overrides and pages. If the Keep the data when uninstalling option is on, encrypted secrets, keys and the log are kept for a later reinstall.
Release notes
2.0.0 (31 October 2026)
- Security: rebuilt access control. PrestaShop 8 legacy pages covered, bypasses through
&logoutand through the AJAX header fixed, strict allow list, verified state tied to the session on the server, file manager covered. - Protection against code replay, clock drift detection, stronger recovery codes (10 codes, hashed with a server key), reset restricted to SuperAdmins with a CSRF token.
- New: security keys and passkeys (WebAuthn), trusted devices, policy per profile, dashboard, security log, e-mail alerts,
df2fa:resetcommand. - New: customer 2FA by app or by e-mail code, optionally mandatory per group.
- Redesigned interface: full-screen verification page and enrolment wizard, My 2FA page, entry in the employee menu for all profiles.
- Complete translations in 8 languages (back office, front office, e-mails). Tested on PrestaShop 8.2.1 and 9.1.5, PHP 7.4 to 8.5.
1.1.1 (8 September 2026)
- Fixed the employees’ 2FA status table, interface translated into 7 languages.
1.1.0 (2 July 2026)
- PrestaShop 9 compatibility, secret encryption, hashed recovery codes, lockout after 5 wrong codes, local QR code.
1.0.0 (12 March 2025)
- First version: TOTP, mandatory or optional mode, recovery codes, SuperAdmin reset.