
Google, Apple and Facebook Login for PrestaShop: DataFirefly Social Connect Documentation
Install and configure Google, Apple and Facebook login on PrestaShop 8 and 9: provider credentials, checkout buttons, Connected accounts page, dashboard, webhook, GDPR.
Overview
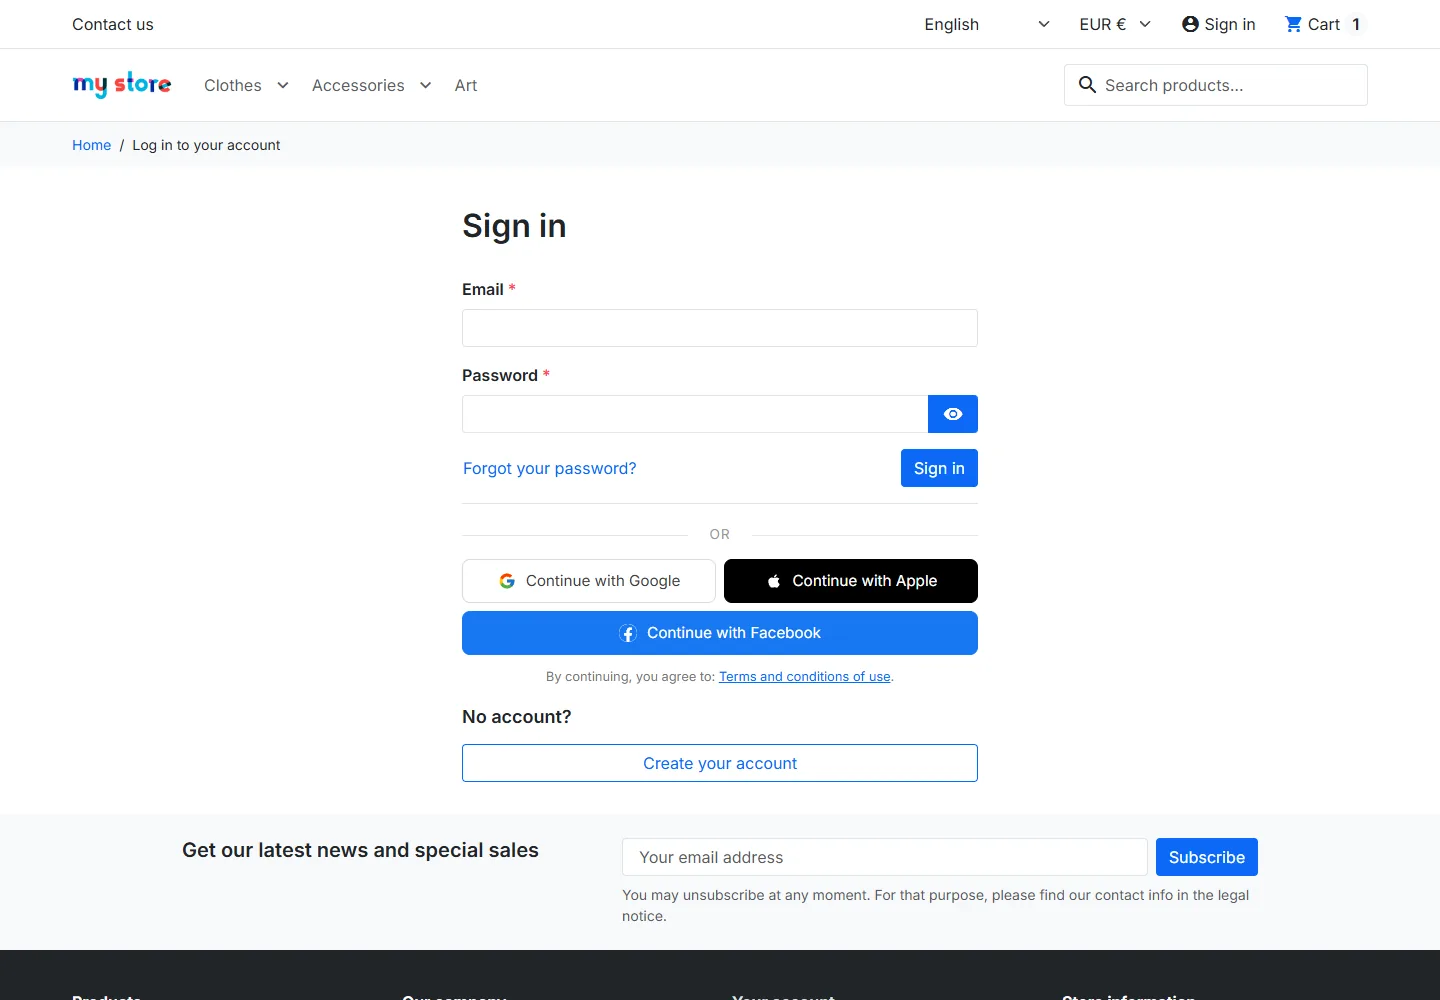
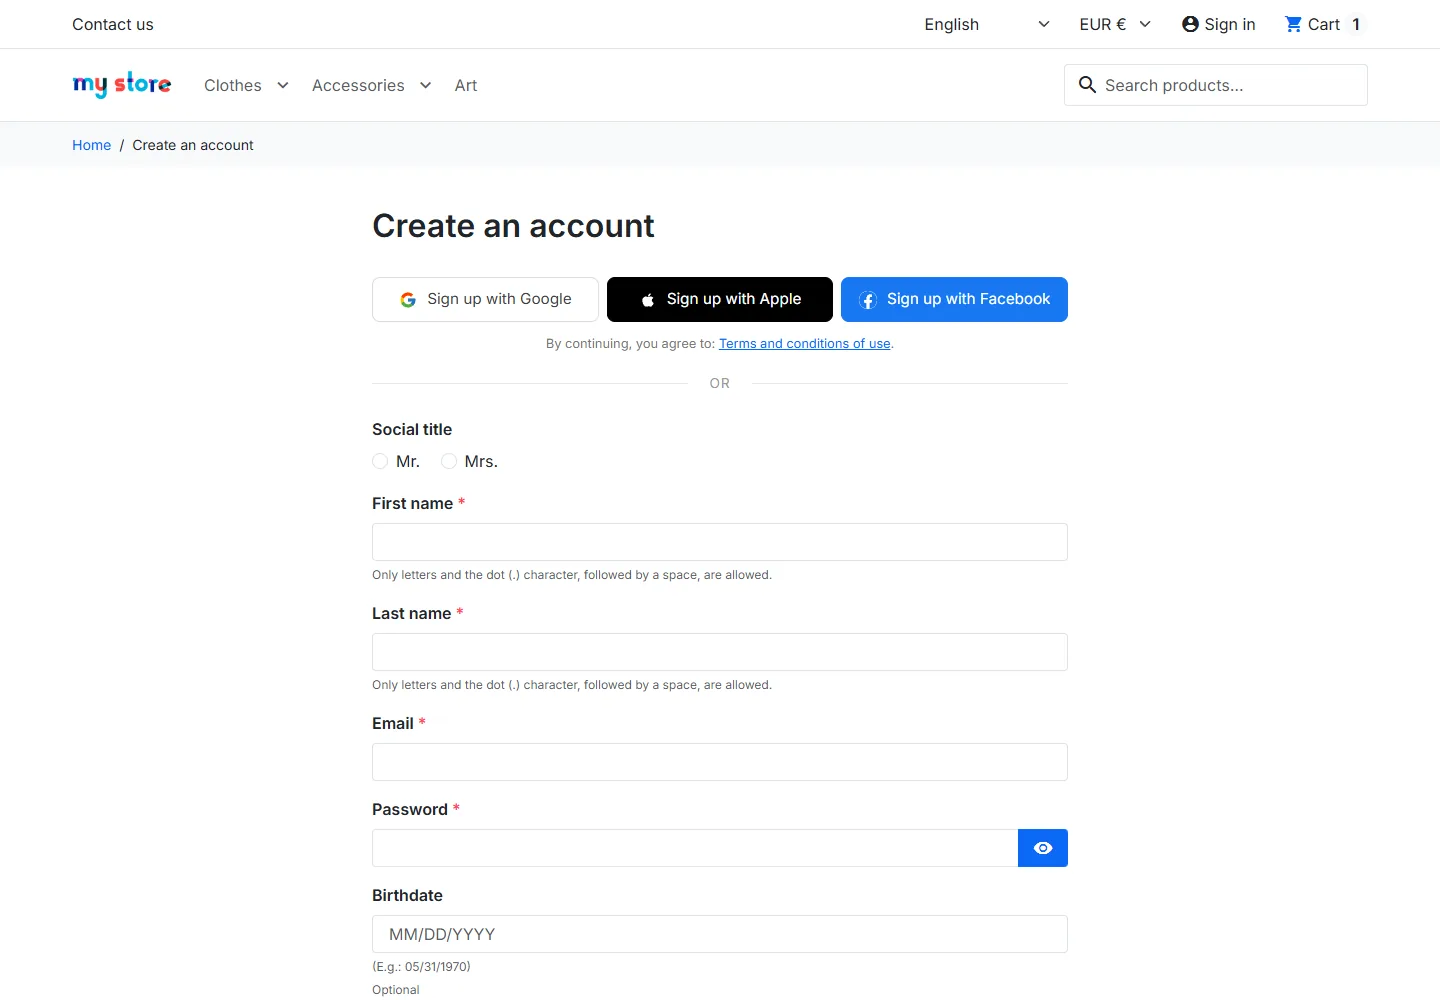
DataFirefly Social Connect adds one-click sign-in and sign-up with Google, Apple and Facebook to PrestaShop 8 and 9. The buttons appear on the login page, the registration page and, optionally, in the checkout. Customers manage their linked accounts from a “Connected accounts” page in their customer area.
The module also includes an analytics dashboard (conversion per provider, devices, login hours, revenue), an optional welcome voucher and a signed webhook for your CRM.
This documentation covers version 1.2.0. It is compatible with PrestaShop 8.0.0 to 9.x and PHP 7.4 to 8.5 (PHP 8.1 minimum with PrestaShop 9), with cURL and OpenSSL. No Composer dependency is required.
Installation
- Download the module archive from your customer account on datafirefly.com.
- In the back office, open Modules > Module Manager > Upload a module and drop the ZIP.
- Click Install. The module creates 5 tables (
ps_dfsc_identity,ps_dfsc_log,ps_dfsc_stats_daily,ps_dfsc_button_click,ps_dfsc_consent) and saves its default settings. - Click Configure. As long as no provider is active, the module opens the Providers tab directly and the buttons stay hidden on the shop.
Upgrading from version 1.0.0
Upload the new ZIP in the Module Manager: the upgrade runs automatically. Your credentials, settings, customer links and statistics are kept. The upgrade adjusts the indexes of the links table, registers the new hooks, adds the new settings and removes the hidden admin tab from 1.0.0, which is no longer needed.
After the upgrade, open the Providers tab and compare the return URIs shown with the ones registered at Google, Apple and Facebook. They are now always built in the shop’s default language. On a multilingual shop whose back office used another language, the URI may have changed.
Upgrading to version 1.2.0
Upload the 1.2.0 ZIP in the Module Manager: the upgrade runs automatically from 1.0.0 or 1.1.0, and customer links, settings and statistics are kept. Main changes:
- Facebook security: an email returned by Facebook no longer signs in an existing customer automatically, because Facebook does not say whether the address was confirmed. The customer signs in with their password, then connects Facebook from Connected accounts. A new option restores the previous behaviour; it is off by default, including after the upgrade.
- Google security: PKCE and ID token checks (issuer, audience, expiry and nonce).
- Accounts without email: an account created through Apple or Facebook without an email address can no longer disconnect its only provider, which is its only way in.
- GDPR: the links and consents of a customer deleted with the “do not allow registration” option are now erased too.
- Fixes: “Logins over time” chart empty after the end of daylight saving time, Facebook icon, “or” separator moved below the buttons on the registration page and in the checkout, translated events in Recent activity, button styles no longer applied to the buttons of DF Simple Checkout.
Provider setup
Each provider requires credentials created in its developer console. The Providers tab shows the exact return URI to copy into each console: the slightest difference causes a redirect_uri_mismatch error.
These URIs are built in the shop’s default language and do not change with the visitor’s language: one URI per provider is enough. The customer then comes back in their own language.
A provider only appears on the shop if it is enabled and all its credentials are filled in. The banner of the tab shows whether each one is active, incomplete or off.
Secret fields (Client secret, App secret, Apple private key) are never displayed again once saved. Leave them empty to keep the current value.
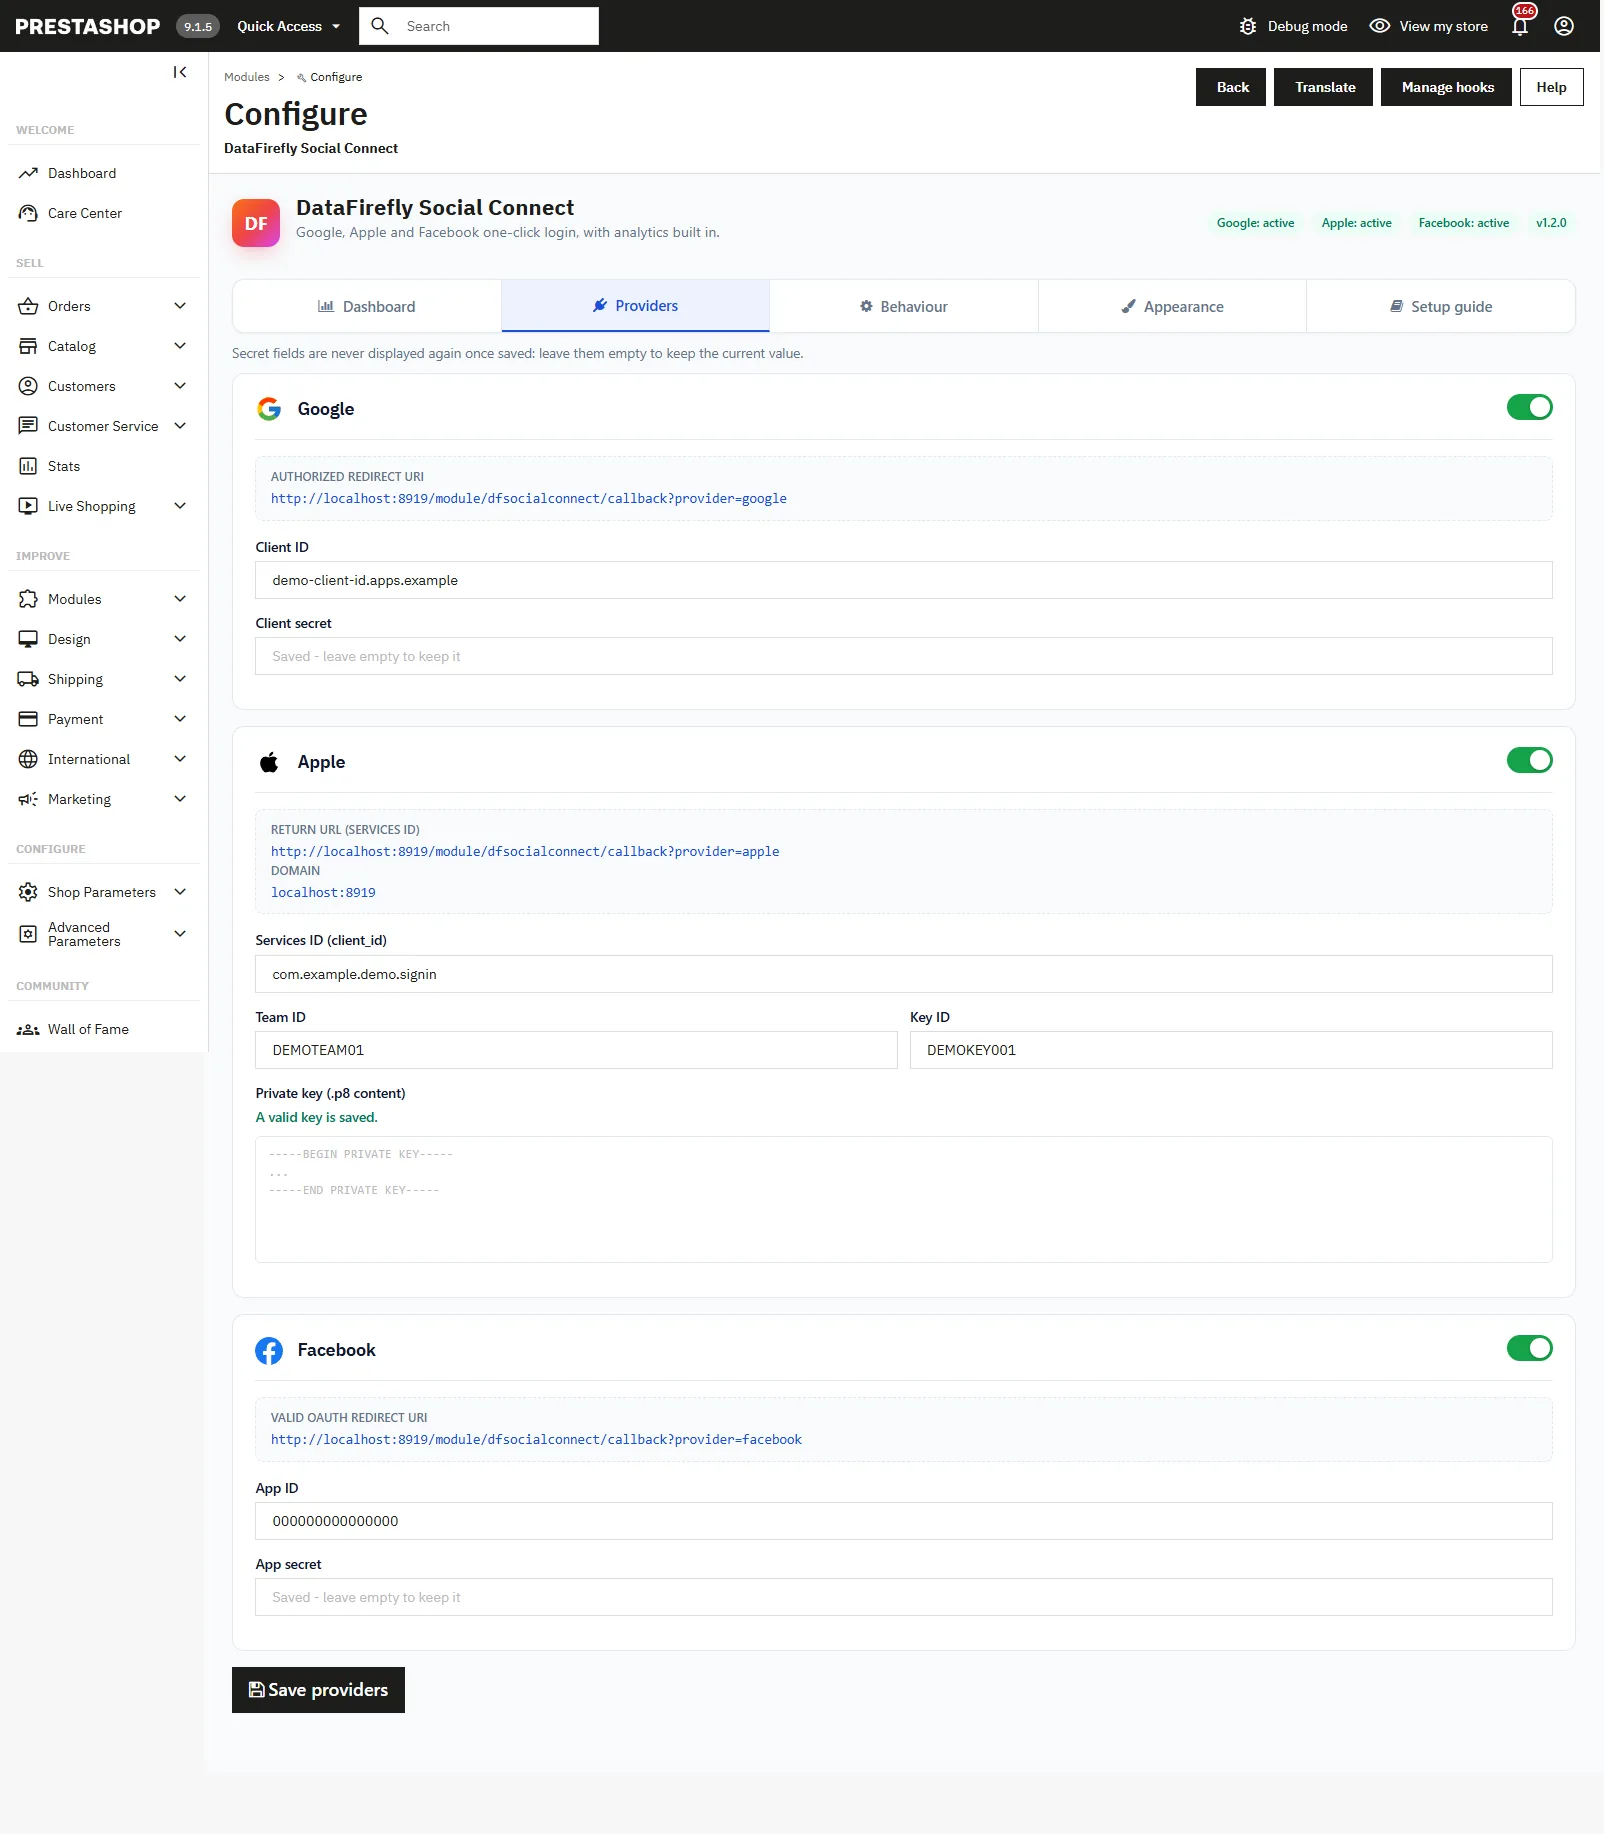
- Open the Google Cloud Console, Credentials section.
- Create or select a project, then Create credentials > OAuth client ID, type Web application.
- Under Authorized redirect URIs, paste the URI shown in the module (format:
https://your-shop.com/en/module/dfsocialconnect/callback?provider=google). - Paste the Client ID and Client secret into the module, enable Google and save.
Apple
- Open Apple Developer, Identifiers (paid Apple Developer account required).
- Create a Services ID (not an App ID). Its identifier, for example
com.yourshop.signin, is the Services ID to enter in the module. - Enable Sign in with Apple on this Services ID, declare the domain shown by the module and set the return URI (provider=apple) as the Return URL.
- Under Keys, create a key with Sign in with Apple enabled and download the
AuthKey_XXXXXXXXXX.p8file. Apple only lets you download it once. - In the module, enter the Services ID, the Team ID (10 characters, top right of the Apple console), the Key ID (10 characters) and the full content of the .p8 file, including the BEGIN and END lines.
- Enable Apple and save. The module checks the key immediately and shows “A valid key is saved.” or an error.
The client_secret Apple requires is a JWT signed with ES256 using your .p8 key. The module generates it at every login with a 5-minute validity: no manual rotation is needed.
Customers who choose to hide their email receive an @privaterelay.appleid.com address. For your order emails to reach them, register your sending domain in the Private Email Relay service of your Apple Developer account.
Apple sends the customer back to the shop with a POST request coming from its own site. Browsers do not attach the PrestaShop cookie to it. The module detects this case and replays the request from the shop, which keeps the customer’s session and cart. Nothing needs to be configured on your side.
- Open Meta for Developers and create an app.
- Add the Facebook Login product and request the
emailpermission. - In Facebook Login > Settings, paste the return URI shown by the module (provider=facebook) into Valid OAuth Redirect URIs.
- Copy the App ID and App secret (Settings > Basic) into the module, enable Facebook and save.
The module uses Facebook Graph API v23 and adds appsecret_proof to every call: a stolen access token cannot be reused without your app secret.
Facebook does not say whether the email of an account was confirmed. By default, a Facebook email therefore never attaches the provider to an existing customer account: see the “Also trust Facebook emails for auto-link” option in the Behaviour tab.
Customer journey
Sign-in and account creation
When the customer comes back from Google, Apple or Facebook, the module proceeds in this order:
- If this social account is already linked to a customer of the shop, the customer is signed in.
- If the email matches an existing customer and the provider has verified it and auto-linking is enabled, the provider is attached to that account and the customer is signed in. For Facebook, the email only counts as verified when the “Also trust Facebook emails for auto-link” option is enabled.
- If the email matches an existing customer but cannot be attached, no account is created. The customer sees the message: “An account already exists with this email address. Sign in with your password, then connect this provider from “Connected accounts” in your account.”
- Otherwise, an account is created with the first name, last name and email sent by the provider, in the language the customer was browsing in, with a random hashed password.
Disabled accounts cannot sign in. On a multistore setup without shared customers, a social account never signs in a customer from another shop.
At login, the module fires the native actionAuthentication hook and, for a new account, actionCustomerAccountAdd. Automatic cart rules are recalculated, as with the PrestaShop form. If the PrestaShop confirmation email option is enabled, the new customer receives the usual welcome email.
Return to the original page
After login, the customer returns to the page they started from, for example the checkout. Otherwise, they land on the page chosen in the Behaviour tab. Only addresses on your shop are accepted: a crafted link cannot send the customer to another site.
“Connected accounts” page
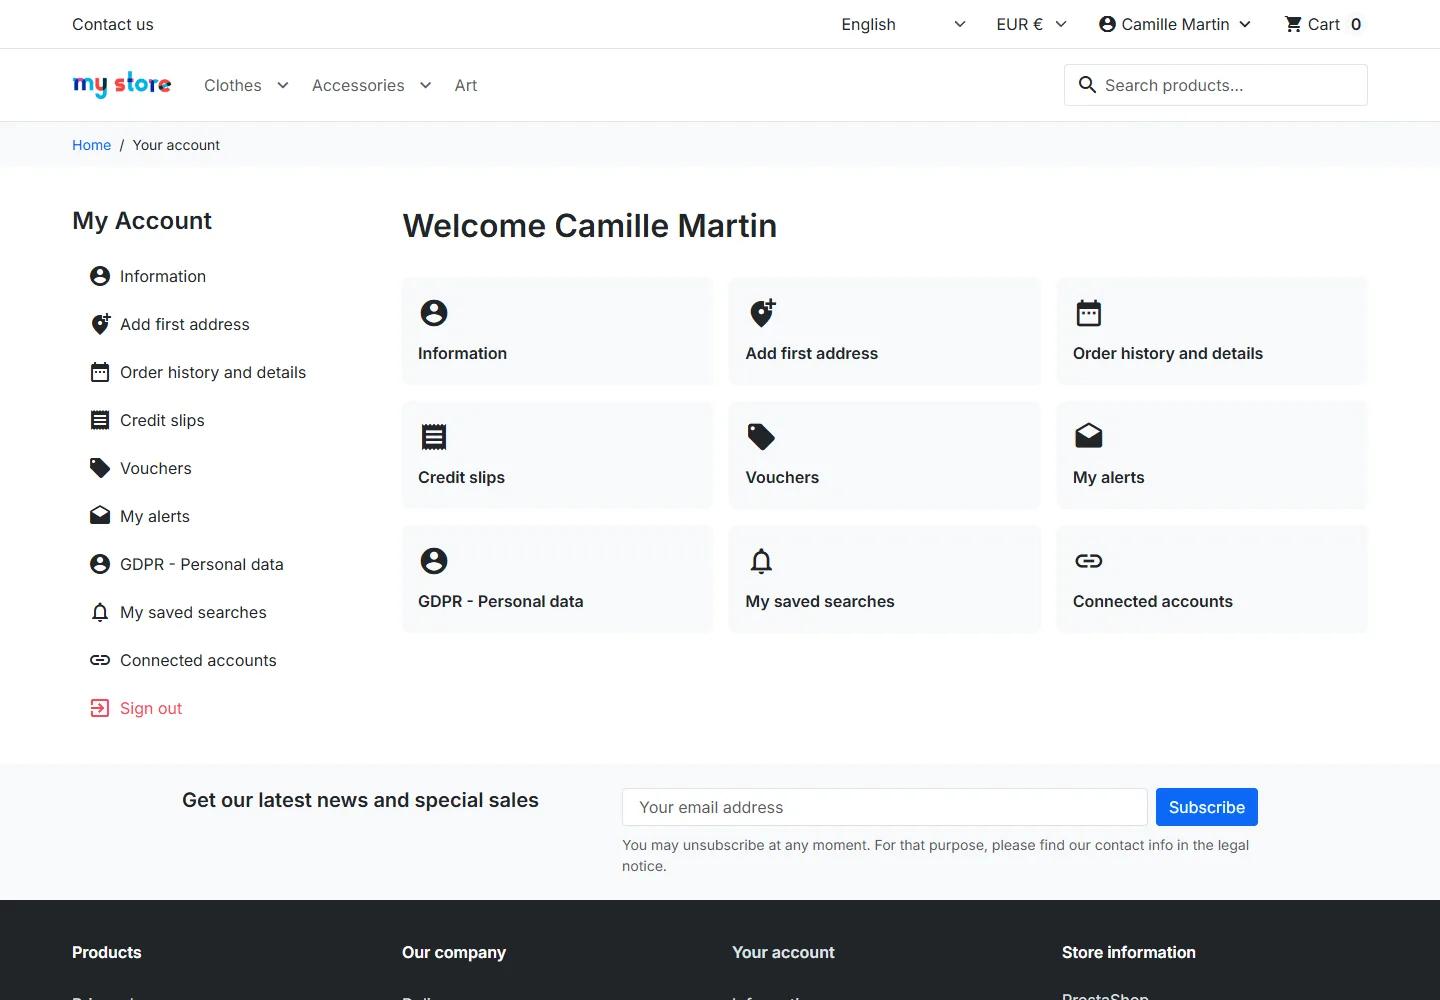
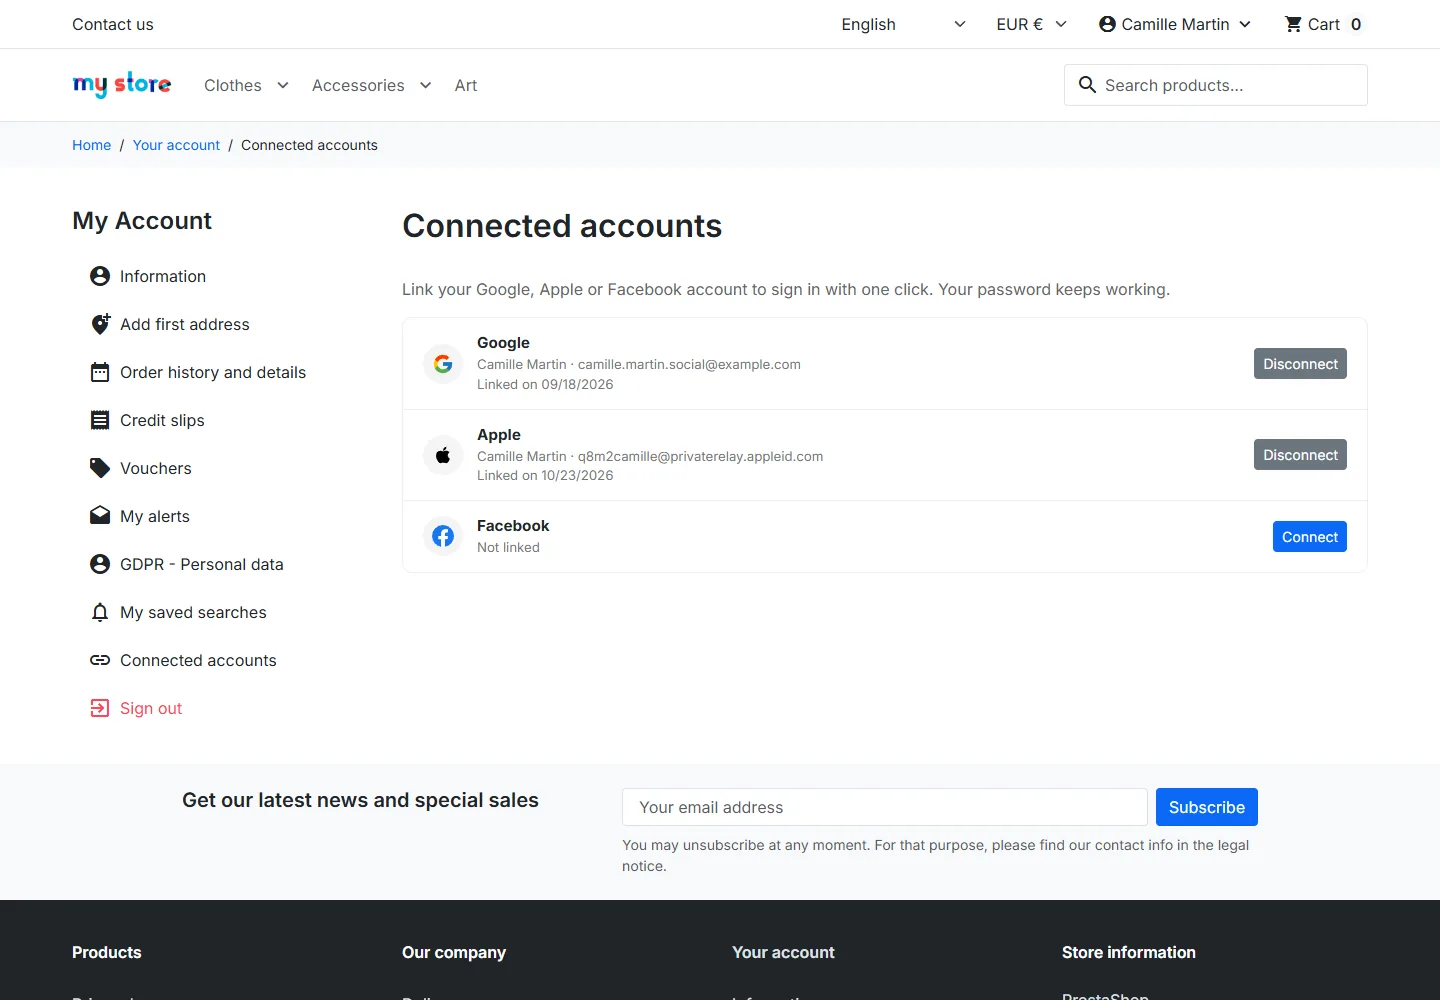
A “Connected accounts” tile is added to the My account page (Classic and Hummingbird themes). It opens a page listing each provider with its status. For a linked provider, the page shows the name, the email, the link date and the avatar if it was imported.
- Connect: starts the sign-in with the provider and attaches it to the customer’s account.
- Disconnect: removes the link after confirmation. If it is the last linked account, the customer is first asked to set a password with “Forgot your password?” to keep access to their account. An account created without an email address (Apple or Facebook) cannot disconnect its only provider: the page shows “Only way to sign in”.
Behaviour tab
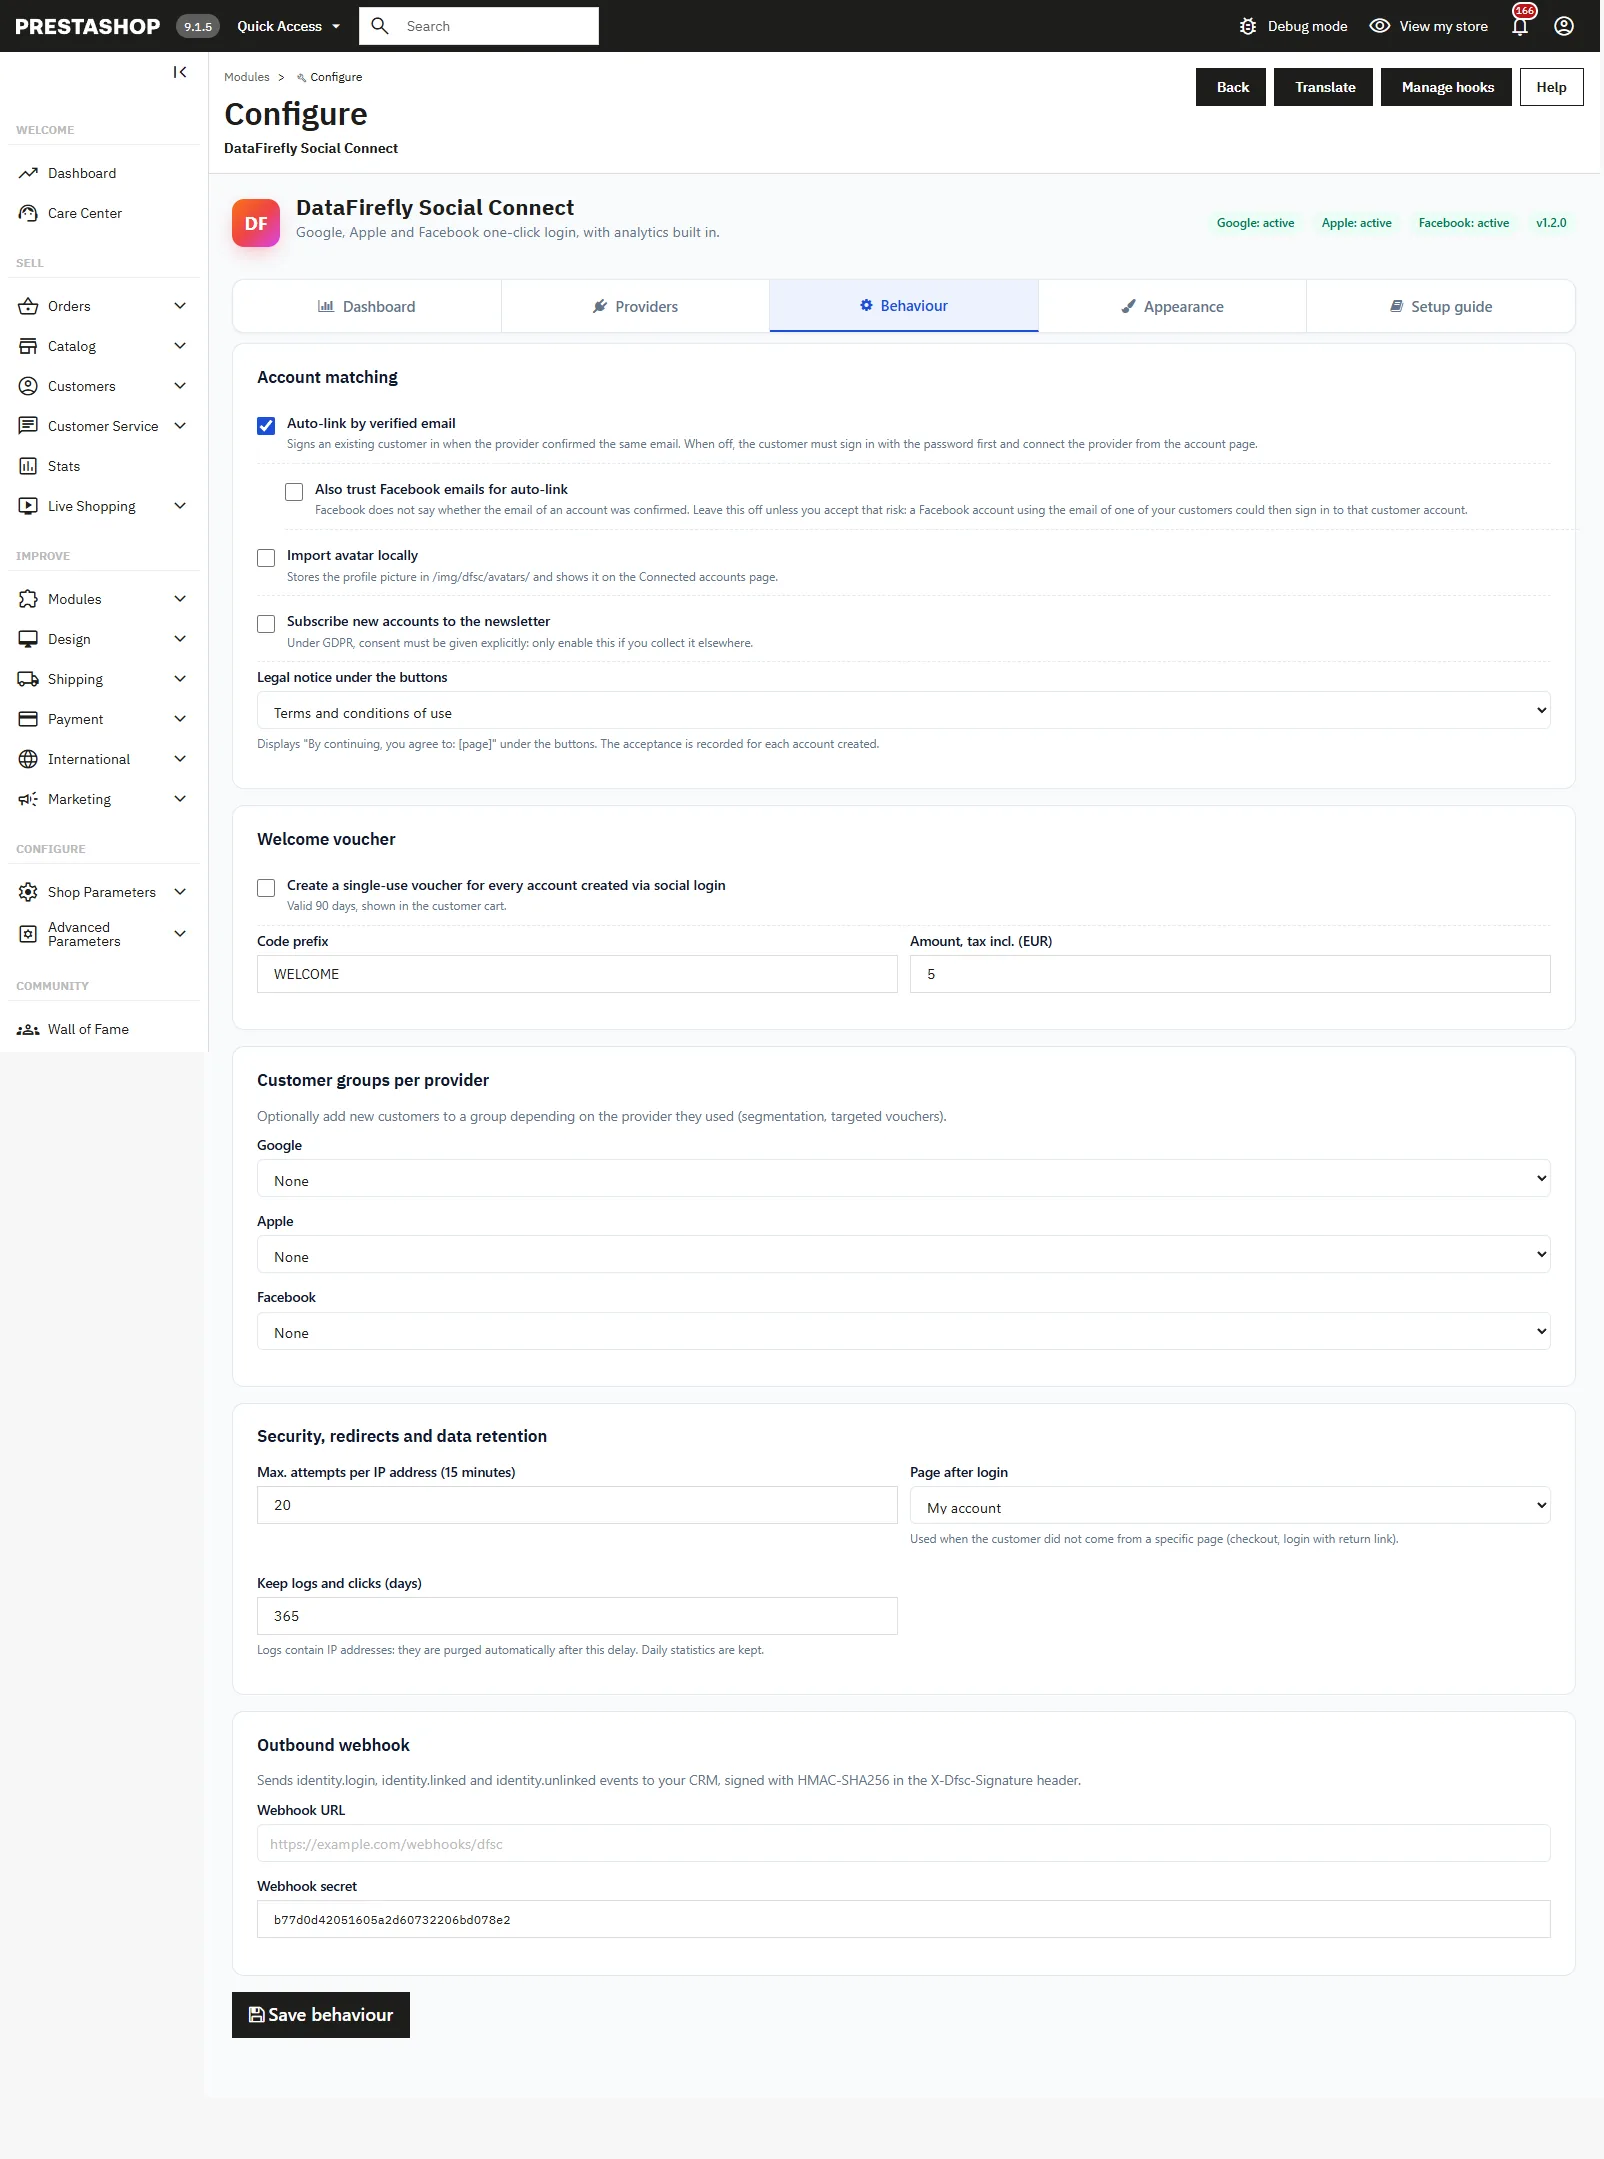
- Auto-link by verified email: attaches the provider to an existing account when the provider has confirmed the same email. When off, the customer must sign in with their password and then connect the provider from their account. Enabled by default.
- Also trust Facebook emails for auto-link: off by default. Facebook does not say whether the email of an account was confirmed: once this option is on, a Facebook account using the email of one of your customers could sign in to that customer account.
- Import avatar locally: stores the profile picture in
/img/dfsc/avatars/(HTTPS only, 2 MB maximum, JPEG, PNG, GIF or WebP checked) and shows it on the Connected accounts page. - Subscribe new accounts to the newsletter: GDPR requires explicit consent. Only enable this option if you collect that consent elsewhere.
- Legal notice under the buttons: choose a CMS page (your terms or your privacy policy). The sentence “By continuing, you agree to: [page]” appears under the buttons and the acceptance is recorded for each account created. Choose “None” to hide the notice.
- Welcome voucher: for each account created through a provider, creates a single-use voucher, valid for 90 days and shown in the customer’s cart. Set the code prefix (letters, digits, hyphens, 40 characters maximum) and the amount, tax incl., in the default currency. The code looks like
WELCOME-GOOGLE-A1B2C3. The customer is told about it as soon as they sign in. - Customer groups per provider: adds new customers to the chosen group depending on the provider they used.
- Max. attempts per IP address (15 minutes): number of logins started from the same IP over 15 minutes. Default 20, from 1 to 500.
- Page after login: My account, Home page, Checkout, Order history or Personal information. Used when the customer did not come from a specific page.
- Keep logs and clicks (days): from 30 to 3,650 days, 365 by default. Logs contain IP addresses and are purged automatically once a day. The dashboard’s daily statistics are kept.
- Outbound webhook: URL and secret, see below.
Appearance tab
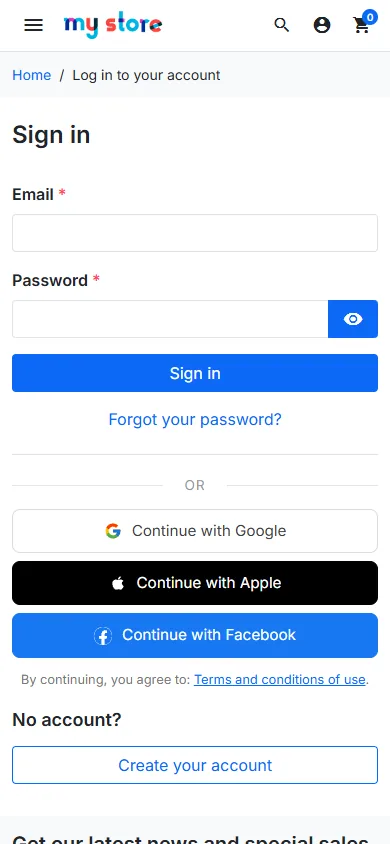
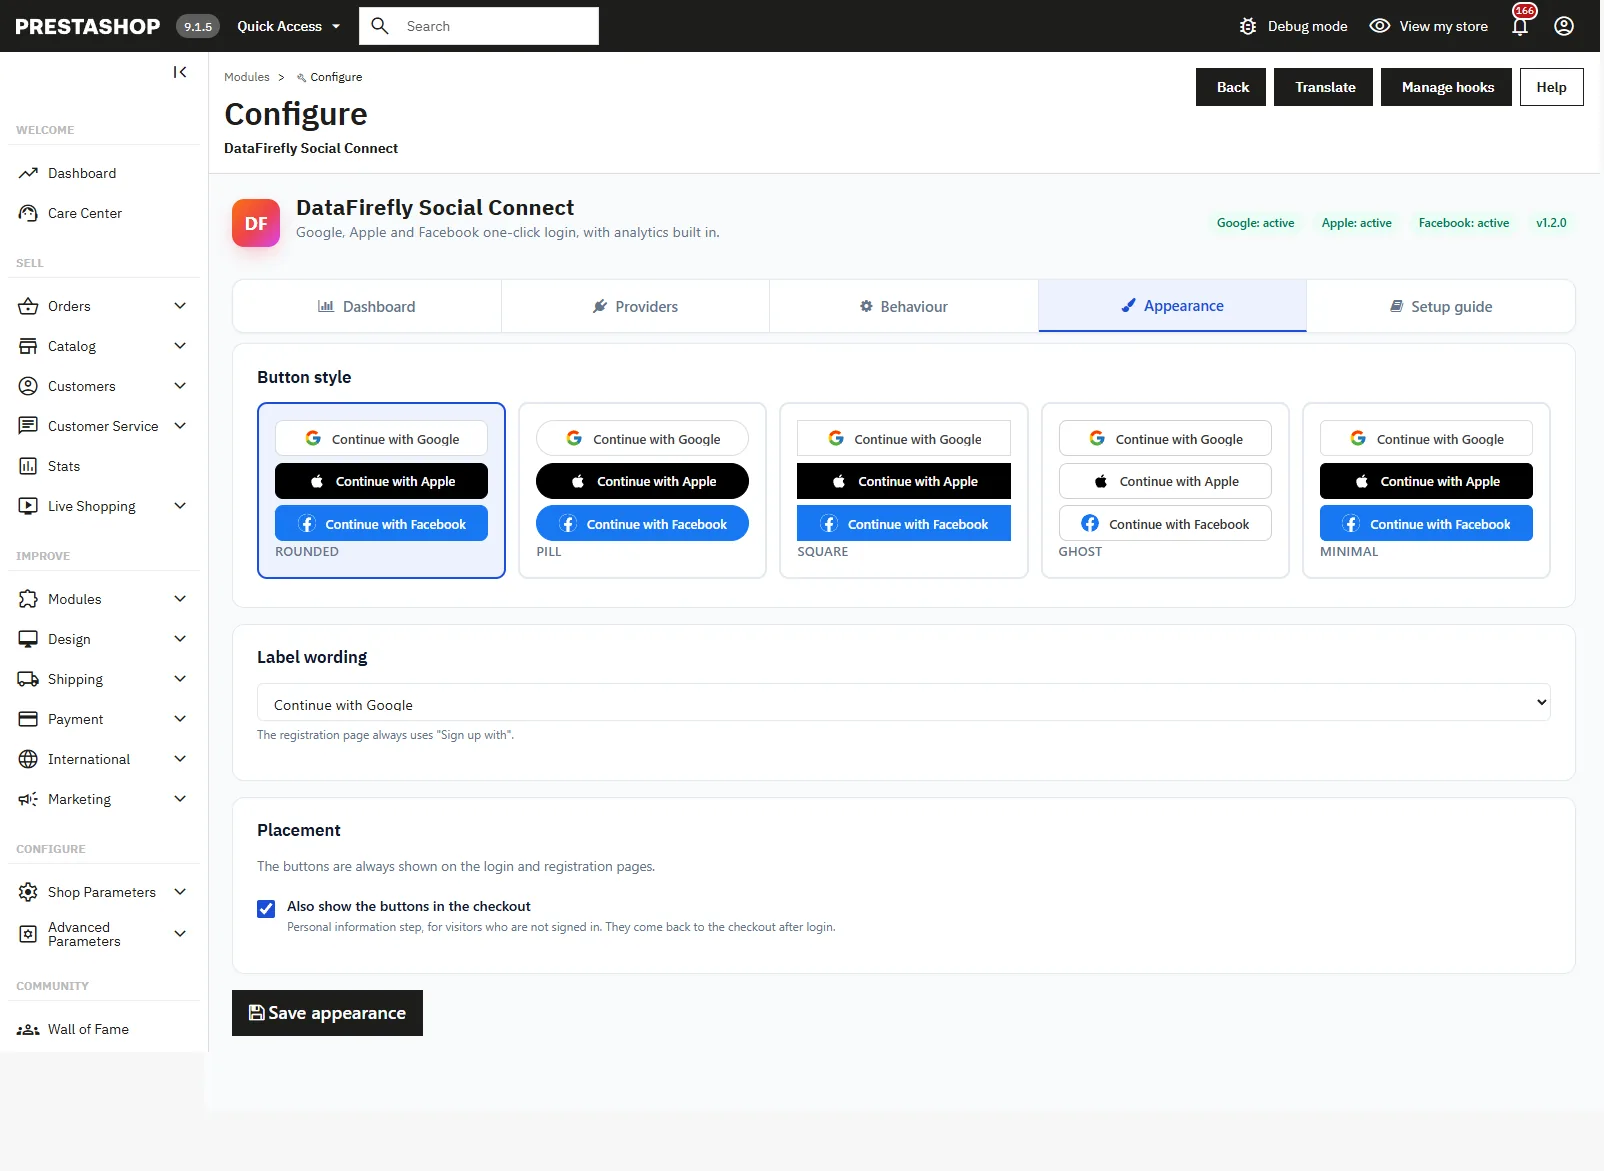
- Button style: rounded (default), pill, square, ghost or minimal. On wide screens the buttons sit side by side, and they wrap to a new line instead of cutting their text.
- Label wording: “Continue with”, “Sign in with” or “Sign up with”. The registration page always uses “Sign up with”.
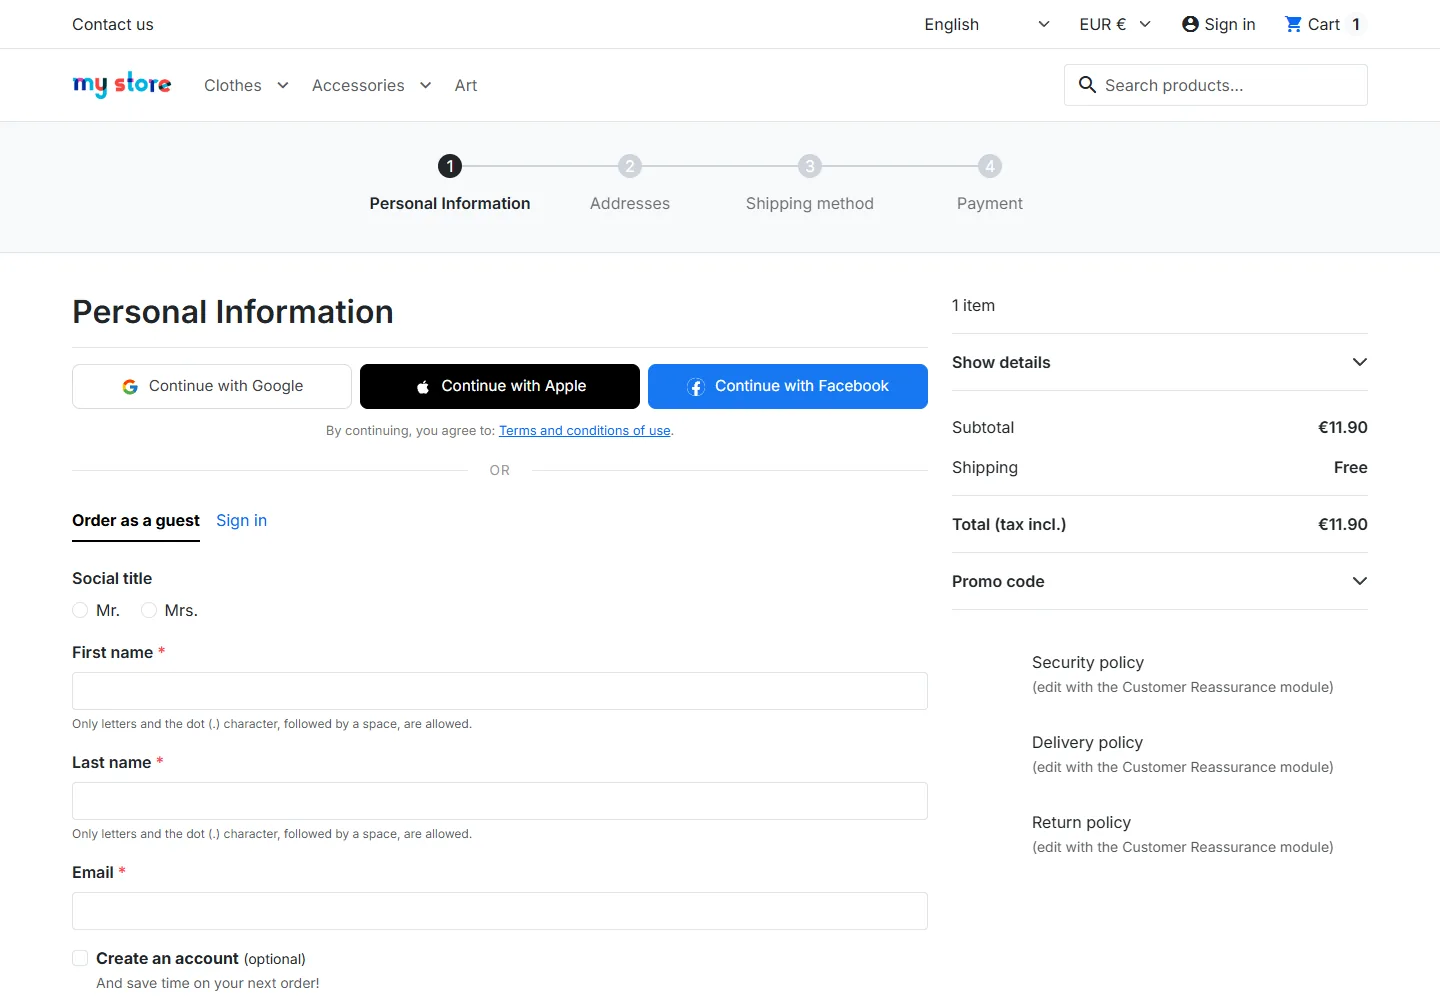
- Also show the buttons in the checkout: “Personal information” step, for visitors who are not signed in. Enabled by default.
The buttons are always shown on the login and registration pages as soon as at least one provider is active.
Dashboard
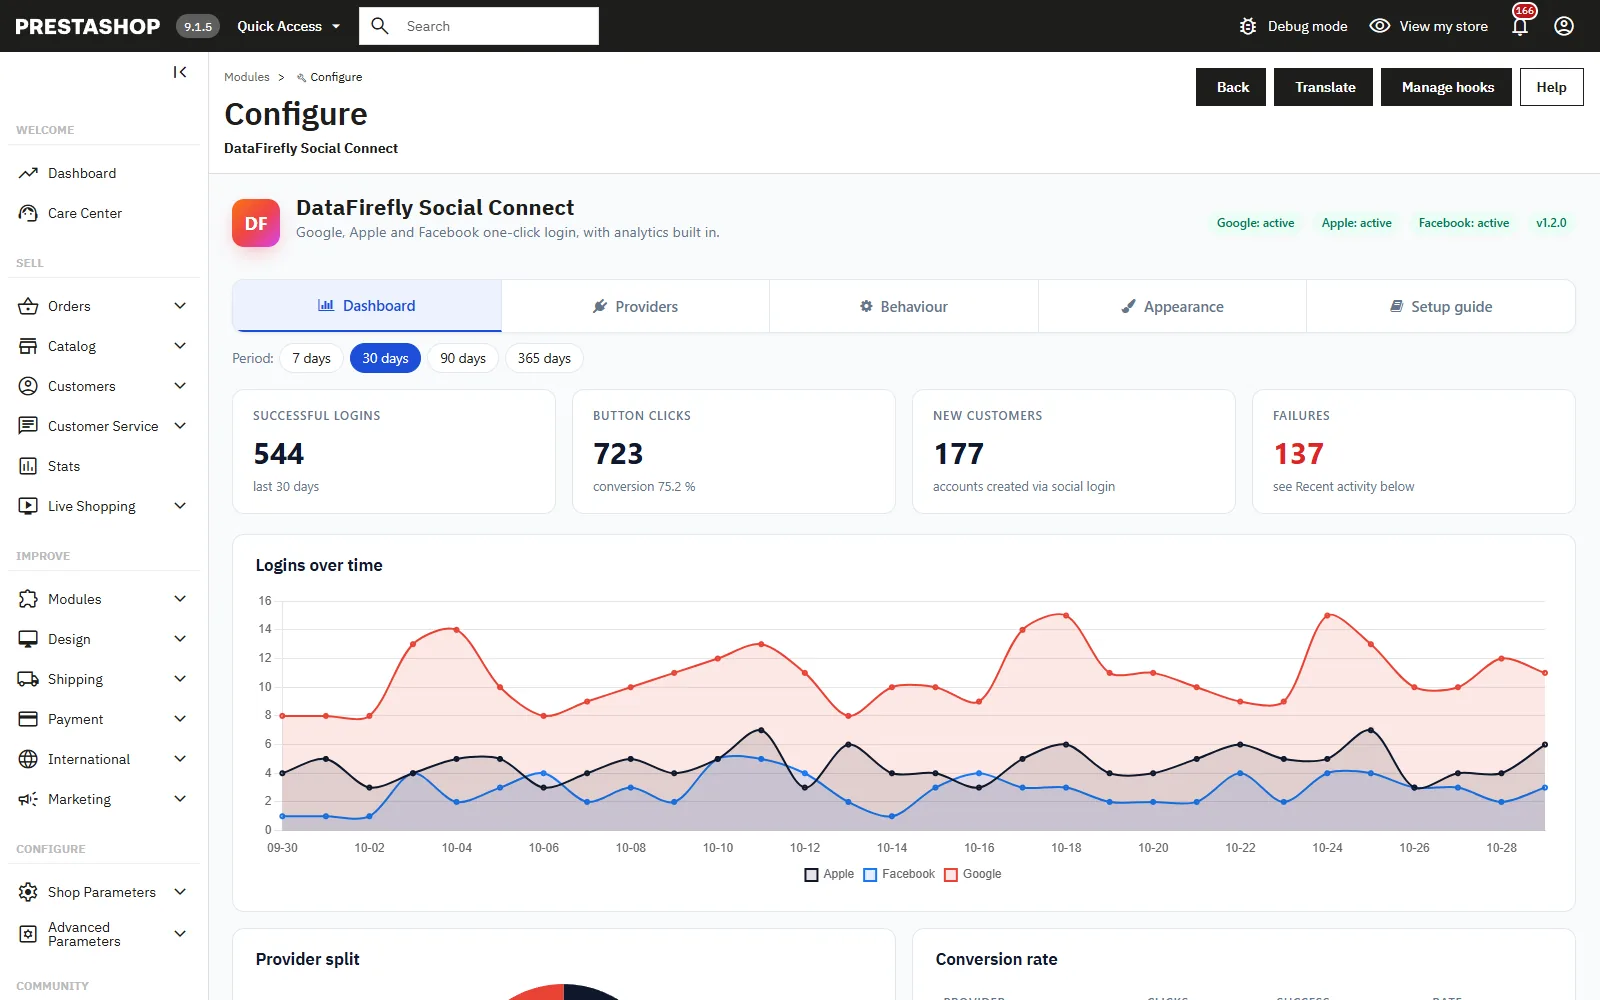
The first tab of the configuration shows statistics over 7, 30, 90 or 365 days. On multistore, it follows the shop or group selected in the back office.
- Indicators: successful logins, button clicks with the conversion rate, new customers, failures.
- Logins over time, day by day and per provider.
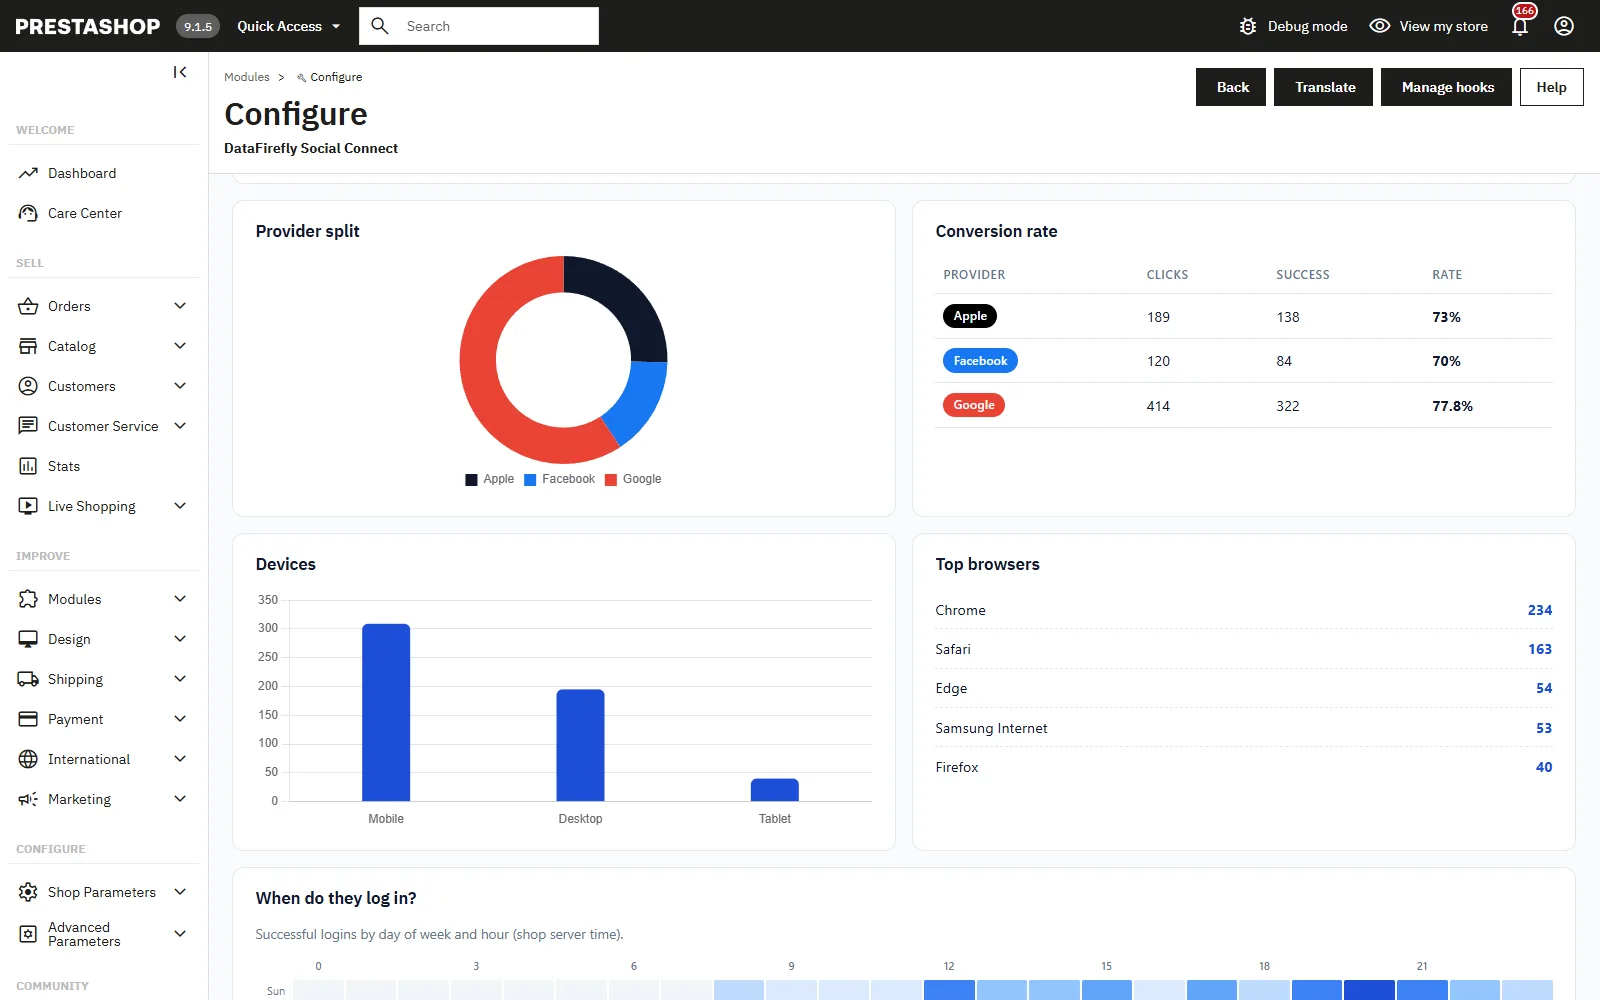
- Provider split and conversion rate per provider: an unusually low rate often points to a misconfigured provider.
- Devices and Top browsers.
- When do they log in?: day x hour map of successful logins (server time).
- Account penetration: share of active customer accounts linked to each provider.
- Revenue from social-login customers: valid orders of the period, tax incl., in each order’s currency. Each customer counts once, under the first provider linked.
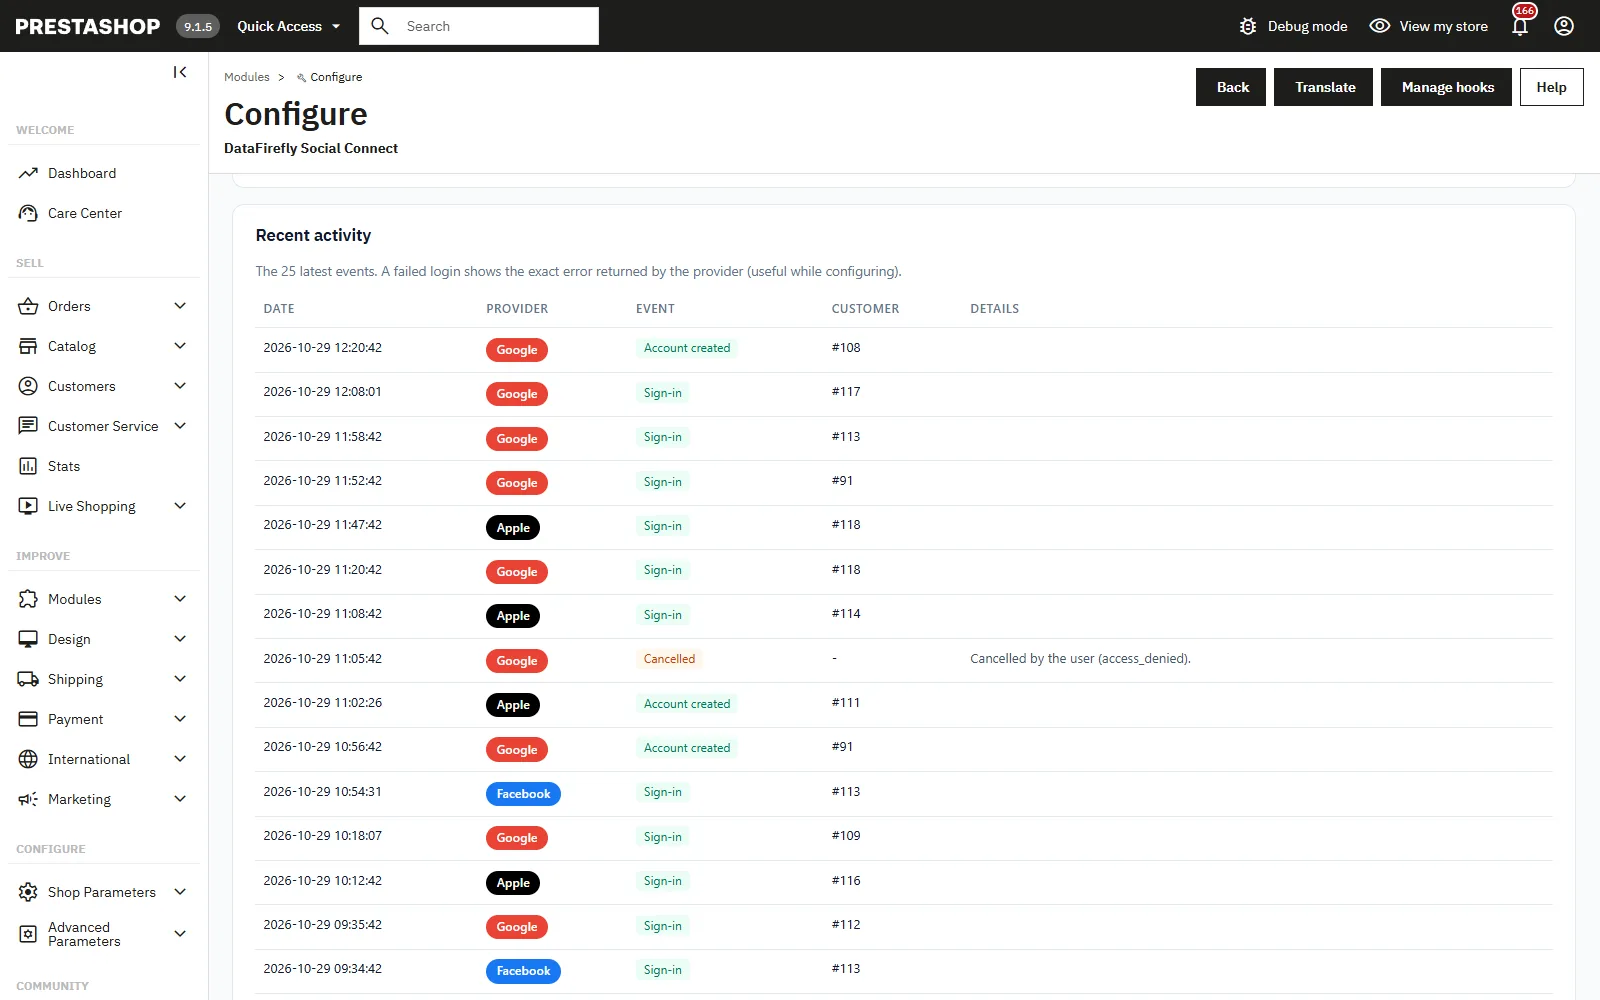
- Recent activity: the 25 latest events (account creations, logins, links, disconnections, failures) with the exact error returned by the provider.
CRM webhook
The module can send a JSON POST to the URL of your choice on the events identity.login (login or account creation), identity.linked (link from Connected accounts) and identity.unlinked (disconnection). The call is capped at 3 seconds so it does not slow the customer down. If it fails, the error is written to the PrestaShop logs.
The body is signed with HMAC-SHA256 using the webhook secret. A random secret is generated at installation. The signature is sent in the X-Dfsc-Signature header as sha256=<hex> and the event name in X-Dfsc-Event. On the receiving side, recompute the HMAC over the raw body and compare.
{
  "event": "identity.login",
  "sent_at": "2026-10-14T11:27:45+02:00",
  "data": {
    "id_customer": 1234,
    "provider": "google",
    "event": "created",
    "email": "marie.dupont@example.com",
    "id_shop": 1
  }
}
The data.event field is created (account created), linked (attached to an existing account through a verified email) or login (login of an already linked customer).
GDPR
- The legal notice under the buttons informs the customer before the account is created. The acceptance is recorded in
ps_dfsc_consent, together with the newsletter subscription status. - Logs and clicks, which contain IP addresses, are purged after the chosen retention period.
- The customer can disconnect each provider from the Connected accounts page.
- With the official psgdpr module, the customer’s data export includes their linked accounts, and deleting their data erases their links, consents and avatars.
- When a customer is deleted in the back office, including with the “do not allow registration” option, their links, consents and avatars are deleted and their log lines are anonymised.
Languages
The module ships in English, French, Spanish, German, Italian, Dutch, Polish and Portuguese, on both the shop and the back office. Texts can be edited in International > Translations > Installed modules translations.
Uninstall
From the Module Manager, uninstalling removes the 5 ps_dfsc_* tables, its DFSC_* configuration keys (those of DF Simple Checkout, which uses the same prefix, are left untouched) and the /img/dfsc/ folder of imported avatars. Customer accounts and their orders stay intact: only the social links are erased.
Troubleshooting
Always start with the Recent activity list on the dashboard: it shows the exact error returned by the provider.
redirect_uri_mismatch (Google) or blocked URL (Facebook): the URI registered at the provider does not exactly match the one shown by the module. Check https, www, the language prefix and the ?provider= parameter.
invalid_client (Apple): wrong Team ID or Key ID, incomplete .p8 key, Services ID confused with an App ID, or a Return URL different from the module’s. If the module says “The saved key cannot be read: paste it again.”, paste the key again.
invalid_grant: the authorization code has expired or was already used, for example after pressing the browser’s back button. Simply start the login again.
“Your sign-in session has expired. Please try again.”: more than 15 minutes passed on the provider’s screen, or the shop cookie was blocked. Start the login again.
“An account already exists with this email address”: the provider did not confirm the email (always the case for Facebook unless the “Also trust Facebook emails for auto-link” option is on), or auto-linking is off. The customer signs in with their password and then connects the provider from Connected accounts.
“Too many attempts. Please wait a few minutes.”: the per-IP limit has been reached. Wait 15 minutes or raise the threshold in Behaviour, for example for a company whose workstations all share the same IP.
A button does not appear: check in the configuration banner that the provider is “active” and not “incomplete”. Then clear the PrestaShop cache.
The welcome voucher is not created: check that the option is enabled and that the amount is greater than zero. The voucher is only created for a new account, not when an existing account is linked.