PrestaShop Administration & Productivity

PrestaShop Admin Security 8 & 9: Brute Force Protection, IP Blocking and Captcha

The PrestaShop back office closed to bots: limited attempts, filtered IPs and countries, a login page invisible without a secret link, and an alert as soon as a login looks unusual.

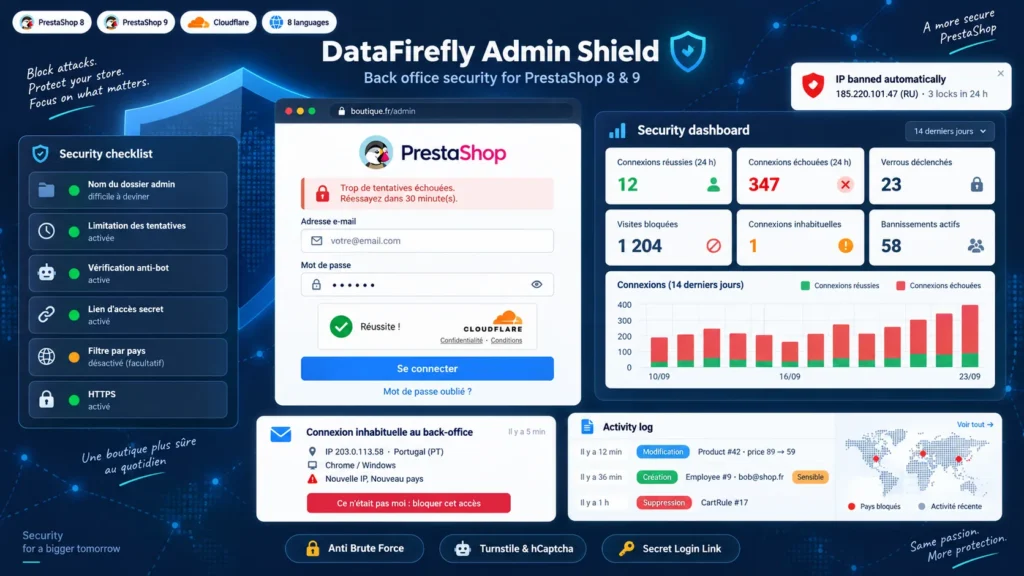
The back office login page is the most attacked door of a PrestaShop shop. Bots try thousands of passwords there, from countries where you have no staff. This module limits attempts per account and per IP, bans addresses that keep trying, filters countries, adds Cloudflare Turnstile or hCaptcha to the form and can make the back office completely invisible without a secret link. Every unusual login sends an e-mail with a button to block the access, and a log records what each employee creates, modifies or deletes.

At a glance
  • Login attempt limiting per account and per IP, progressive lock and automatic ban
  • Blocking by IP, CIDR range and country, whitelist and strict whitelist-only mode
  • Secret access link: without it, the back office answers with a 404 page
  • Cloudflare Turnstile or hCaptcha on the login and forgotten password forms
  • Unusual login alerts, active sessions, activity log and weekly report
PrestaShop 8 & 9 Brute force protection Turnstile & hCaptcha Audit log
  • 30-day refund
  • 12 months updates
  • 24h support
www.datafirefly.com/en/
PrestaShop Admin Security 8 & 9: Brute Force Protection, IP Blocking and Captcha
v1.3.0 · updated 2026-09-23
What it does

The short version.

01

Bots stop at the door

After 5 failures on one account or 15 from the same IP, the login is locked. The duration doubles at each repeat, and an IP locked three times in 24 hours is banned. The lock applies to the IP and account pair, so an attacker cannot lock out the real administrator.

02

A back office that does not exist for anyone else

With the secret access link, only browsers that opened it once can see the login page. Everyone else gets a 404 page. The country filter and the strict whitelist mode complete the setup for teams with fixed IP addresses.

03

An alert when something is off

New IP, new country, new device or a login outside usual hours: the employee and the super administrators get an e-mail, and the message can also go to Slack, Teams or Discord. The It was not me button bans the IP, closes the sessions and invalidates the password.

04

Who changed what, and when

The activity log records every creation, modification and deletion made in the back office, with the old and new value of each field. Creating an employee, changing a profile, an API key or installing a module triggers an immediate alert.

The long version

Everything you'd want to know before you install.

A detailed look at how PrestaShop Admin Security 8 & 9: Brute Force Protection, IP Blocking and Captcha works, why we built it the way we did, and the thinking behind the features above.

§ 01

Why a renamed admin folder is no longer enough

PrestaShop renames the admin folder at installation, but the name leaks: links in e-mails, browser extensions, modules that display it. Once the address is known, nothing stops a bot from trying passwords forever. This module adds what the core lacks: a cap on attempts, bans, geographic filtering and, if you want it, a secret link without which the login page does not exist.

§ 02

Protection built for both PrestaShop 8 and PrestaShop 9

PrestaShop 9 replaced the old login controller with Symfony Security. The module plugs into both: a Symfony subscriber filters every back office request before routing and intercepts the PrestaShop 9 login form before the firewall; on PrestaShop 8 it also relies on the native hooks of the login controller. No core file is modified and no override is installed.

§ 03

A captcha that cannot lock you out

One badly copied captcha key is enough to block every administrator. Here, the check is only enforced after a successful test from the back office with the exact keys saved. If the Cloudflare or hCaptcha service cannot be reached, you decide whether logins go through. The same logic applies elsewhere: the module refuses to save a country filter, a blacklist or a whitelist-only mode that would block your own connection, and a single file uploaded by FTP switches every protection off in an emergency.

§ 04

Know who is logged in and what they do

The Active sessions tab lists every open session with the IP, country and device used at login; you close a session or log an employee out everywhere. For every object modified in the back office, the activity log keeps the list of changed fields with their old and new values, passwords and tokens masked. PrestaShop skips a module's hooks for profiles not allowed to view it, so the module grants that right to every profile to make sure each employee is logged.

§ 05

A report that arrives without asking

Every week or every month, the administrators receive a report: successful and failed logins, locks, bans, blocked visits, unusual logins, sensitive changes and the IP addresses most active on the login page, with the security points still to fix. A signed cron URL guarantees delivery; without cron, the report leaves on the next back office visit.