
Login as Customer Pro: Documentation
Open a support session on a customer account from the PrestaShop 1.7.8, 8 and 9 back office: single-use link, banner, read-only mode, log.
Overview
Login as Customer Pro (module dfconnectas) opens a support session on a customer account from the back office: you see the shop exactly as the customer does, to reproduce an issue or help them order. Each session uses a single-use link valid for a few seconds, shows a permanent banner with the time left, ends by itself and stays in a log nobody can edit.
Compatibility
- PrestaShop: 1.7.8, 8.x and 9.x (tested on 1.7.8.11, 8.2.1 and 9.1.5).
- PHP: as supported by your PrestaShop version (tested on PHP 7.4, 8.1 and 8.5).
- Themes: Classic and Hummingbird.
- No override, no Composer dependency. 8 languages: English, French, Spanish, German, Italian, Polish, Dutch, Portuguese.
PrestaShop 1.7.0 to 1.7.7 is no longer supported since version 2.0.0: stay on 1.1.0 on those versions.
Installation and upgrade
- Install the ZIP from Modules › Module Manager (or
php bin/console prestashop:module install dfconnectas). - Two entries appear under Customers: Connect as customer (customer list with button) and Connection log.
- Open Modules › Connect As Customer › Configure to check the settings. By default, only SuperAdmin employees can connect as a customer.
Upgrading from 1.0.0 or 1.1.0 keeps the log and the settings. The link lifetime is capped at 60 seconds, open 1.x links are cancelled, the banner can no longer be turned off, and the empty profile list of 1.x (every profile with the module tab) becomes the explicit list of those profiles.
Opening a support session
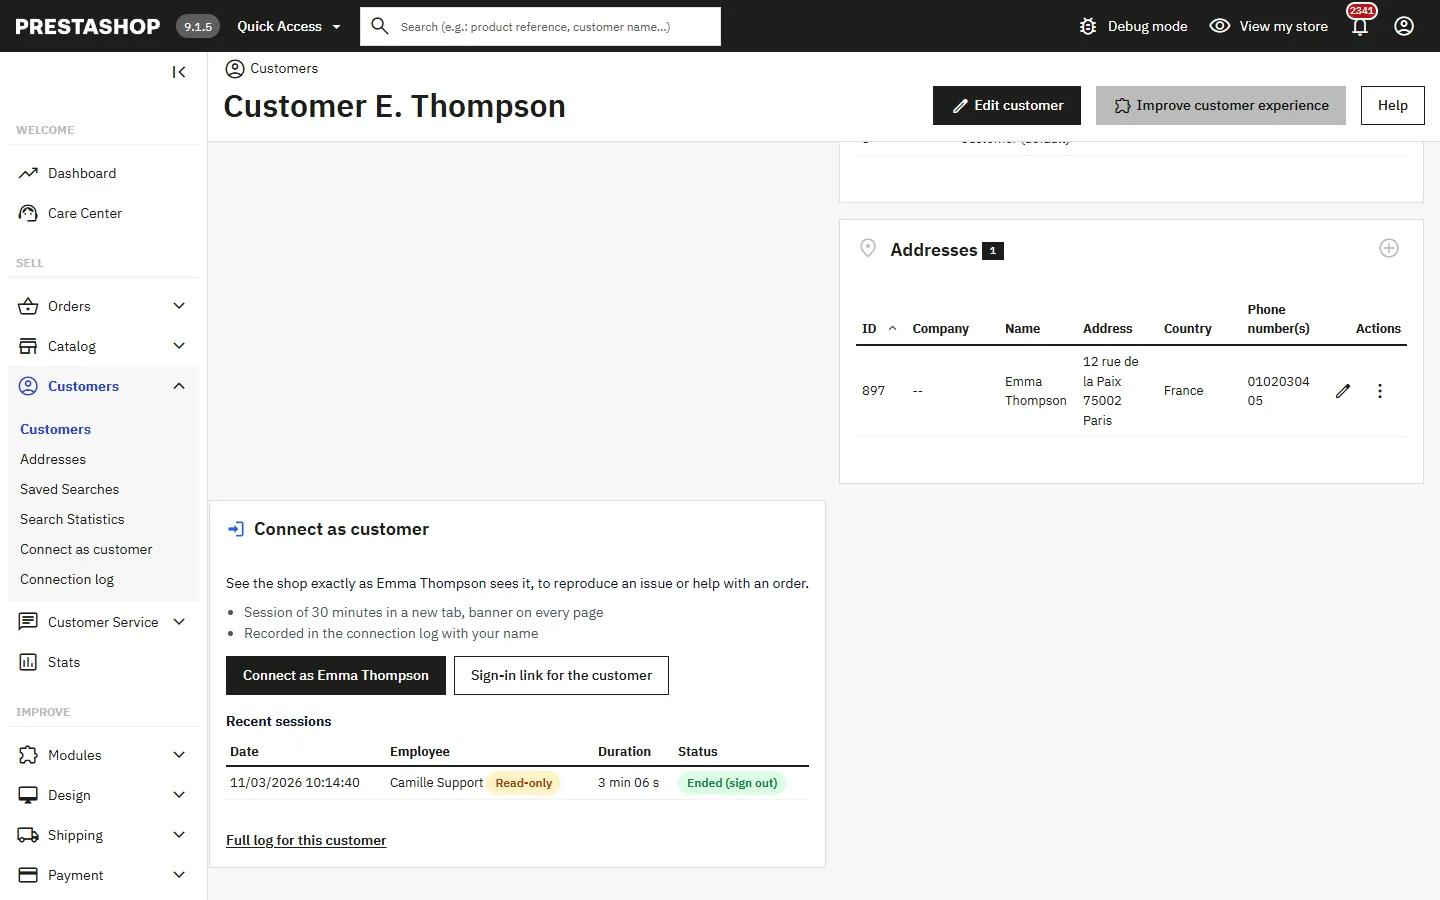
On the customer page, the Connect as customer panel shows the session length and the last sessions on this account.
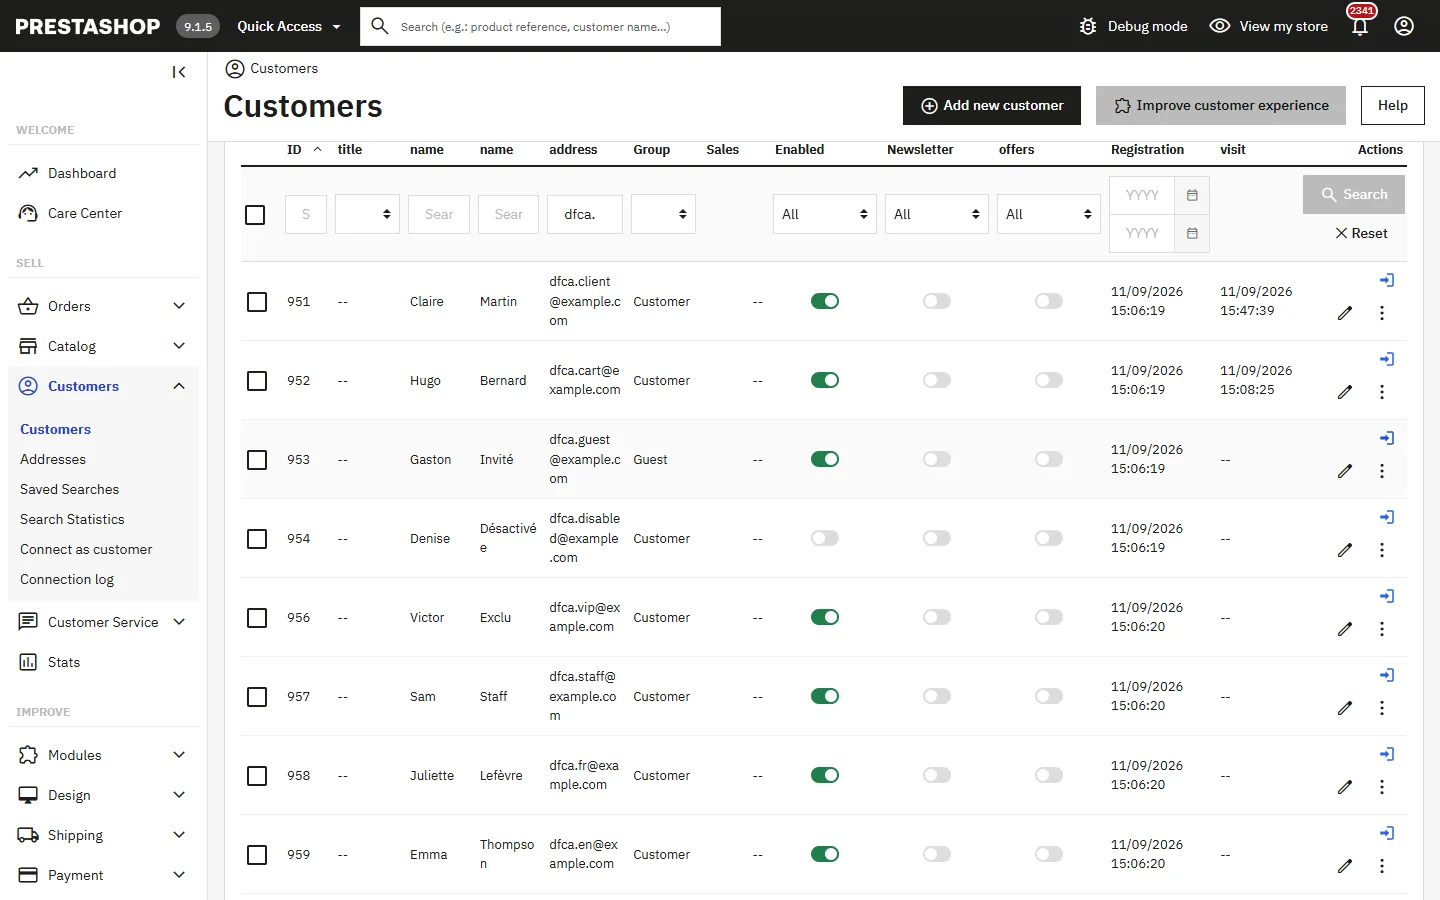
In Customers › Customers, an icon is added to each row (can be turned off). The order page also offers the button next to the customer.
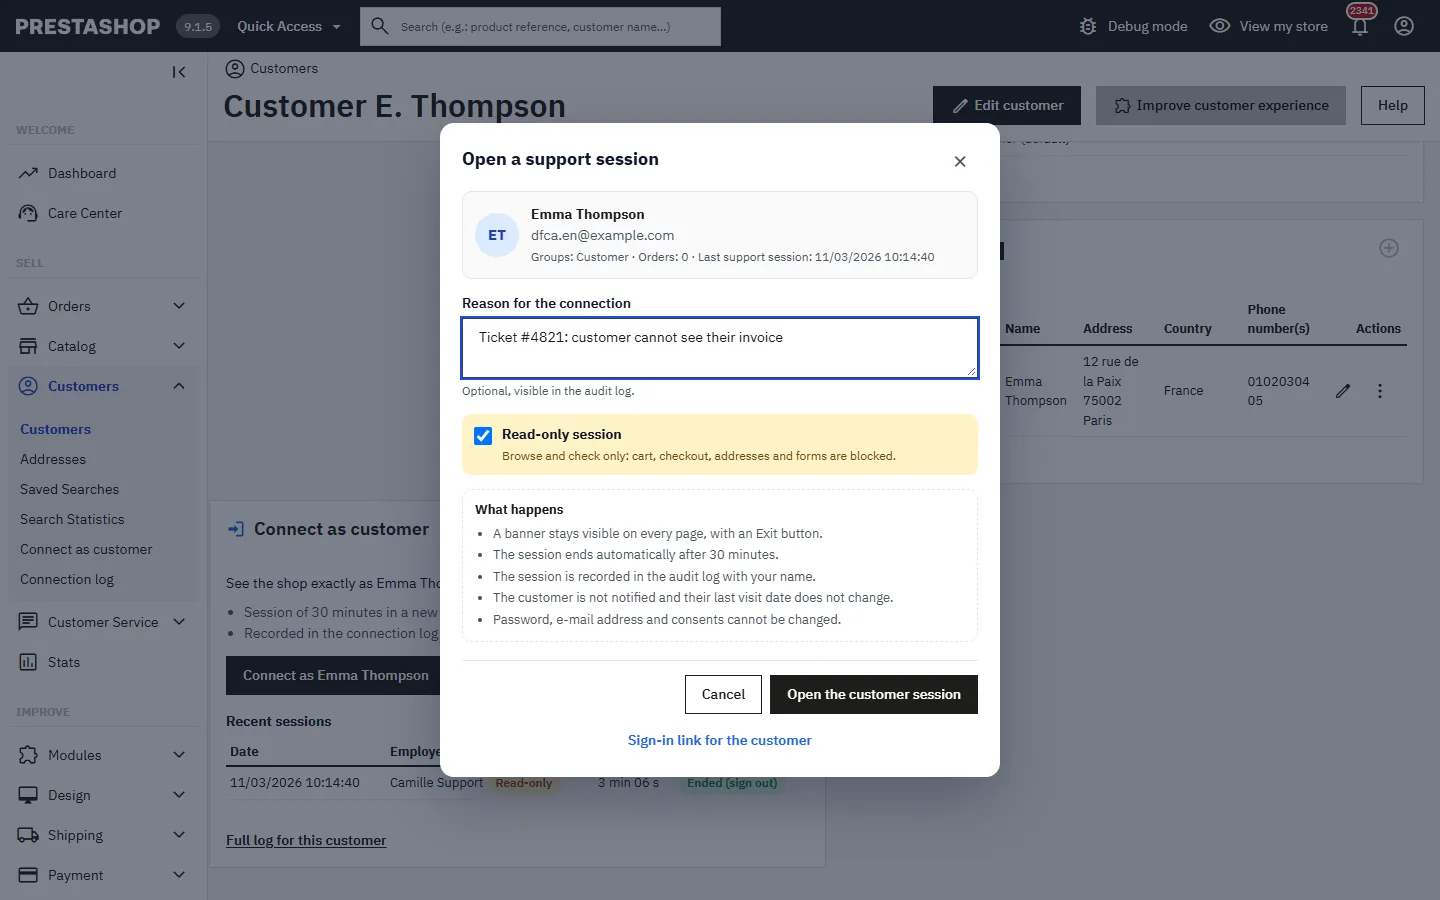
The button opens a confirmation dialog: account, reason (optional or required depending on the settings, shown in the log), Read-only session ticked by default, and what will happen. The shop opens in a new tab; the link never goes through the address bar.
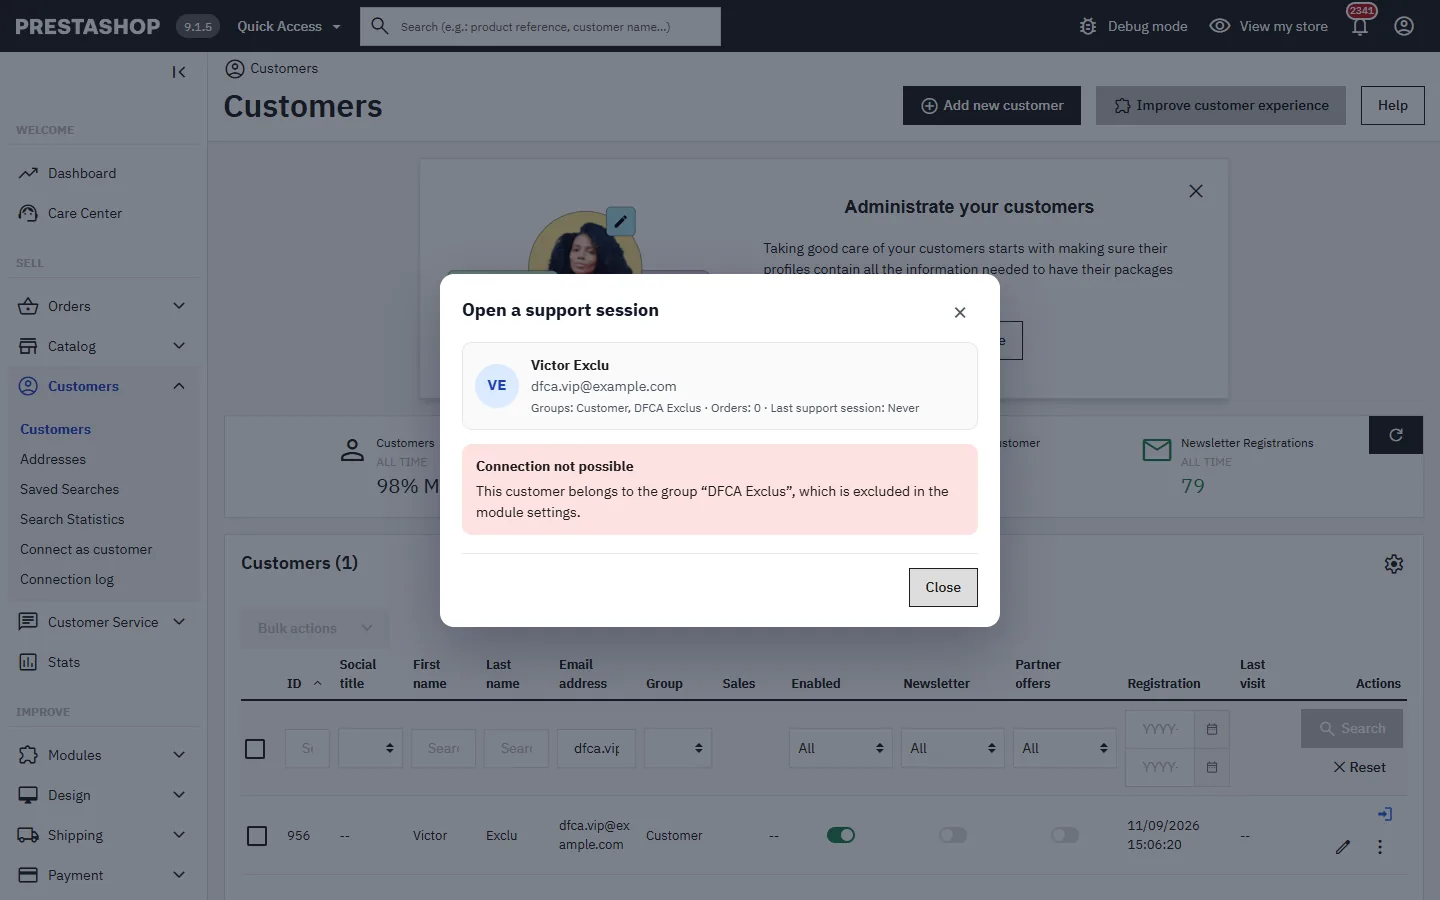
When connecting is not possible, the dialog says why and what to do: account in an excluded group, disabled account (for example waiting for validation), deleted account, e-mail address used by an employee, profile not allowed, shop not accessible, employee two-step verification pending.
During the session
A banner stays on every page: customer, employee, read-only, time left and an Exit button. It can be reduced, not turned off.
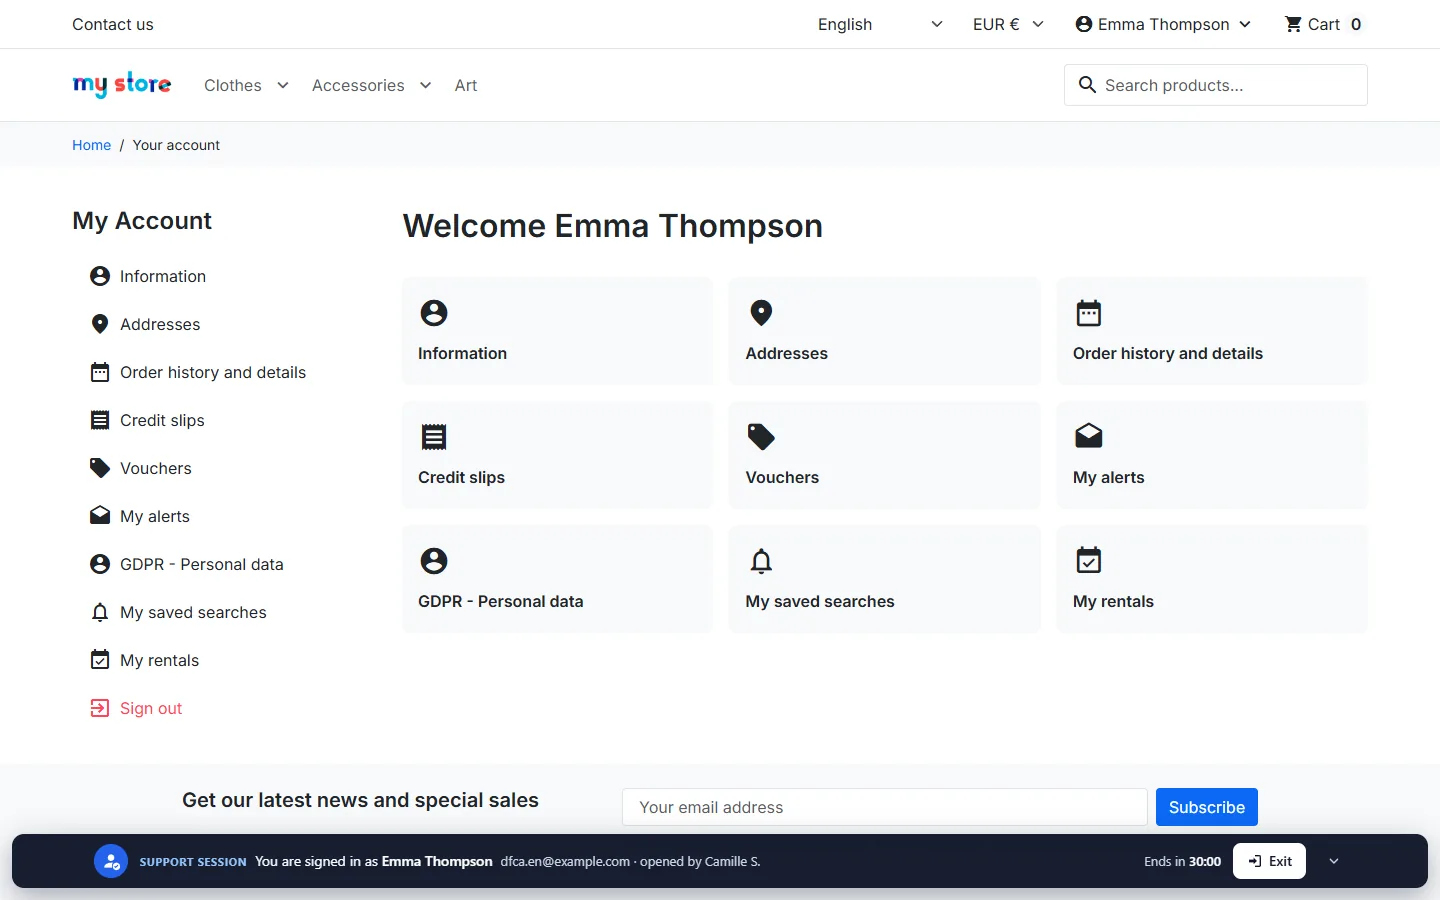
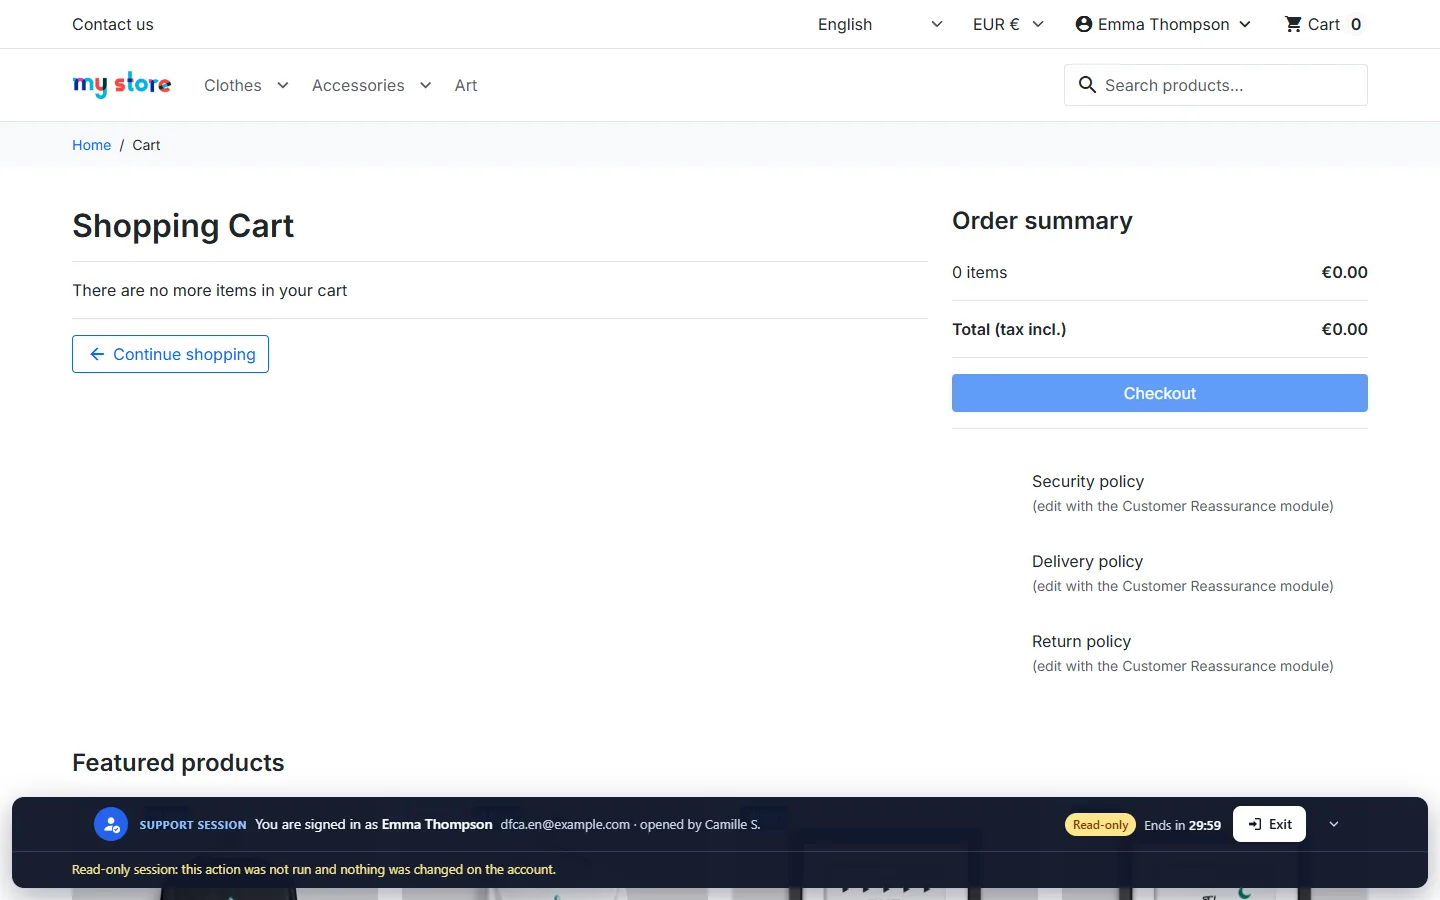
In read-only mode, the cart, checkout, addresses, messages and forms are blocked; the banner explains that nothing was changed. In every session, the password, e-mail address, personal data and consents (Identity page, GDPR module) are protected, unless you allow it.
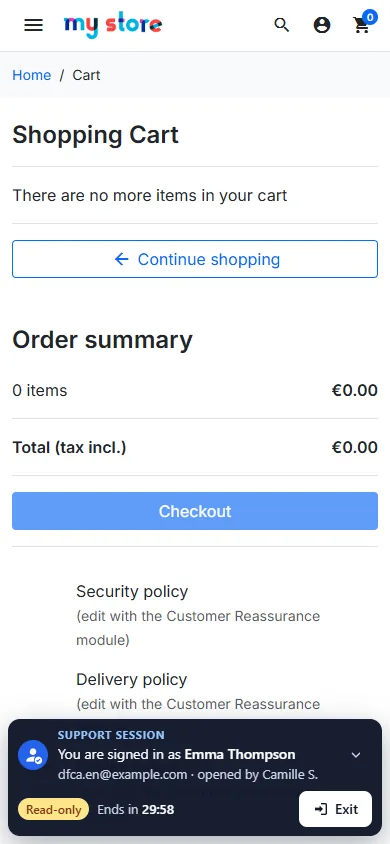
On mobile, the banner folds into two lines and keeps the Exit button visible.
- Separate cart (default): your browser cart is never merged into the account, and a cart created during the session without an order is deleted at the end.
- The customer is not notified, their last visit date does not change and their own sessions on their devices are not touched.
- Analytics: the module adds the
dfconnectas_impersonationevent to the dataLayer and sets Google consent to “denied” before your tags. Exclude this event in your tag manager: other trackers are not stopped.
End of the session
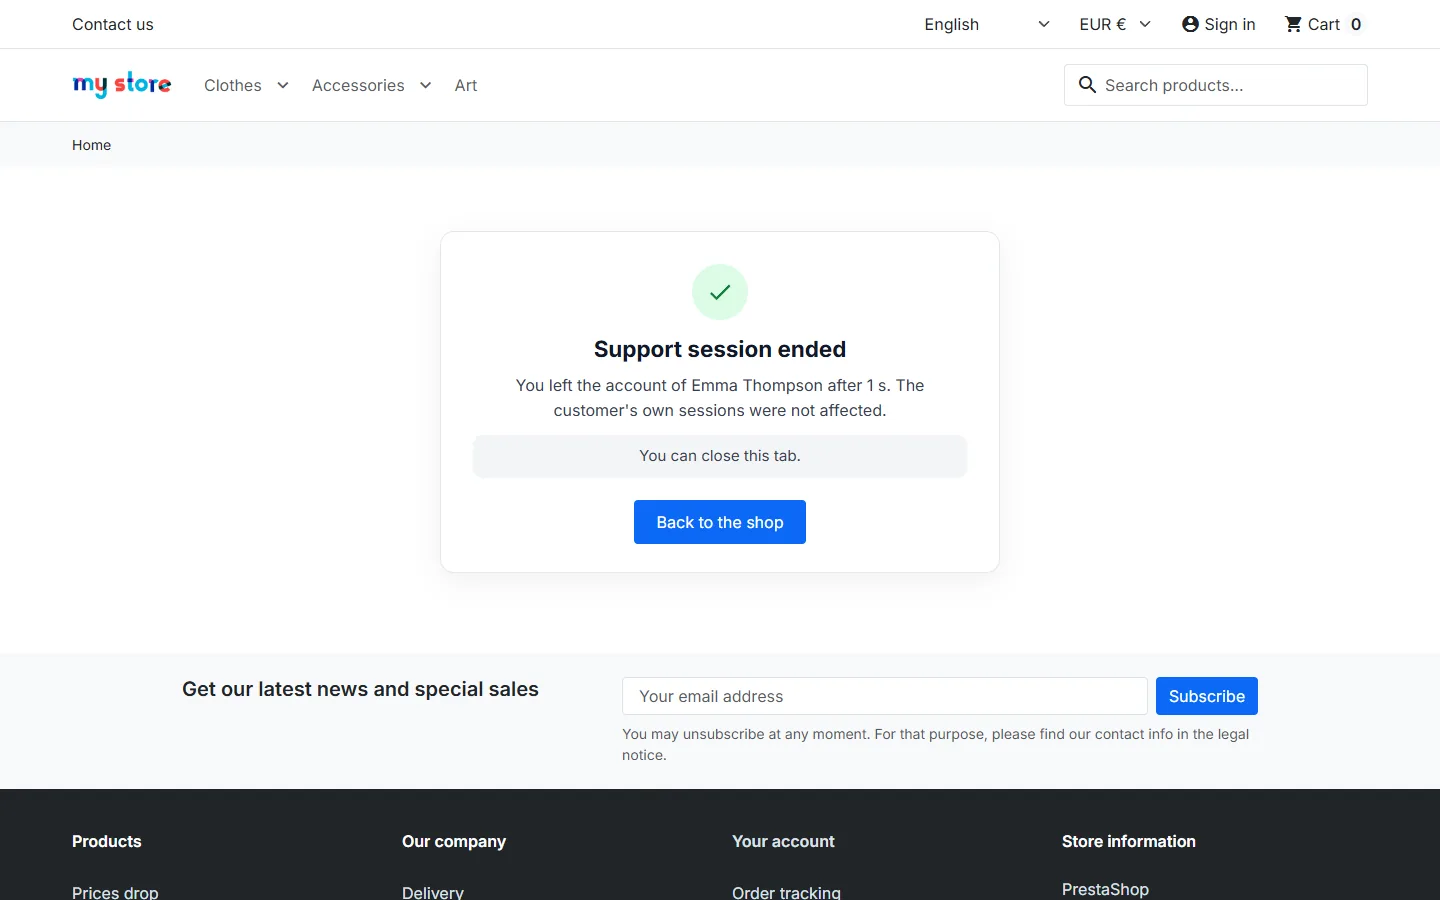
The session ends with the Exit button, at the end of the configured length (30 minutes by default), with the customer’s “Sign out” link, or within a minute if the employee signs out of the back office, is disabled or loses the permission. The browser gets a visitor session back, with its previous cart.
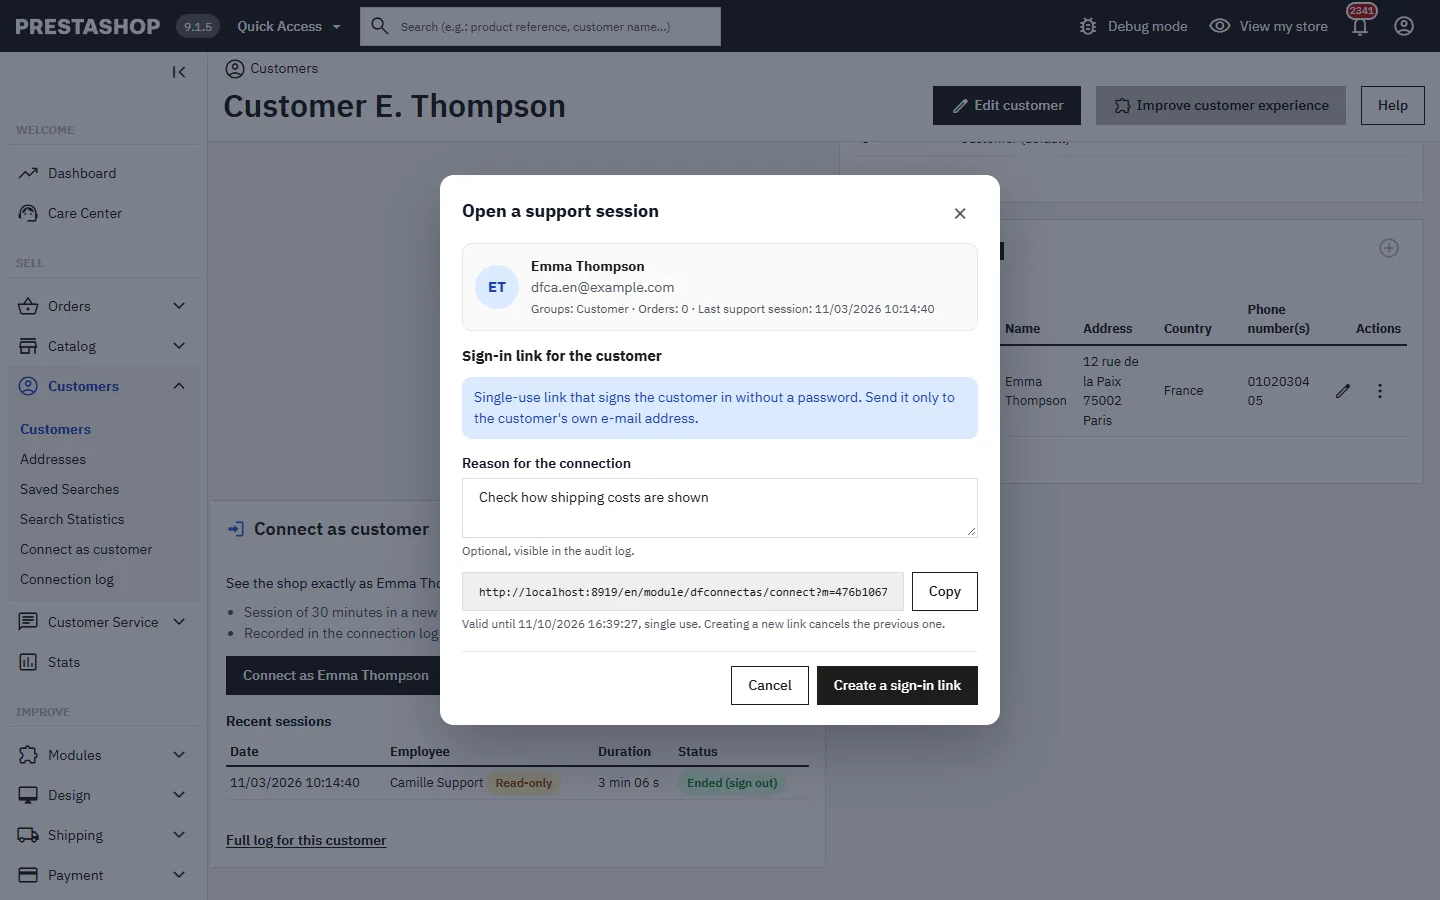
Sign-in link for the customer
Option (off by default) to help a customer who can no longer sign in: a single-use link valid for 1 to 72 hours that signs them in without a password. It is shown once to the employee and never sent by the module; a new link cancels the previous one. The customer confirms with a button, so mail scanners that open links do not use it up.
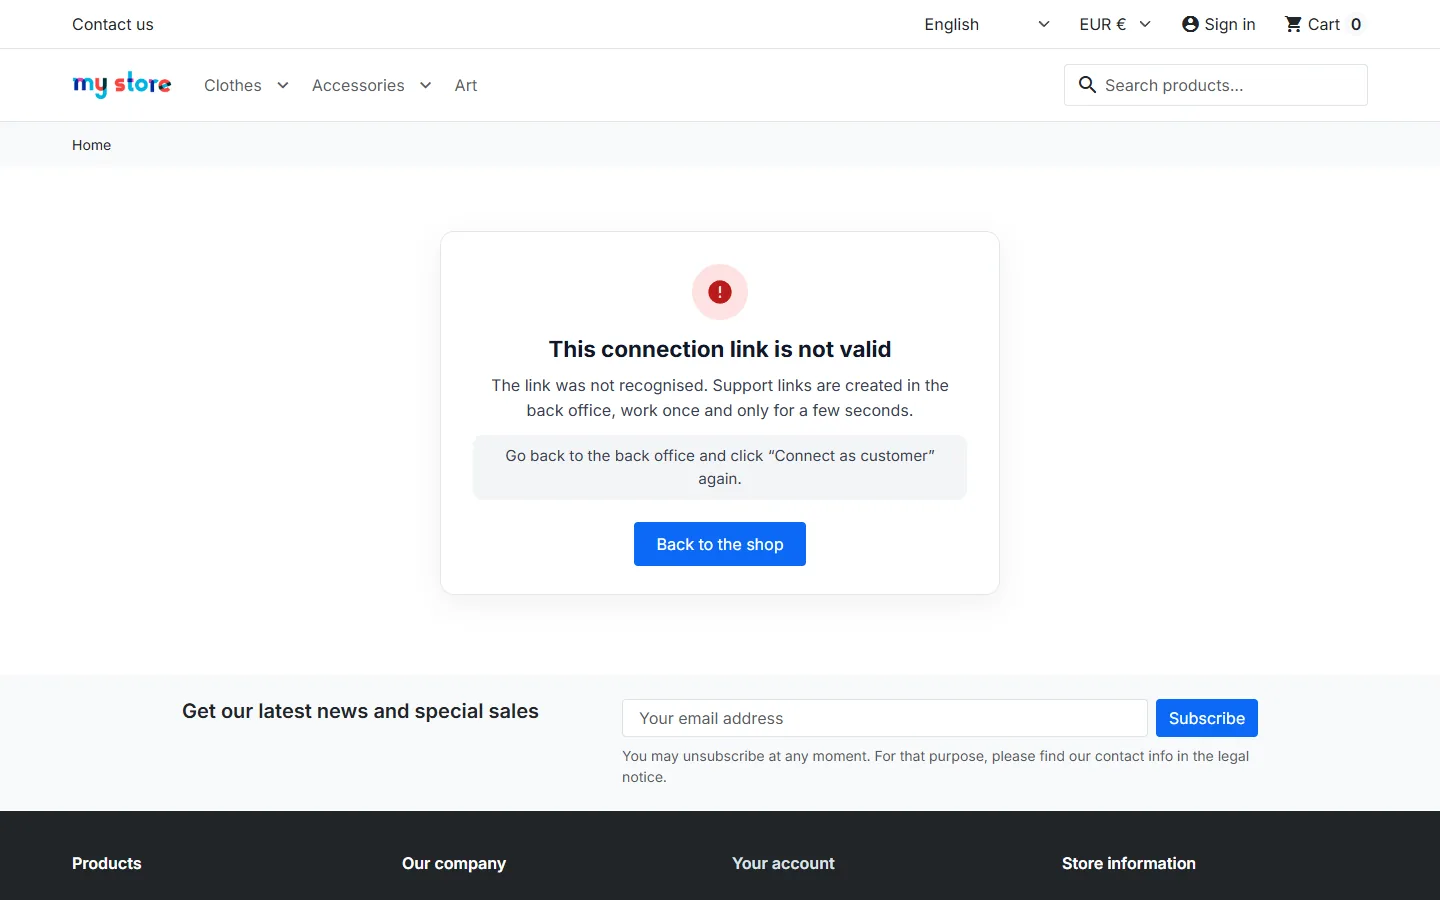
Error pages
Link not valid, already used, expired, opened from another network or another shop, access refused, too many attempts: each case has a clear page with what to do next.
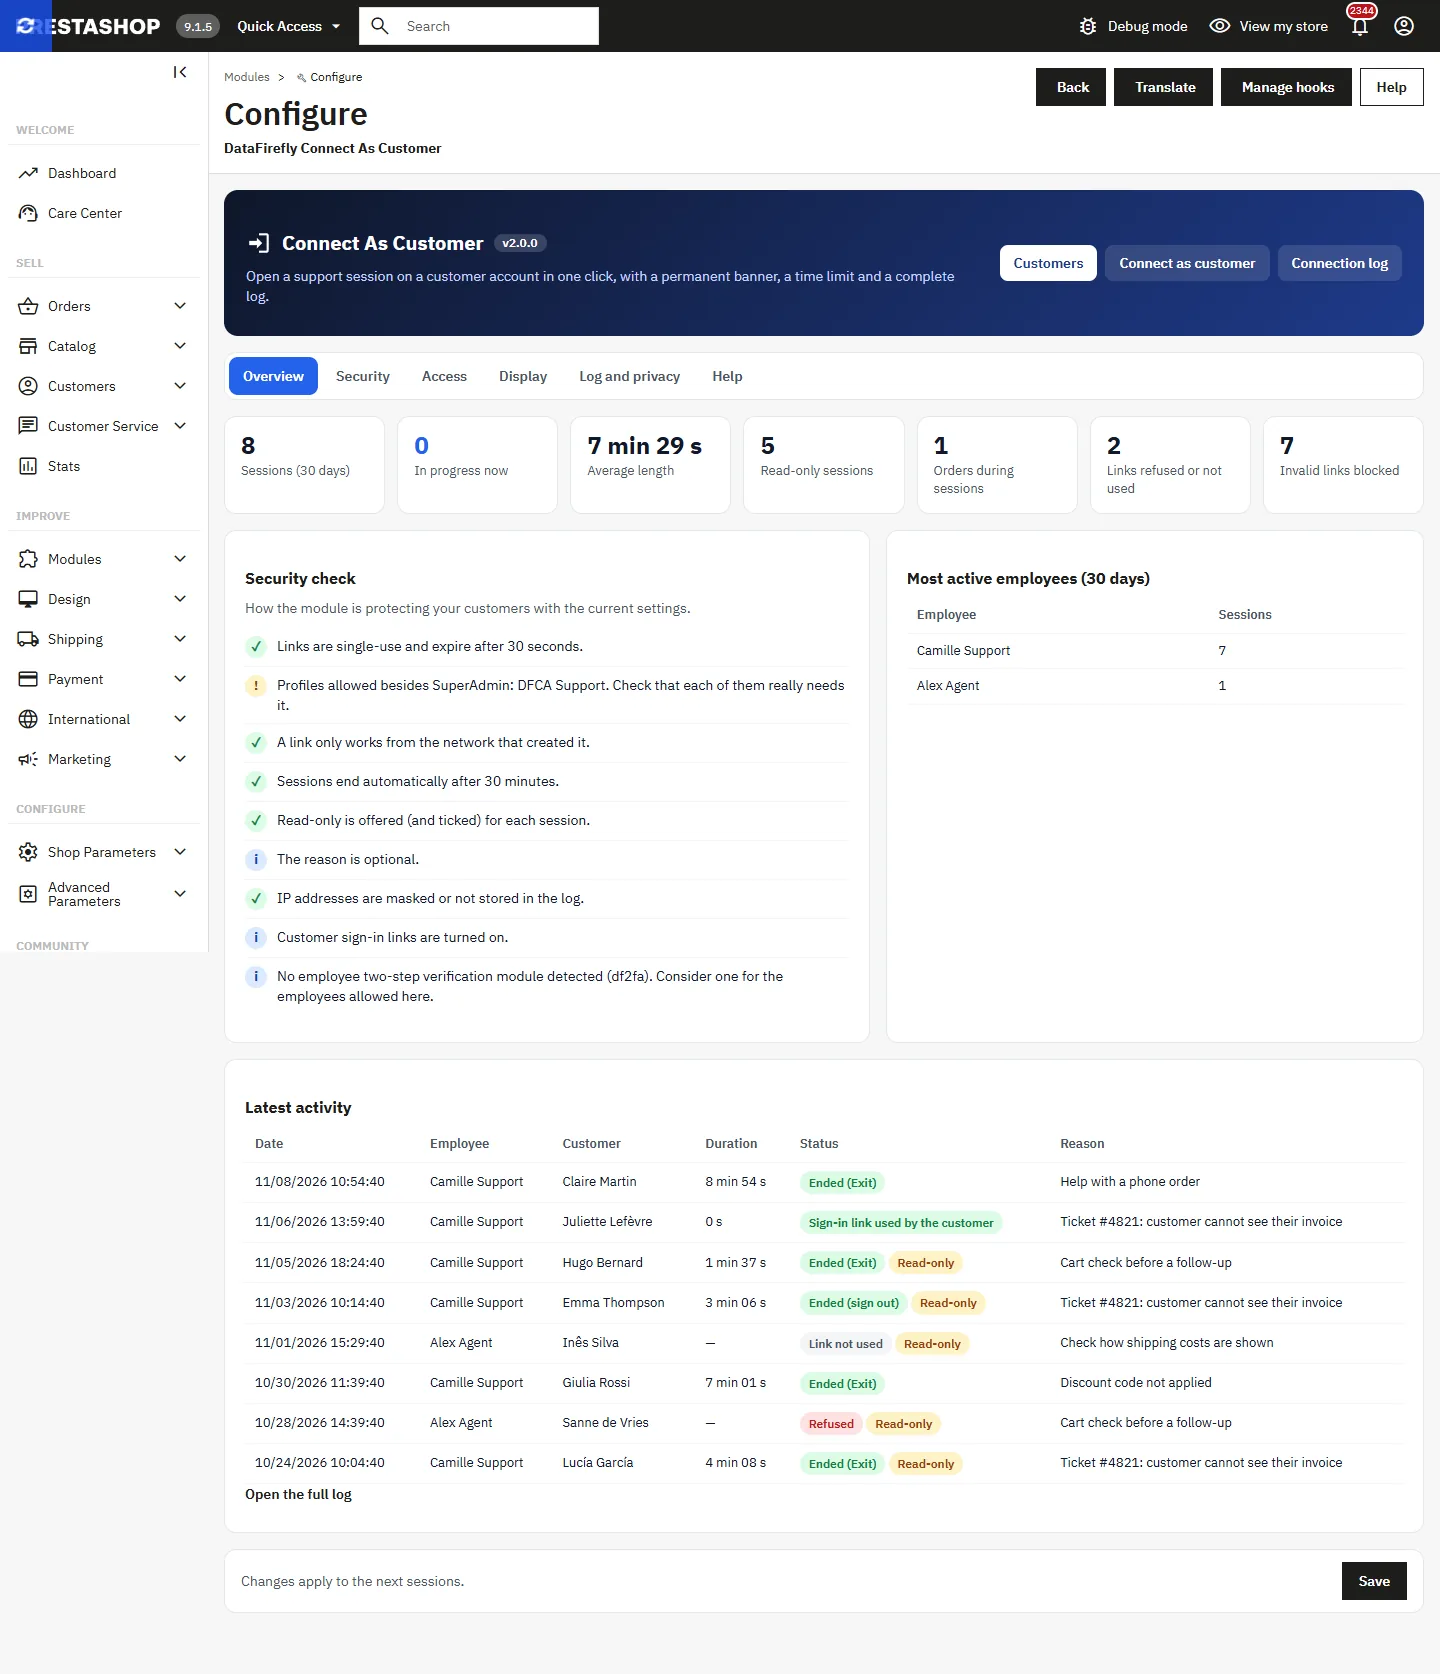
Settings
The overview sums up the activity over 30 days and a security check of your settings.
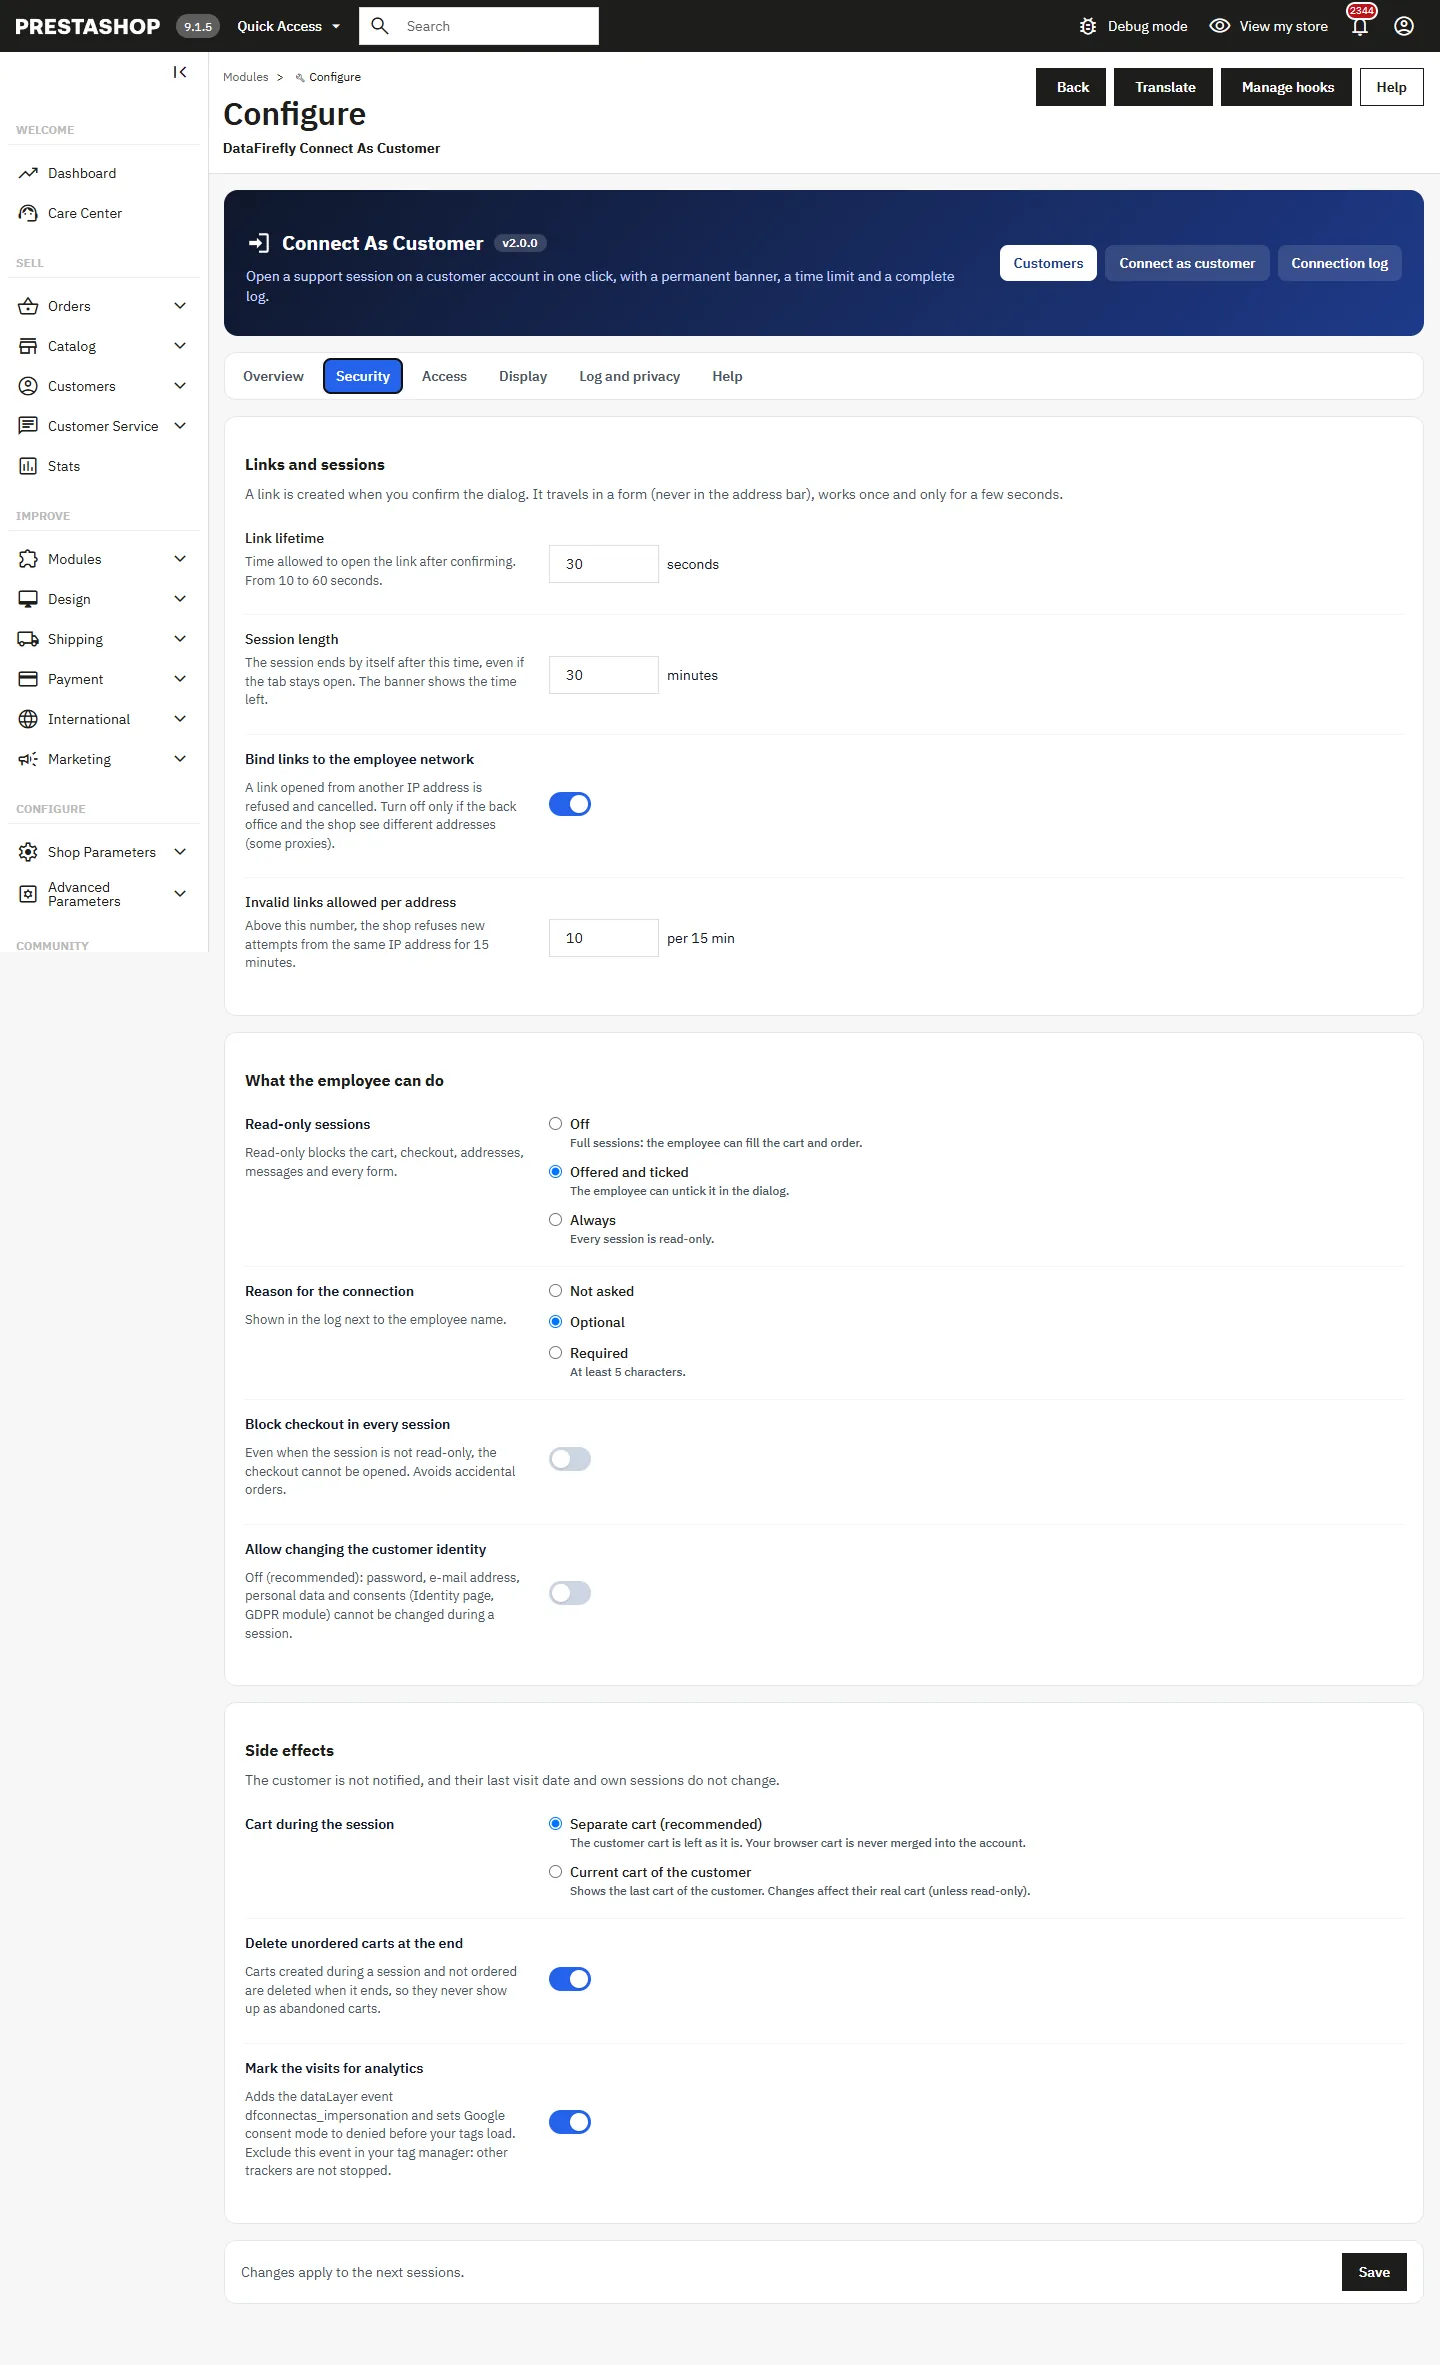
The Security tab sets the link lifetime (10 to 60 seconds), the session length (5 to 480 minutes), binding to the employee’s network, the number of invalid links tolerated, read-only, the reason, checkout blocking, identity protection, the cart and the analytics mark. Each setting is explained.
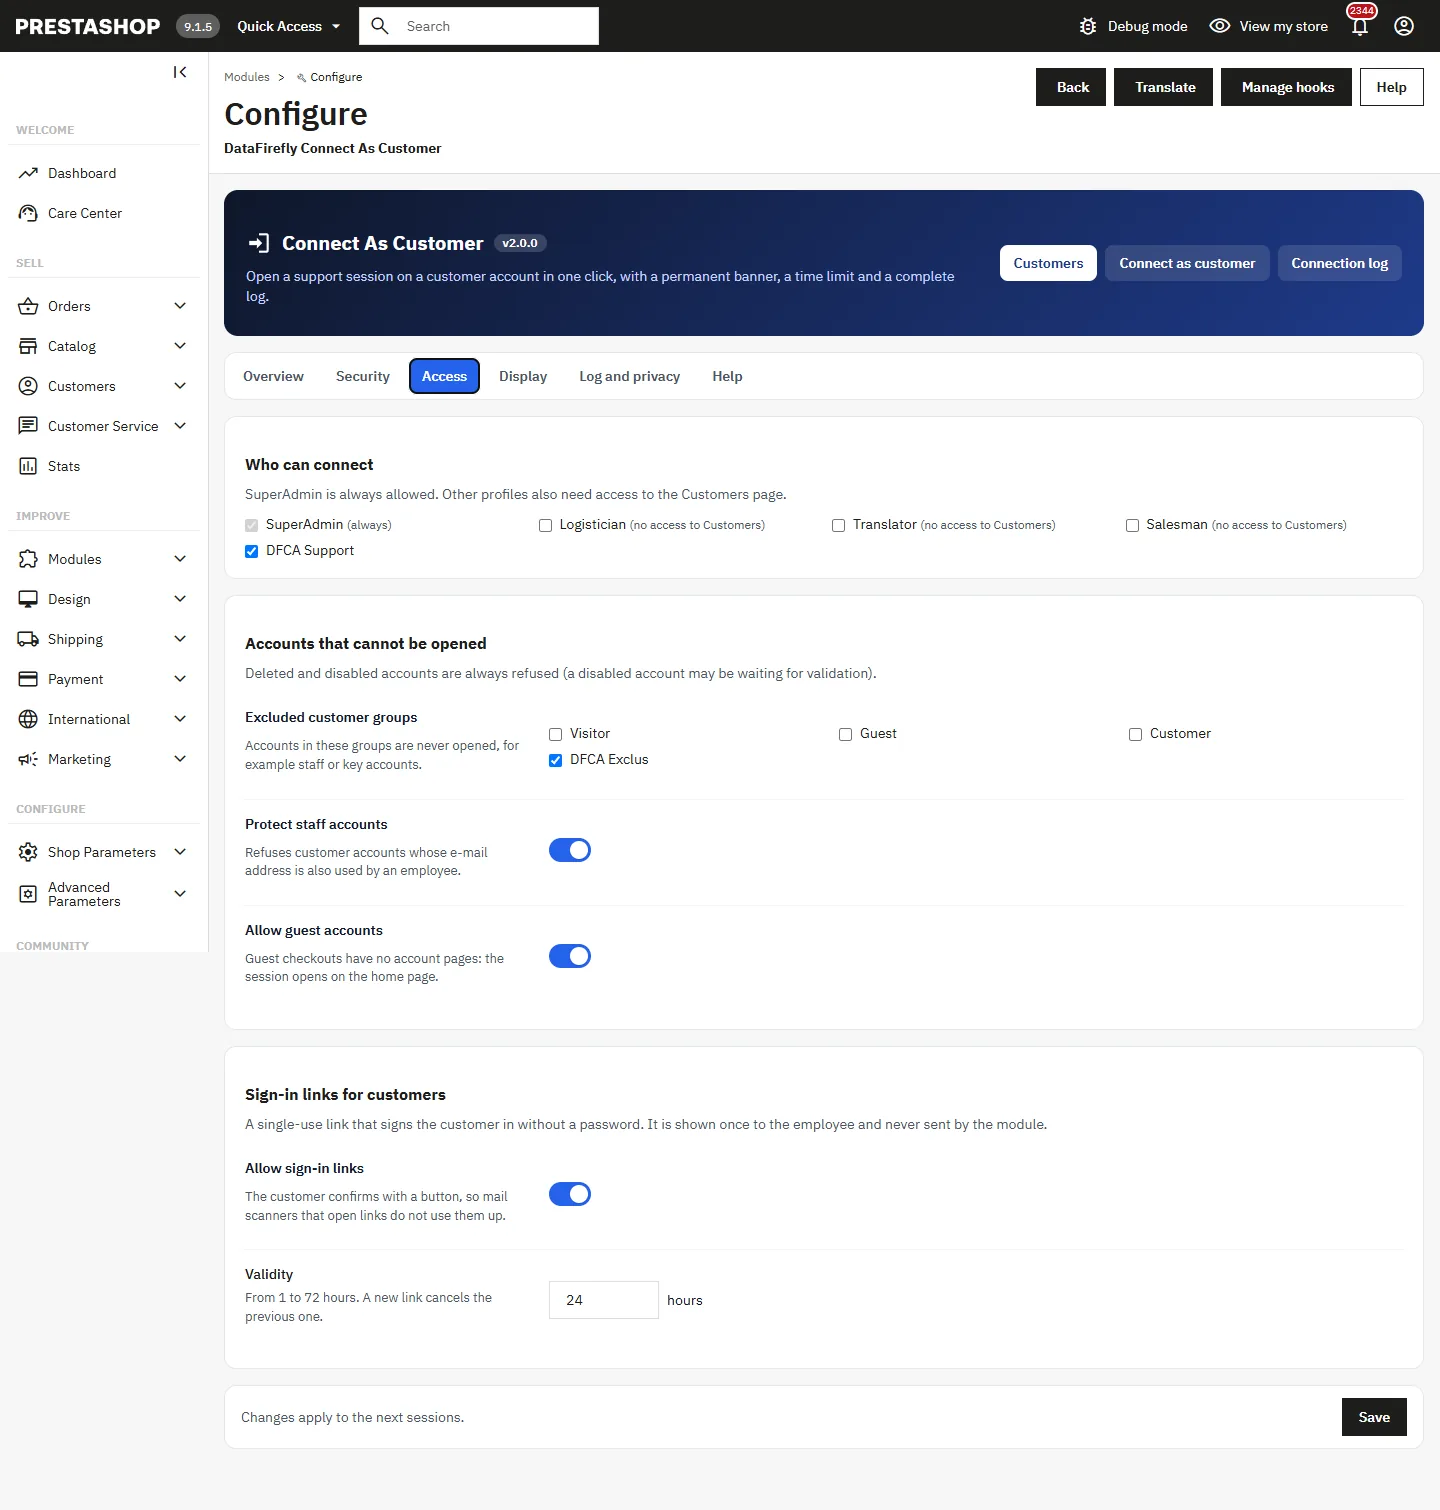
The Access tab chooses the allowed profiles (SuperAdmin always), the customer groups never opened, protection of staff accounts, guest accounts and customer links. Only a SuperAdmin can change the settings.
Connection log
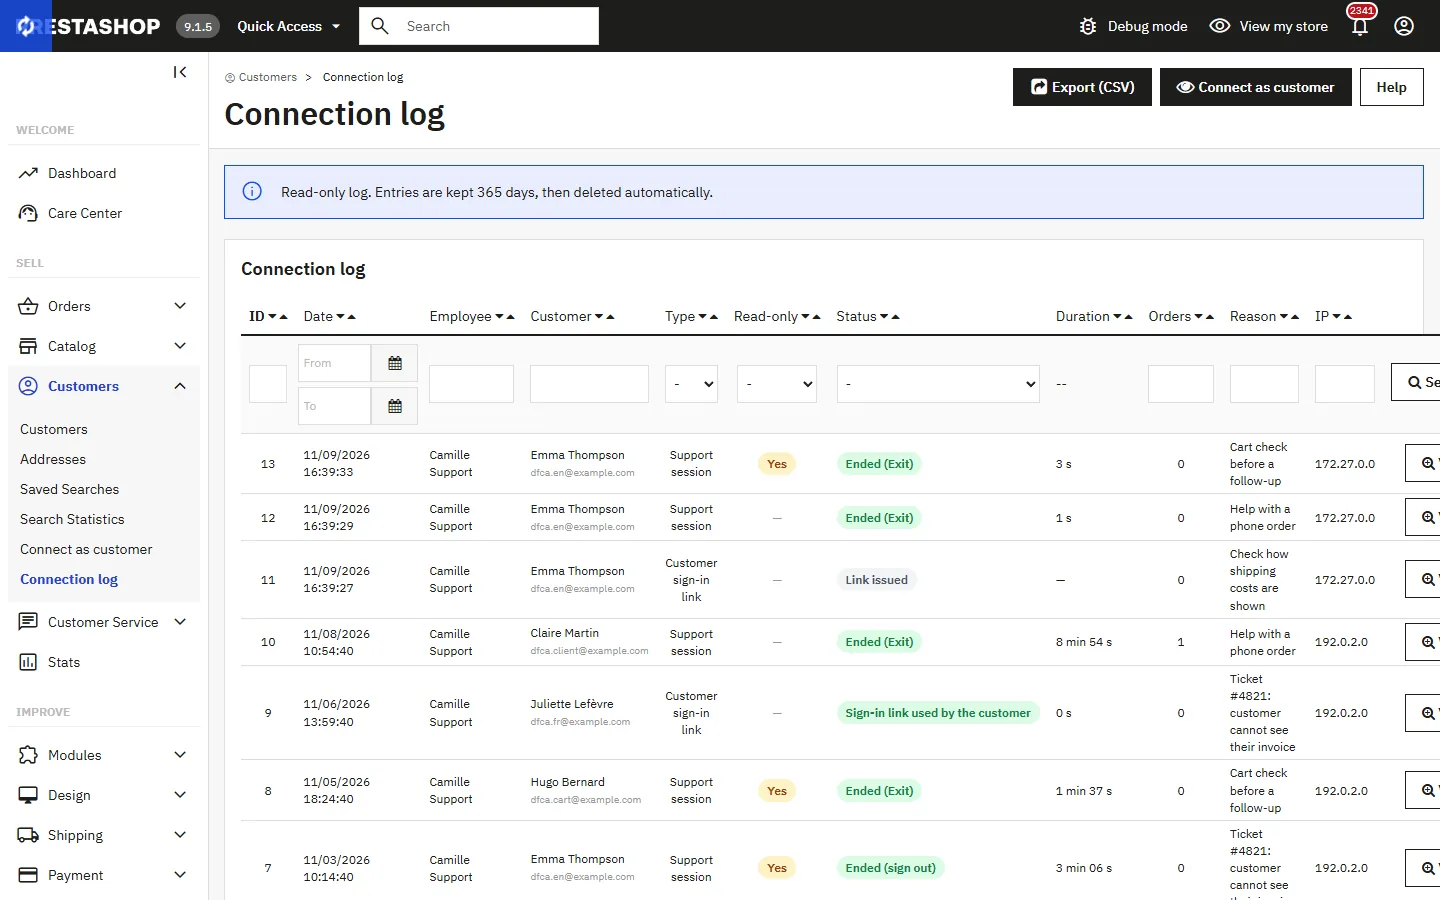
Every link is recorded: employee, customer, reason, read-only, status, duration, orders and IP (masked by default). The log can be filtered, is read-only (no edit or delete from the back office) and is purged automatically after the retention period. The CSV export neutralises formulas for spreadsheets.
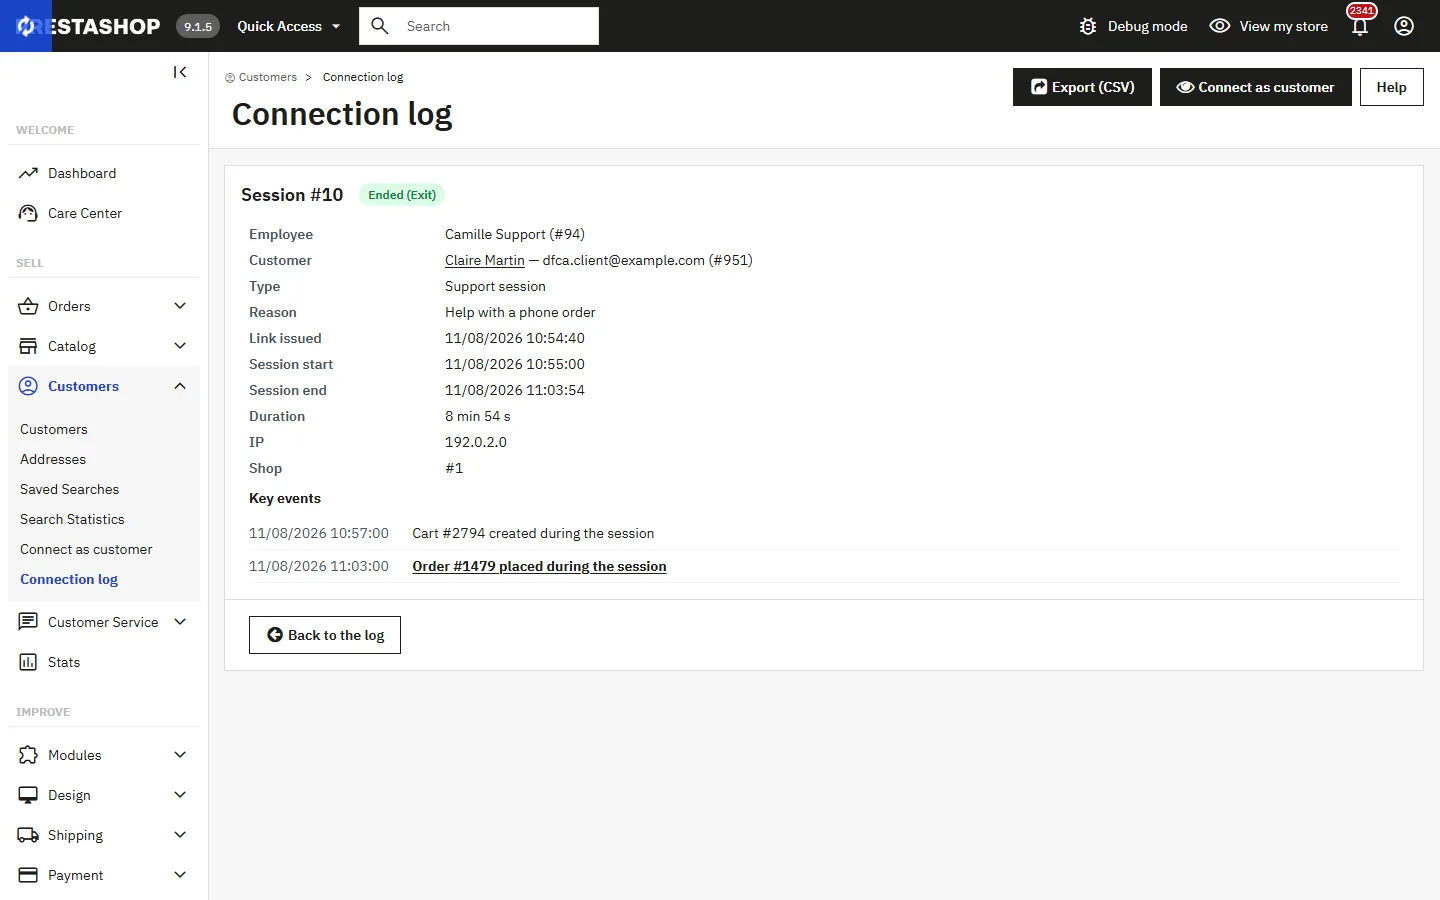
The session detail lists the key events: cart created, order placed, action blocked.
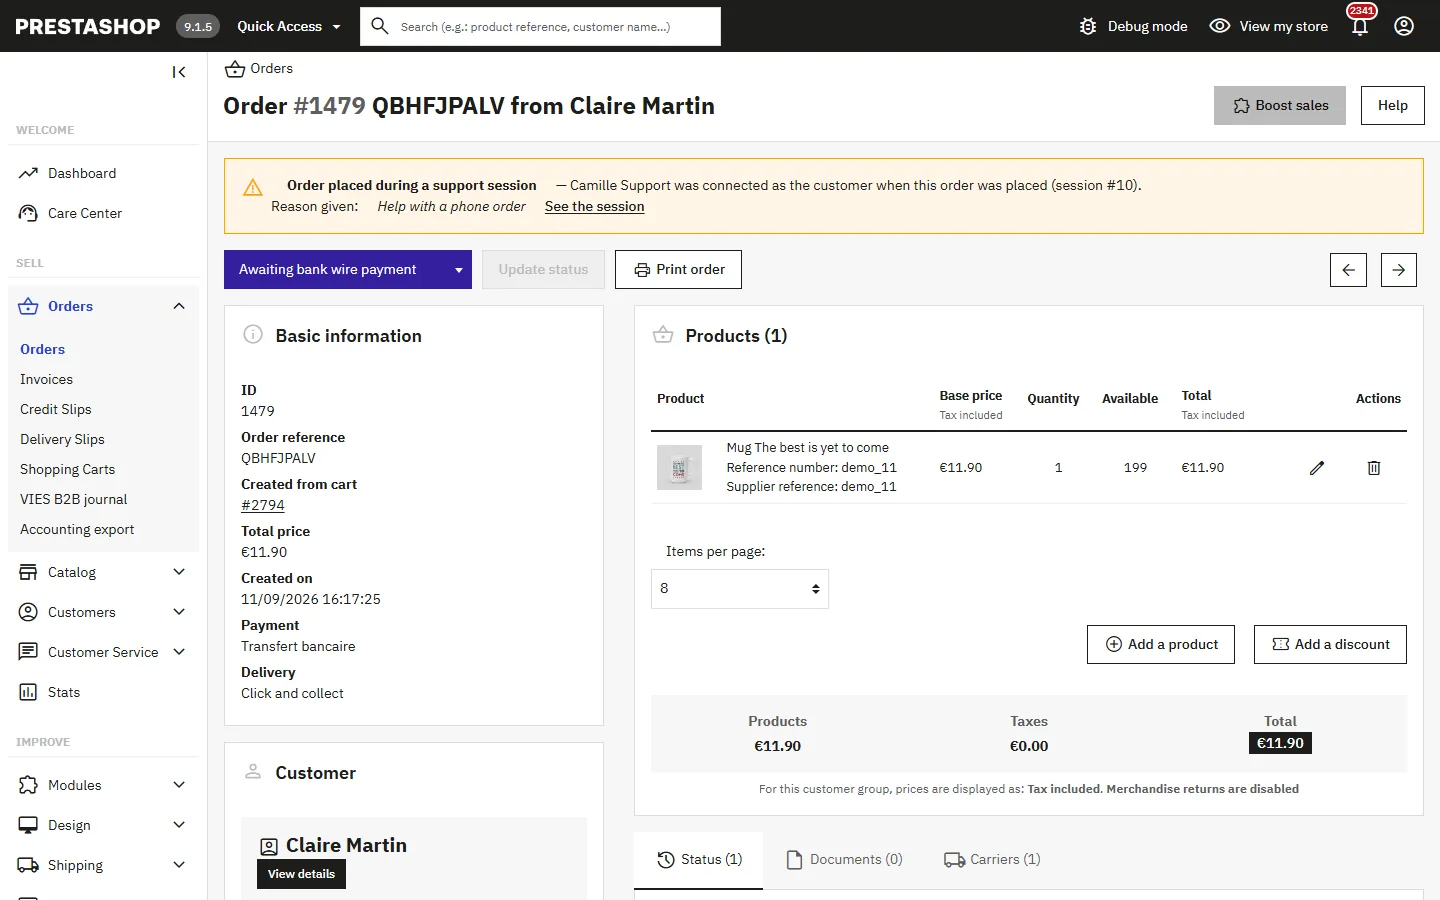
An order placed during a session is flagged at the top of the order page, with the employee, the reason and a link to the session.
Security
- Random single-use link valid for 10 to 60 seconds, stored only as a signed hash (HMAC-SHA256) and bound to the employee, the customer, the shop and the employee’s network.
- Sent in a form, never in a URL; refused when it comes from another site; number of attempts limited per IP address.
- Employee, permissions, shop and back-office session checked again when the session opens and every minute.
- With the DataFirefly 2FA module, an employee whose two-step verification is pending cannot open a customer session.
Troubleshooting
“This link has expired” or “already used”
Start again from the back office: each click creates a new link. On a slow computer, increase the link lifetime (60 seconds at most).
“Link opened from another network”
The back office and the shop see a different IP address (some proxies or CDNs). Turn off Bind links to the employee network in the Security tab.
The button does not show
Your profile is not allowed (Access tab) or cannot view the Customers page. A SuperAdmin can add it.
“Too many attempts”
Too many invalid links were opened from your address: wait 15 minutes or raise the limit in the Security tab.