
Everything you'd want to know before you install.
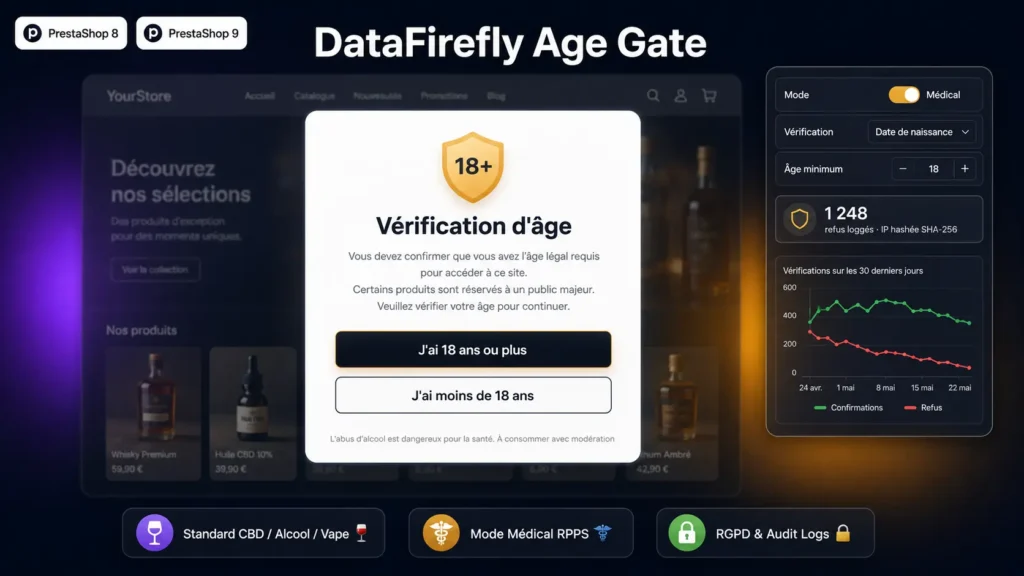
A detailed look at how Age Verification PrestaShop – Blocking Modal for CBD, Alcohol, Vape & Medical works, why we built it the way we did, and the thinking behind the features above.
§ 01
Why a dedicated module rather than a generic popup
Classic marketing popups close with one click, validate nothing, set no compliance cookie, and leave no database trace. For a CBD or alcohol site inspected by regulators, that is a direct non-compliance. For a medical equipment reseller subject to advertising restrictions, that is a risk to your market authorisation. dfagegate does the opposite: genuinely blocking modal (scroll lock, focus trap), server-side validation, SameSite/Secure cookie, logs with hashed IP. It is a compliance tool, not a marketing widget.
§ 02
Standard mode: CBD, alcohol, vape, firearms
For the majority of regulated 18+ markets (or 21+ in certain countries). Three verification types to choose from based on your risk profile: Yes/No buttons (fast, low friction, sufficient for CBD or mainstream alcohol), full date of birth with server-side age calculation via DateTimeImmutable (impossible to bypass via DevTools, recommended for firearms or nicotine liquids), configurable redirect on refusal to a third-party page.
§ 03
Medical mode: compliance with medical device advertising regulations
EU MDR Article 7 and national transpositions restrict advertising of certain medical devices to authorised healthcare professionals. dfagegate materialises the declaration: customisable profession list (doctor, pharmacist, physiotherapist, dentist, veterinarian…), honour declaration checkbox, optional medical licence number validation via regex (9 to 11 digits). The number is never stored — it is used for validation only. This is the spirit of minimum viable compliance: a trace of the declaration, without excessive data collection.
§ 04
Target the regulated department, not the whole store
Since version 1.1.0, the display scope offers three modes. Whole store: legacy behaviour, the modal shows everywhere. Targeted categories: check your categories in a tree with a search filter; the modal shows on those category pages and on the product pages of products belonging to them, sub-categories included when the option is on. Targeted products: search products by name or reference; the modal only shows on their pages. The typical use case: a fine grocery that also sells spirits, an online pharmacy with a professional equipment department. The regulated department is protected, the rest of the store stays friction-free. The decision is made server-side, not in JavaScript.
§ 05
Multi-store and multilingual from install
All configurations (mode, verification type, texts, colours, bypass, display scope) are stored per store context via id_shop_group / id_shop. You can have a CBD store at 18+ in EN and a vape store at 21+ in US within the same PrestaShop, each with its own texts and cookie. Hooks are registered on all stores at install time via Shop::getCompleteListOfShopsID(), avoiding the classic trap of a module that only runs on the current store.
§ 06
Theme robustness: JS injection fallback
The displayBeforeBodyClosingTag hook is supposed to be universal on PrestaShop 1.7.5+, but many custom themes omit it from their layout. dfagegate handles this: the pre-rendered HTML modal is passed to JS via Media::addJsDef. At DOMContentLoaded, the script checks whether the dfagegate-modal element exists in the DOM. If not, it injects it itself via insertAdjacentHTML. Works on any theme without touching the layout. A console.info message confirms whether the fallback activated.
§ 07
GDPR: strictly necessary cookie, hashed IP, automatic retention
The dfagegate_ok cookie falls under the ‘strictly necessary for compliance with a legal access obligation’ category — exempt from prior consent under GDPR, unlike marketing cookies. Its value is binary (1 = confirmed), configurable duration, SameSite=Lax, Secure over HTTPS. Optional refusal logs store a SHA-256 hashed IP (never plaintext). The Logs tab shows statistics (30-day total, breakdown by reason, latest refusals) and retention is automatic: entries older than the configured duration (365 days by default) are purged. Compatible with any existing consent banner.
§ 08
Built-in diagnostic for fast debugging
Once activated, dfagegate adds an HTML comment in the head tag of the type ‘dfagegate v1.1.0 enabled=1 scope=all should_display=1’. If there is a problem, you read it directly in the page source: enabled=0 means the toggle is off, scope shows the active display scope, should_display=0 means a bypass is active or the page is outside the targeted scope. The Test the modal button opens the store in preview mode (?dfagegate_preview=1): the modal shows even if the cookie is set, without setting one. No more private browsing or digging through logs.
There are no reviews yet.