PrestaShop Security & Protection

PrestaShop Security Headers: CSP, HSTS and an A+ Grade Without Server Access

Security headers for PrestaShop, rolled out step by step: a CSP with a nonce on every page, observed in Report-Only before anything is blocked.

  • 30-day refund
  • 12 months updates
  • 24h support

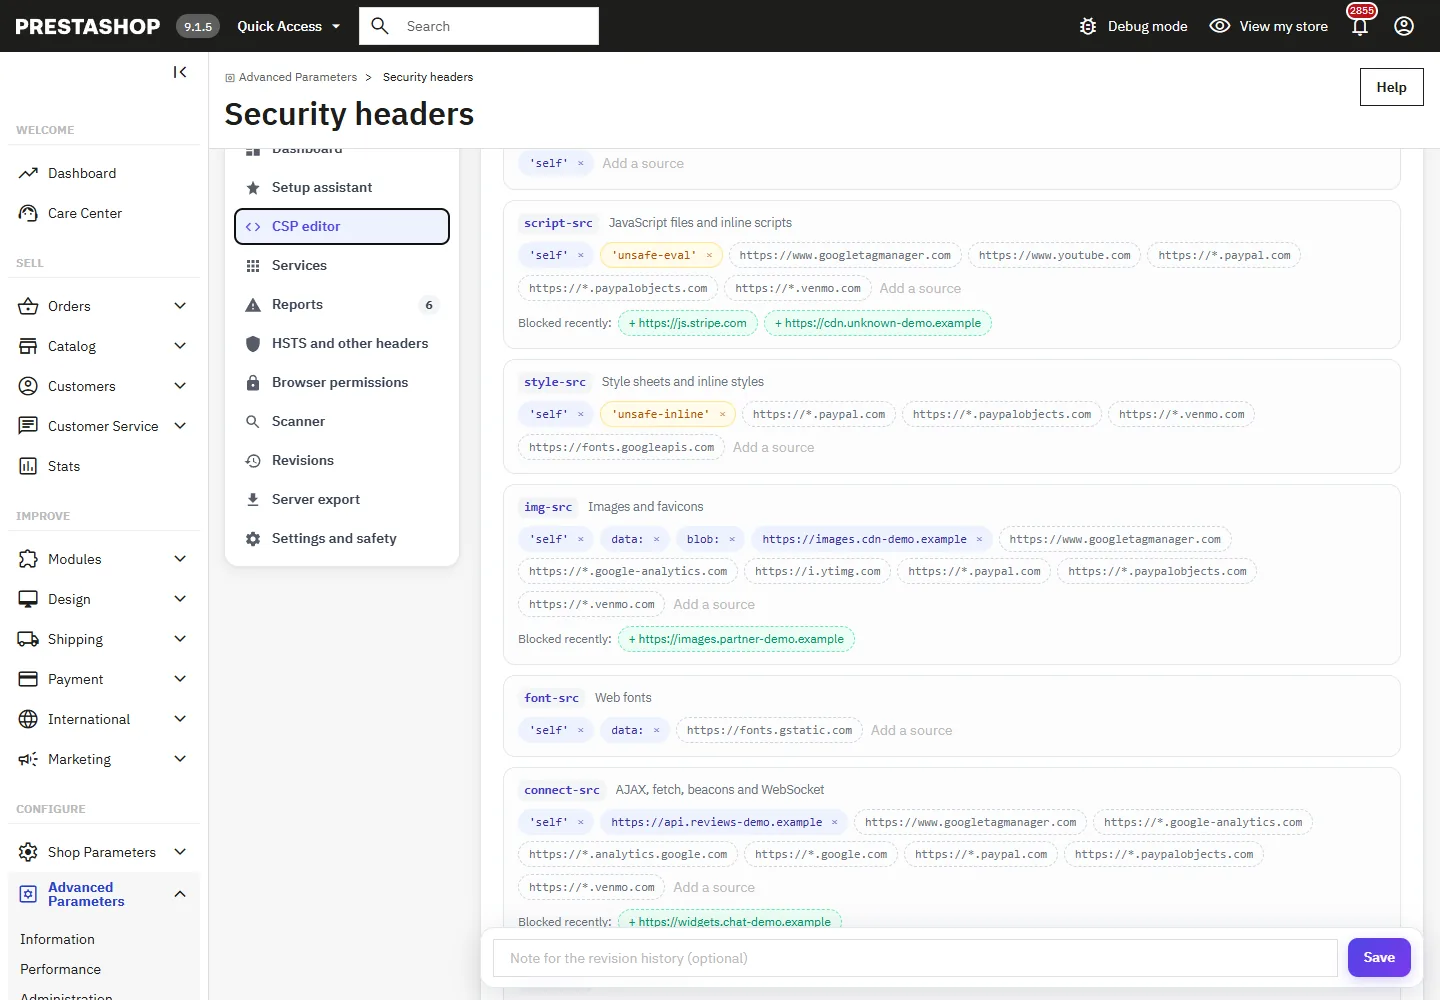
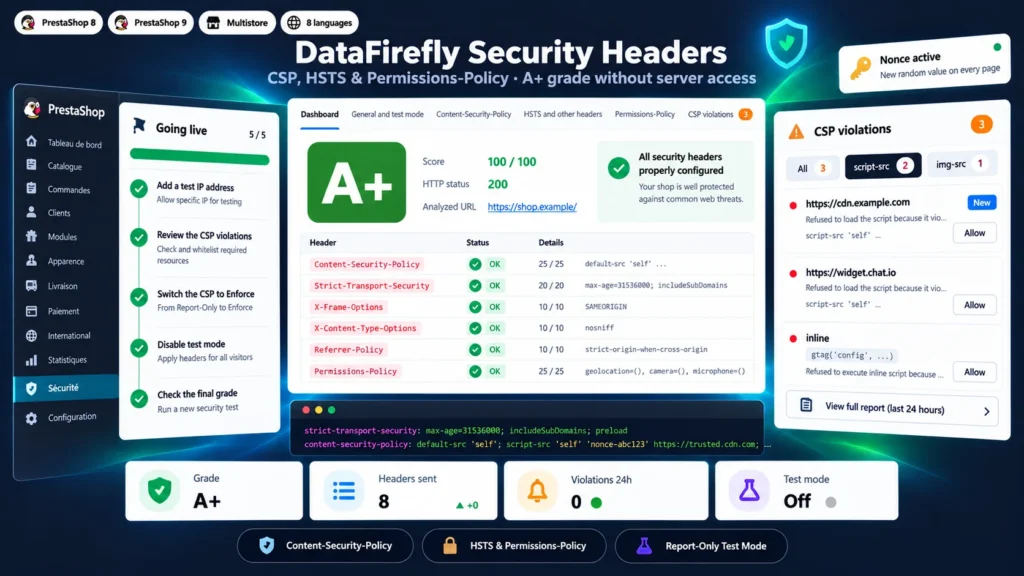
Most PrestaShop shops send almost no HTTP security headers, and writing a Content-Security-Policy that breaks neither the checkout nor the tracking is delicate. This module analyzes the shop, suggests the services to allow from their providers' documentation, and starts an observation period in Report-Only: browsers report what the CSP would block, nothing is blocked. You handle the aggregated reports, then go live with a guided switch and an optional safety net. A random nonce on every page lets the shop's own scripts run without allowing every inline script, and nothing is changed on the server.

At a glance
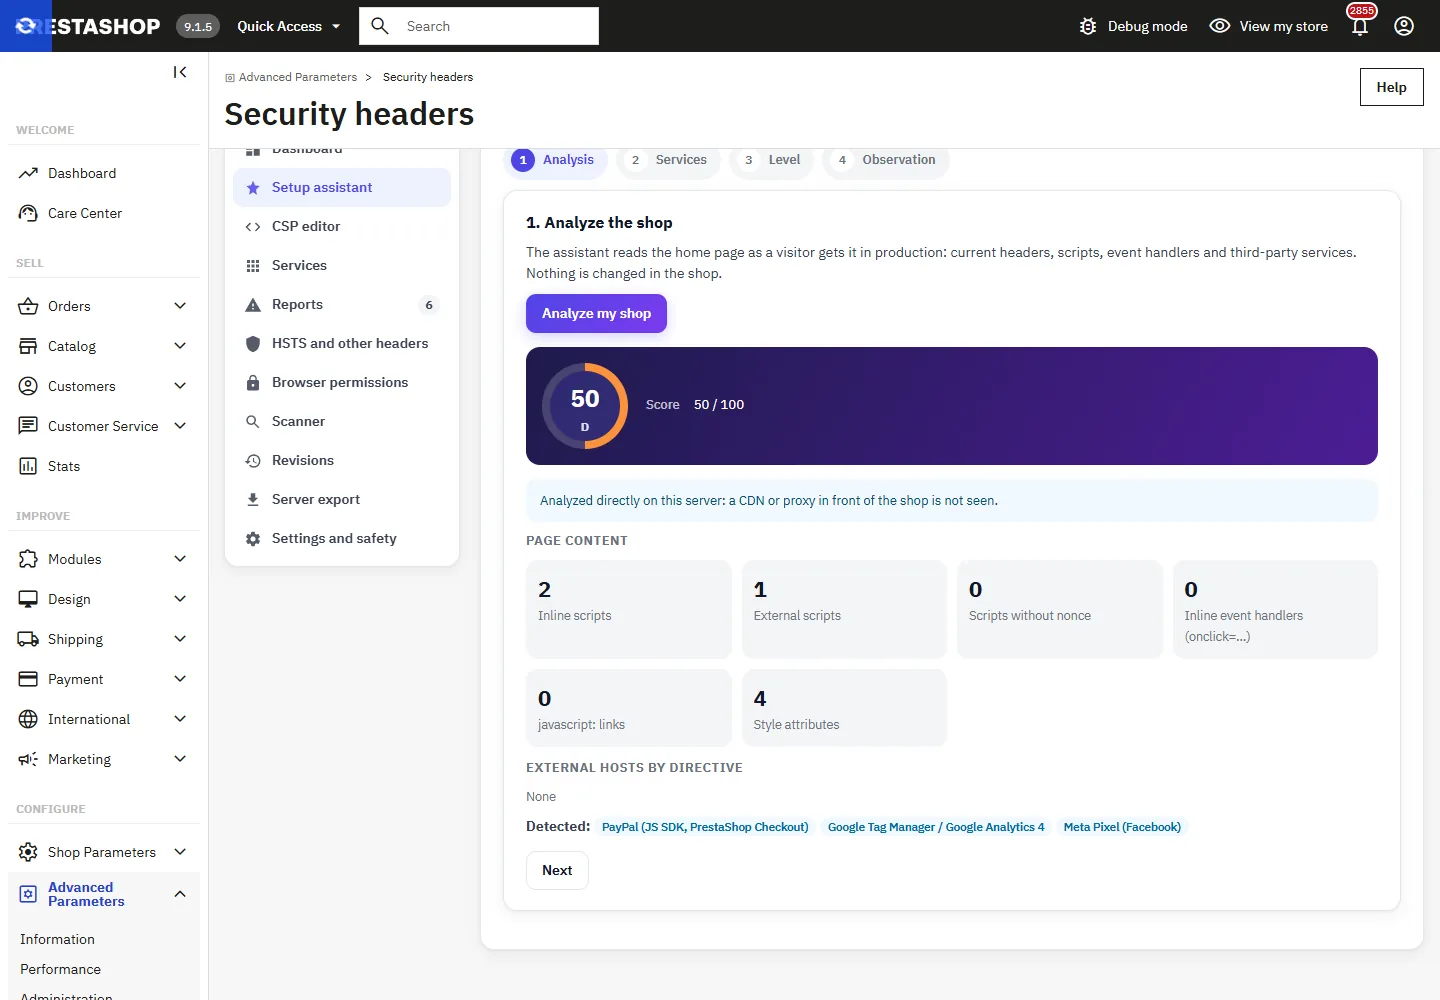
  • Setup assistant: analysis of the shop, services detected, Essential, Recommended or Strict level, Report-Only observation
  • Random nonce on every page, given only to inline scripts and allowed hosts, with a reflection guard
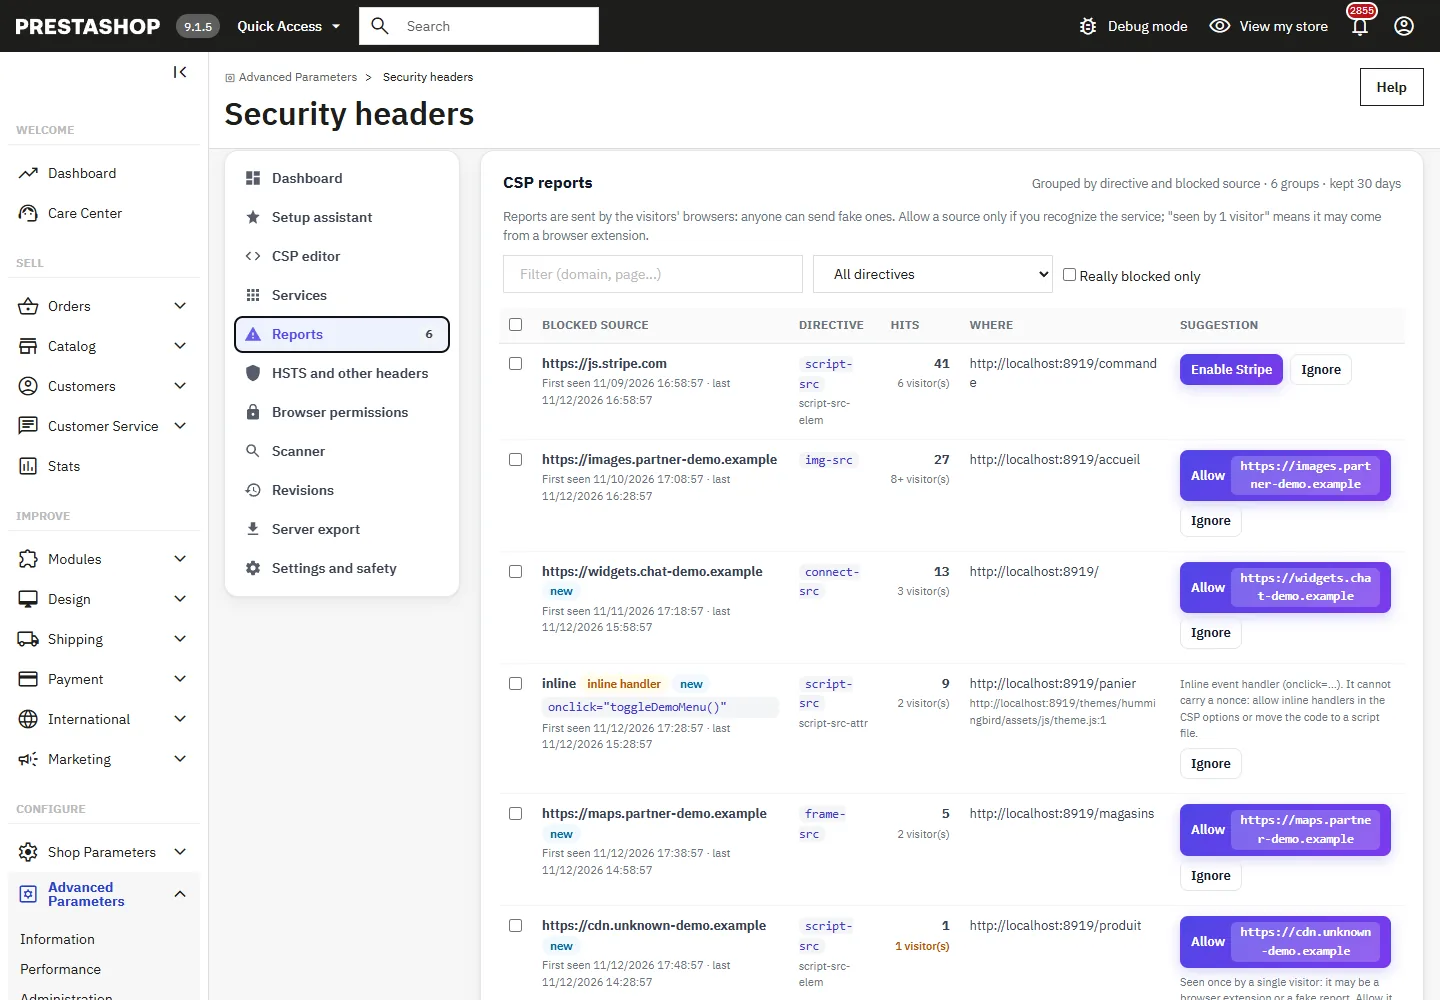
  • Aggregated CSP reports with distinct visitors and one-click allow, behind a rate-limited endpoint
  • HSTS with guarded preload, X-Frame-Options, Referrer-Policy, Permissions-Policy, COOP/COEP/CORP with warnings
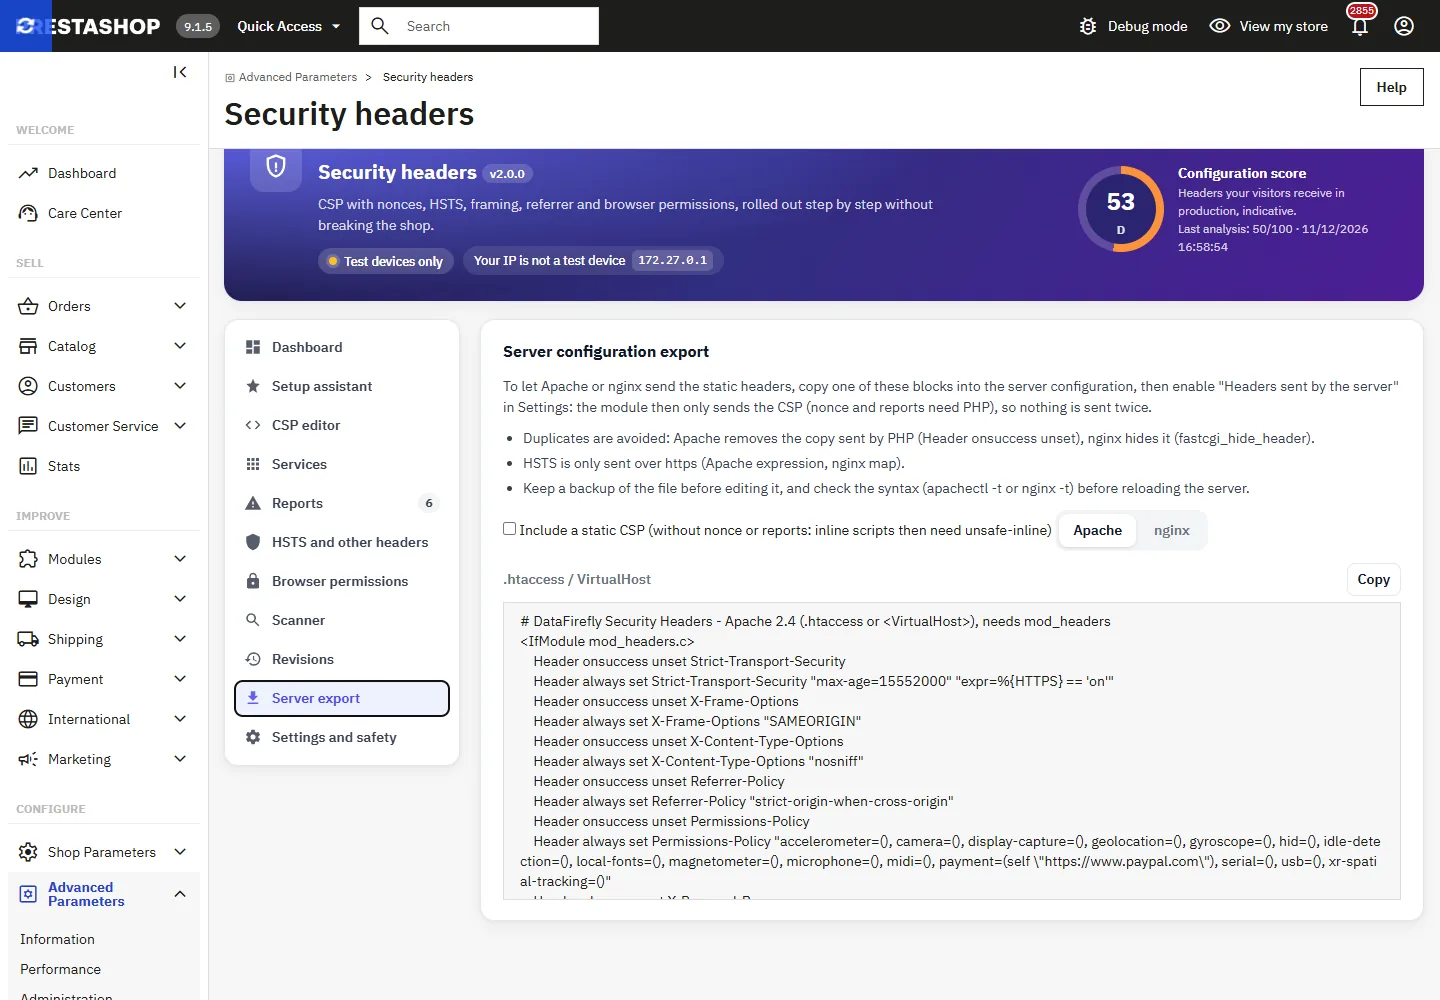
  • Revisions with comparison and one-click rollback, Apache/nginx export without duplicates, emergency stop
PrestaShop 8 & 9 Content-Security-Policy A+ grade No .htaccess
  • PrestaShop Certified Agency 2026
  • PrestaShop Expert Certification — Core Skills
  • PrestaShop Expert, level 3

Built by a PrestaShop Certified Agency

PrestaShop Security Headers: CSP, HSTS and an A+ Grade Without Server Access
v2.0.0 · updated 2026-11-12
PrestaShop Security Headers: CSP, HSTS and an A+ Grade Without Server Access €99.00
What it does

Overview PrestaShop Security Headers

01

Observe before blocking

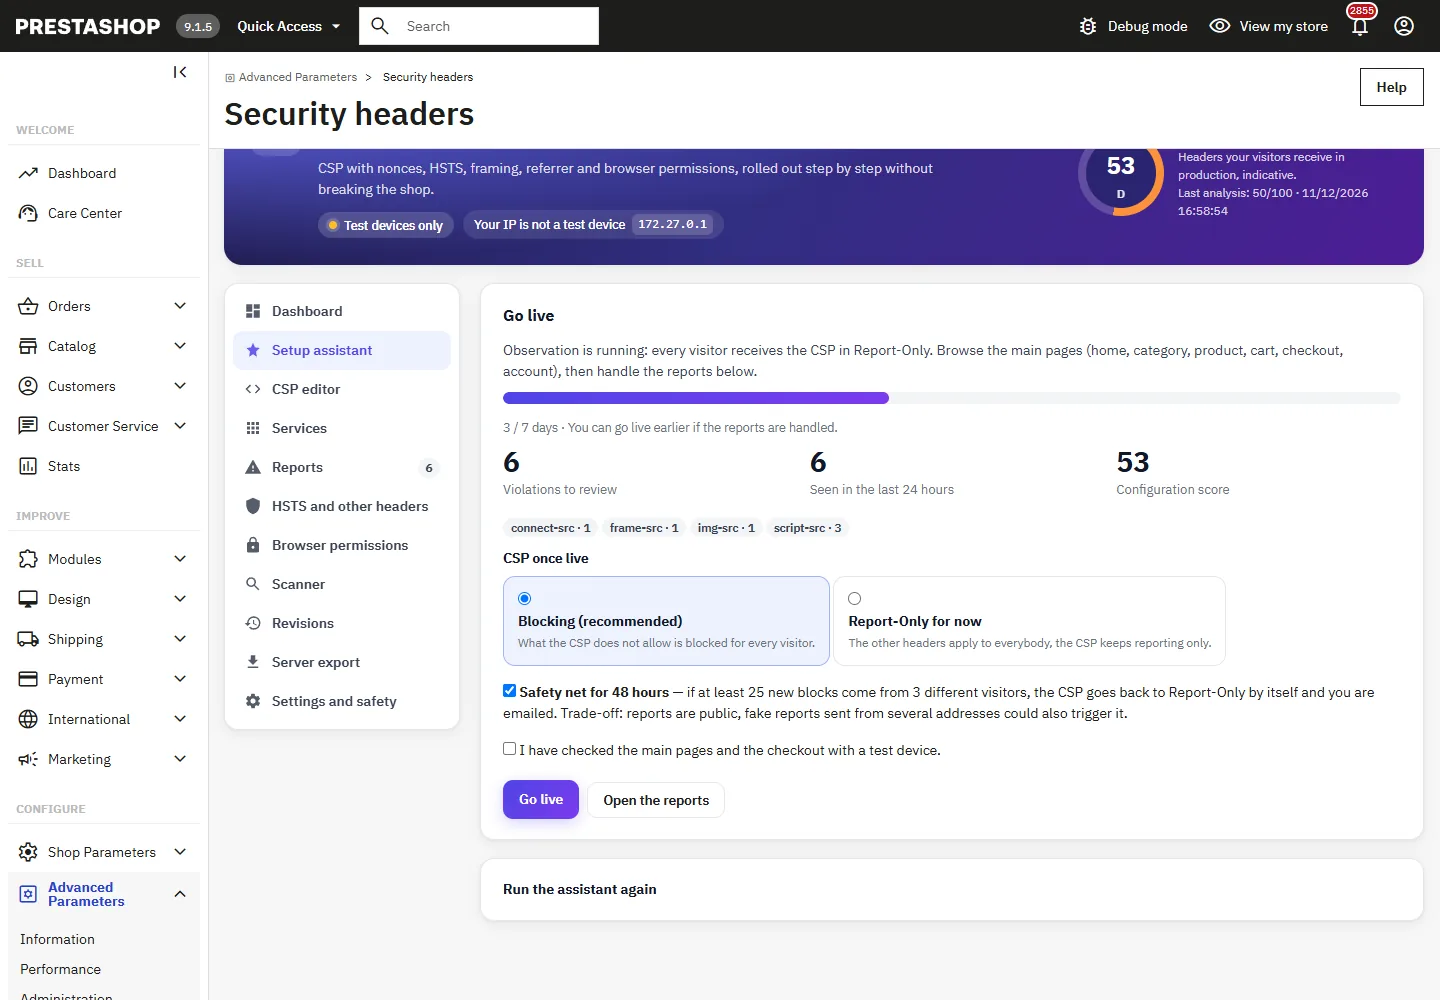
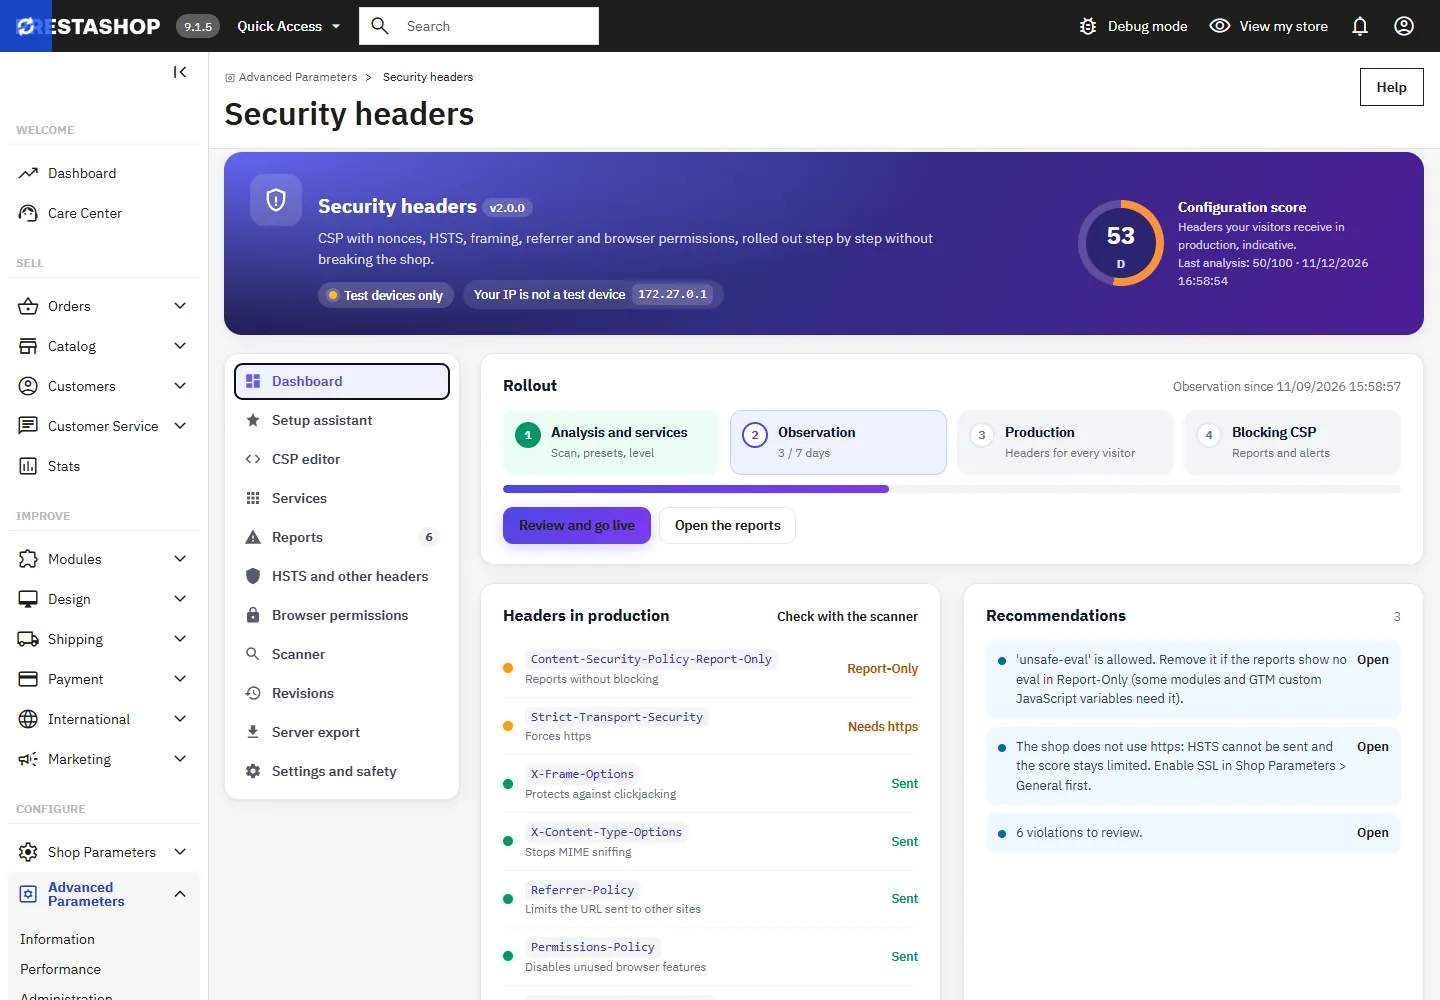
The assistant reads the home page, detects the third-party services and your modules, and starts a 3 to 30 day observation: every visitor receives the CSP in Report-Only, or nothing at all if you prefer to test on your own devices only. The other headers are only sent to your test devices until you go live.

02

A nonce that is not a blank cheque

A new random nonce is added on every page to the scripts written by the shop and to scripts from allowed hosts only. A script tag from an unknown host, or whose text comes from the URL or a form of the request, does not get it. The HTML is read with a real tokenizer, so "<script" inside a JavaScript string is left alone.

03

Reports you can act on

Reports are grouped by directive and source, with hits, blocks, distinct visitors, the page and the script involved. A domain known to a service enables that service, another one is allowed in one click; inline code and eval come with the right fix instead. The public endpoint is rate-limited and drops reports about other sites.

04

A go-live you can undo

The switch to blocking is guided, with an optional 48-hour safety net that goes back to Report-Only by itself if new blocks hit several visitors. Every change is a revision you can compare and restore in one click, and an emergency stop works even without access to the back office.

The long version

Everything you'd want to know before you install.

A detailed look at how PrestaShop Security Headers: CSP, HSTS and an A+ Grade Without Server Access works, why we built it the way we did, and the thinking behind the features above.

§ 01

Why a CSP is delicate on a shop

A Content-Security-Policy decides which scripts, styles, images and frames a page may load. Too loose, it lets an injected script run; too strict, it blocks the payment form, the tracking or the chat. PrestaShop themes and modules also print inline scripts, which a strict policy forbids. The module therefore starts from a policy compatible with the shop and lets the browsers tell you what it would block before anything is blocked.

§ 02

Observation first

The setup assistant analyzes the home page, pre-selects the services it detects and starts an observation period in Report-Only. Your visitors' browsers report what the policy would block, the reports are grouped by directive and source, and each one comes with a suggestion: enable the matching service, allow the domain, or the right fix for inline code. Your own devices, declared by IP or through a test link, already get the blocking policy.

§ 03

What the nonce does, and what it does not

A new random nonce is added on every page to the scripts written by the shop and to scripts from allowed hosts, and unsafe-inline is removed from script-src. A script from an unknown host, or a script tag whose text comes from the request, does not get it. Its limit is stated in the back office: a script stored in the database, for example in a product description, is part of the page and gets the nonce, which is why PrestaShop's HTMLPurifier option should stay on.

§ 04

Going live, and coming back

When the reports are handled, the assistant switches the CSP to blocking for every visitor. An optional safety net watches the next 48 hours and goes back to Report-Only by itself if new blocks hit several visitors. Every change is a revision with its author and an optional note, comparable and restorable in one click, and an emergency stop by file, constant or command line works even if the back office is unreachable.

§ 05

From PrestaShop or from the server

Headers are sent by PHP at the very start of each request, with no server change. If you prefer the server to send the static ones, the module generates Apache and nginx blocks that remove the copies sent by PHP and only send HSTS over https, then keeps sending only the CSP. The scanner checks the result on the shop's own pages and flags duplicates and version leaks; its score is indicative and public scanners may grade differently.
€99.00
One-time · 12 months updates
Read the docs
  • Unlimited dev & staging installs
  • Source code included
  • 30-day refund
  • 24h support · EN / FR
5.0/5 25 reviews
All customer reviews